PHP 8.5.12 fixes two critical pre-auth RCEs: update now
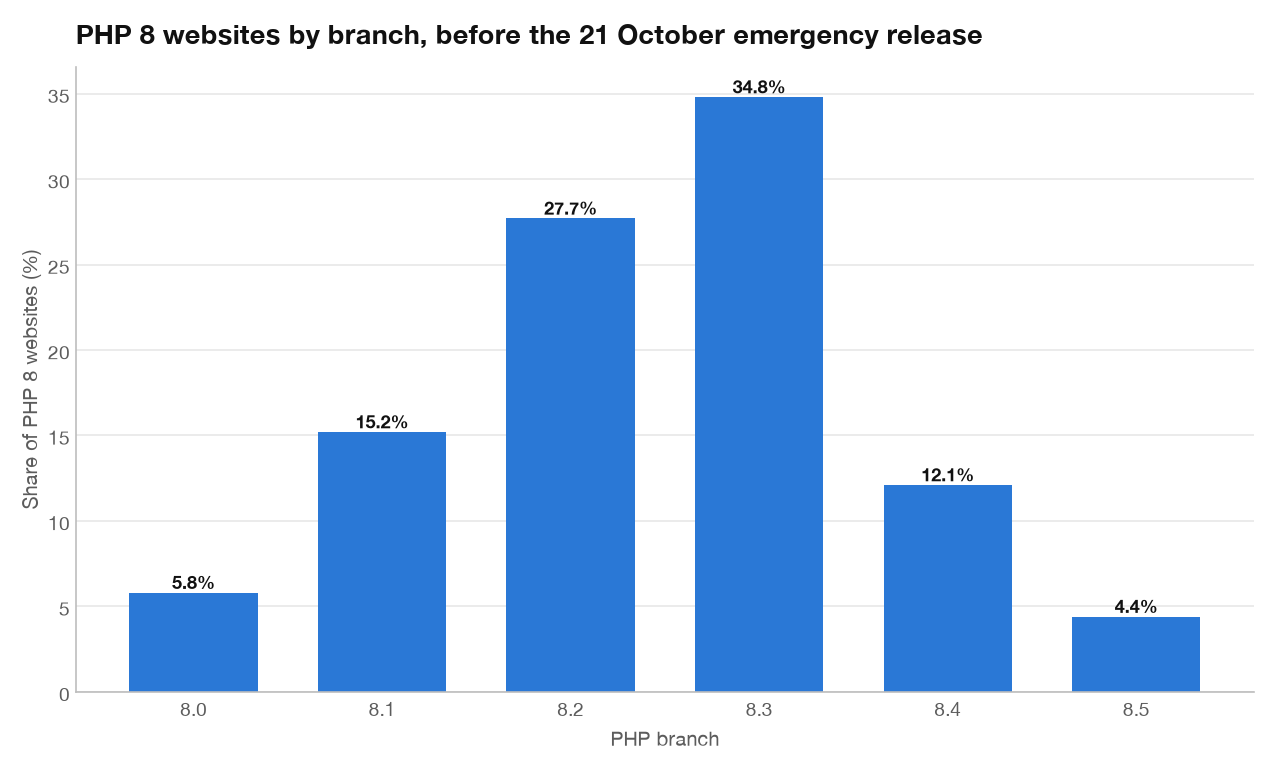
Two PHP flaws rated 9.2, CVE-2026-109618 and CVE-2026-109619, allow unauthenticated RCE before your code runs. Fixed in PHP 8.5.12 and 8.4.27.
61 stories tagged cybersecurity.
Two PHP flaws rated 9.2, CVE-2026-109618 and CVE-2026-109619, allow unauthenticated RCE before your code runs. Fixed in PHP 8.5.12 and 8.4.27.
Gemini 4 Argon is Google's new frontier AI with a 1 million token output limit and top coding and cybersecurity scores. Here is what beginners should know.
CVE-2026-76504 is a CVSS 9.8 authentication bypass in Cisco Catalyst SD-WAN Manager, exploited in the wild since September 2026. CISA gave federal agencies until October 3 to patch. Here is what to check and how to fix it.
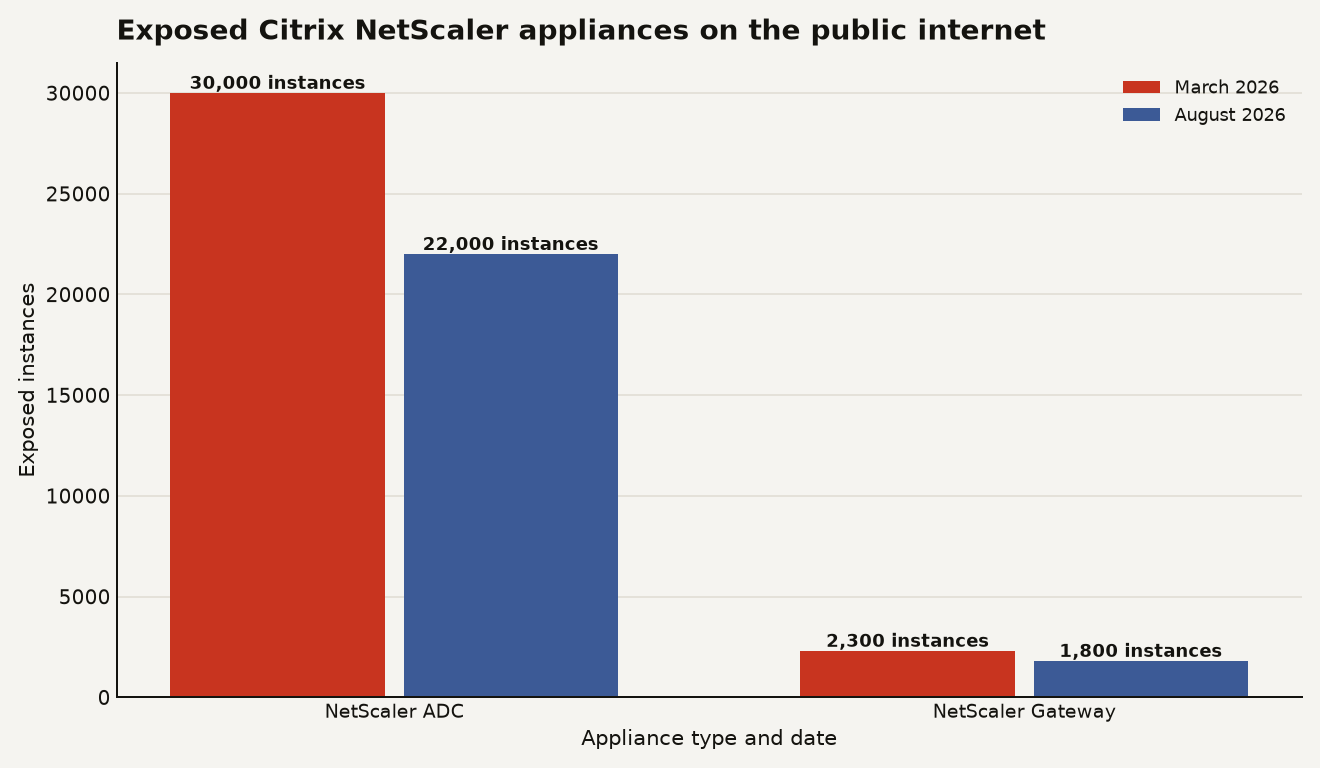
With no fix available for two exploited Citrix NetScaler RCE zero-days, operators must isolate or shut down appliances before Monday.
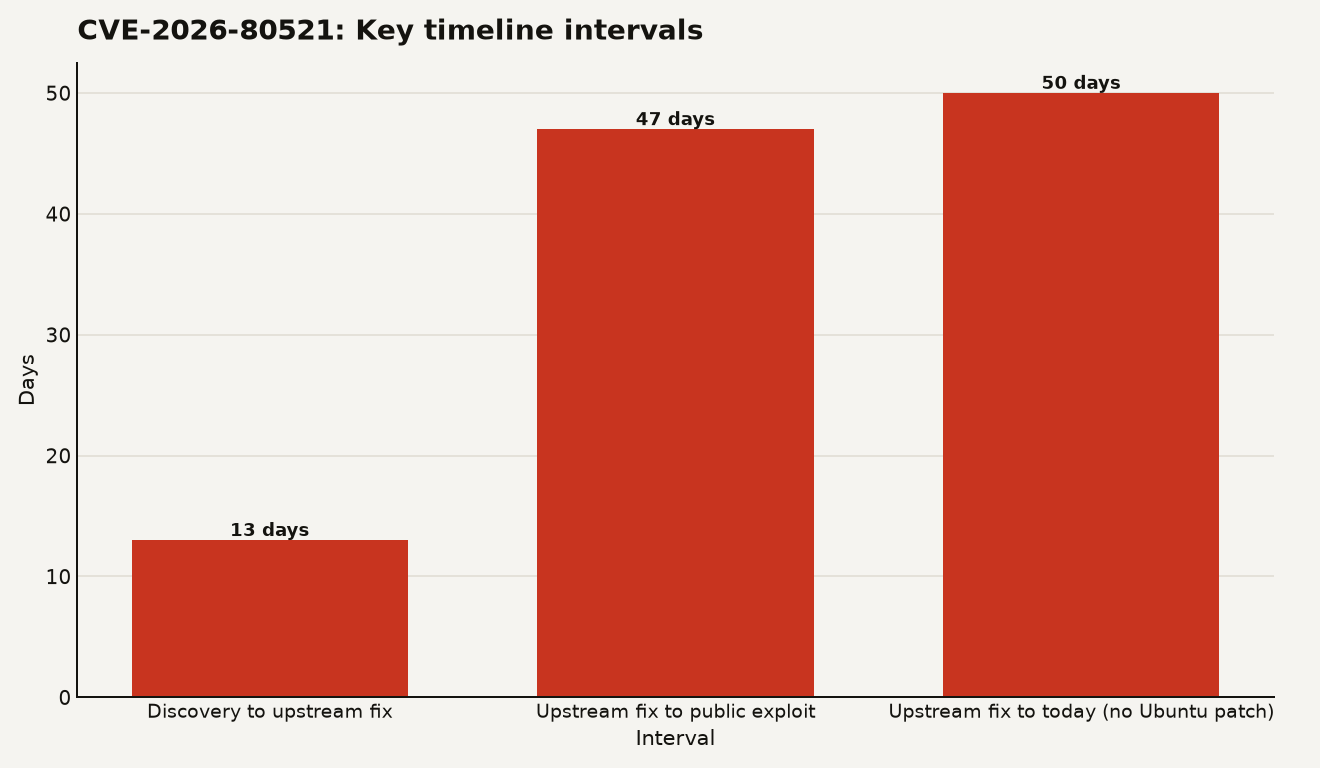
CVE-2026-80521 enables a container escape to host root via a Linux kernel use-after-free. Ubuntu has no LTS patch 50 days after the upstream fix.
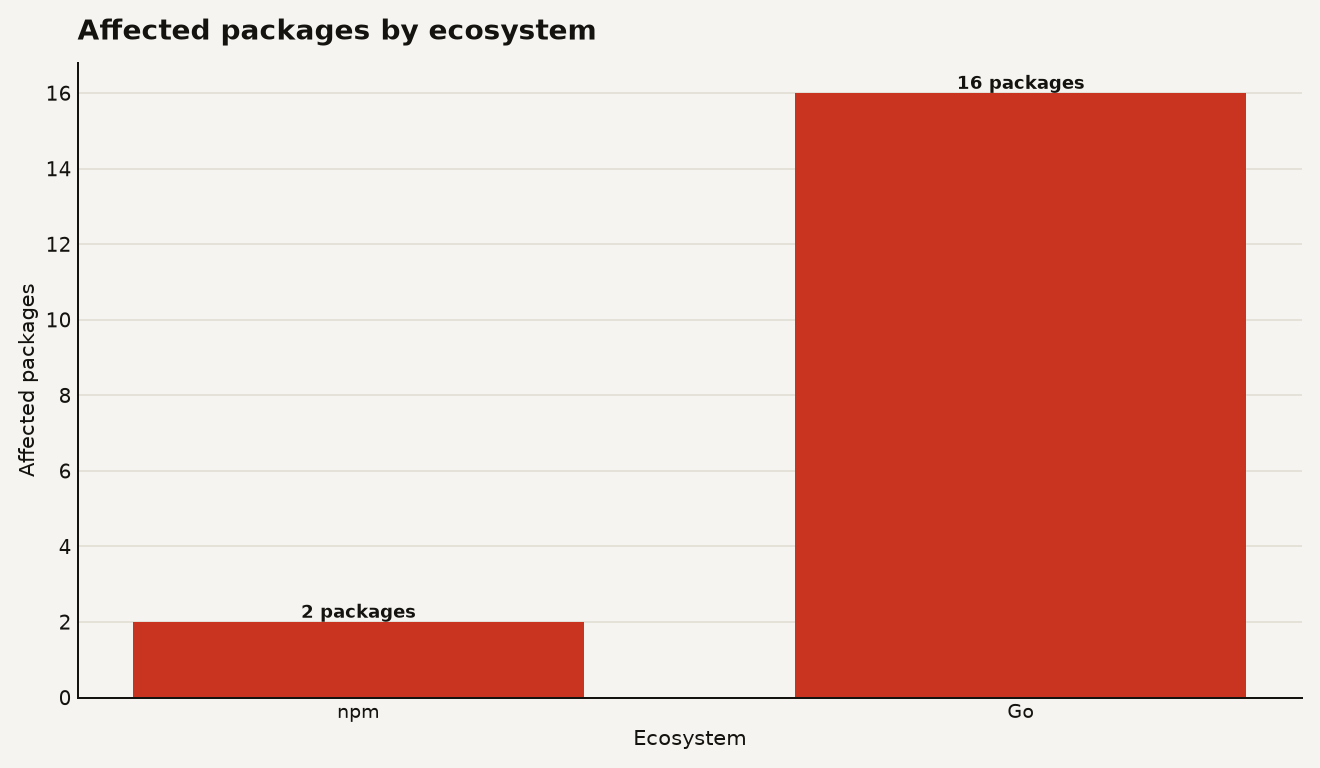
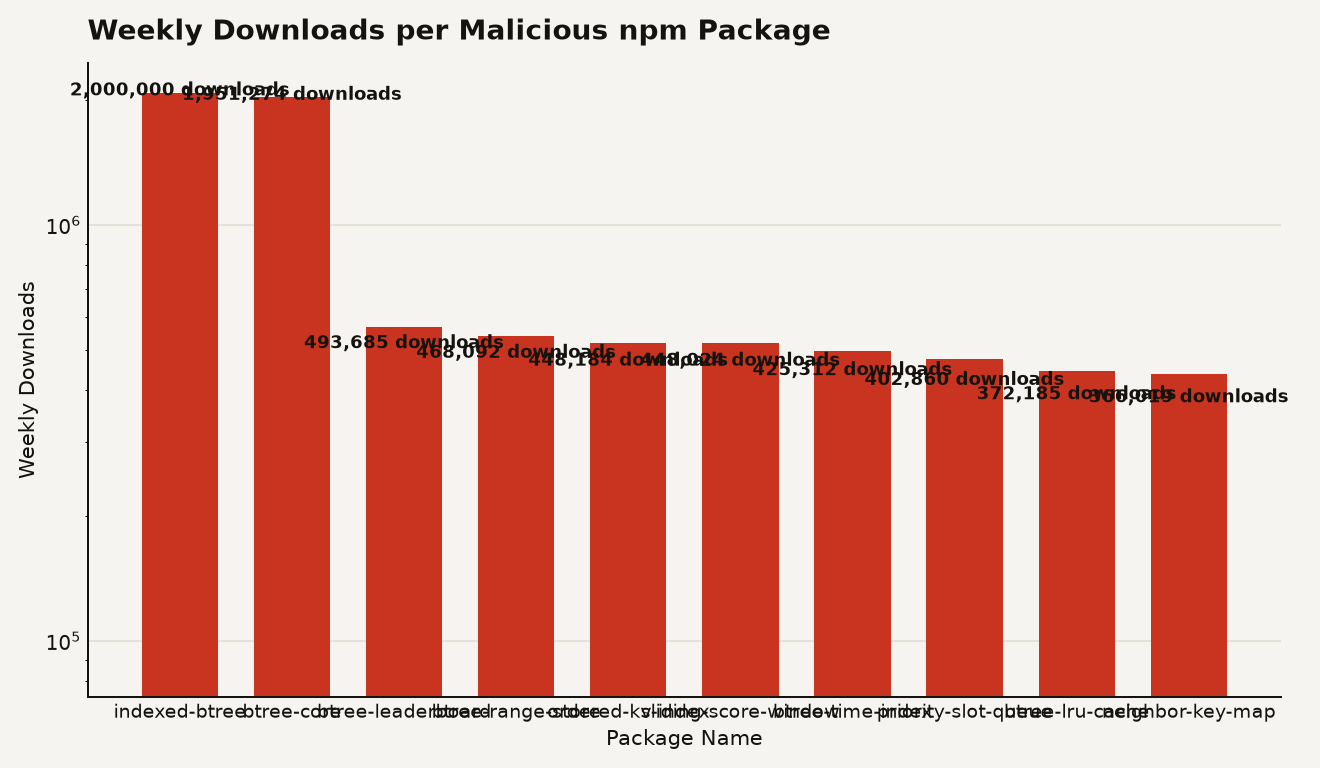
An npm supply chain attack hides malware in runtime methods, bypassing npm v12 install-script blocks. Ten packages and 7 million downloads are affected.
North Korea's WaterPlum hacking group compromised at least 30,000 devices in over 100 countries via fake job interviews, stealing $10.7 million in cryptocurrency. The campaign weaponizes npm packages and VS Code projects against software developers.
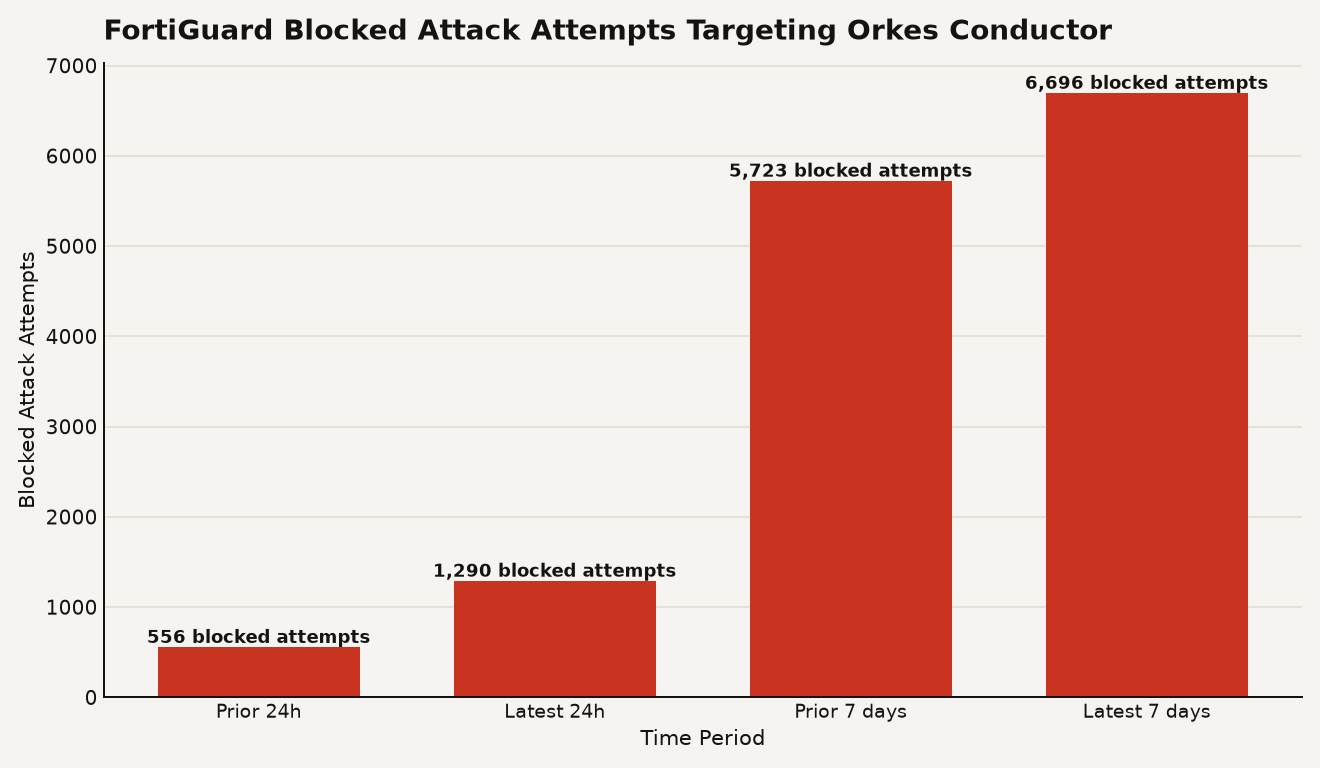
Exploited since August 2026, Orkes Conductor CVE-2026-58138 is a CVSS 9.8 unauthenticated RCE in GraalVM script evaluators. Upgrade to 3.30.2.
An AI coding assistant hijack at a SaaS provider let attackers spread the Shai-Hulud worm across 100 repositories, stealing secrets and proprietary source code.
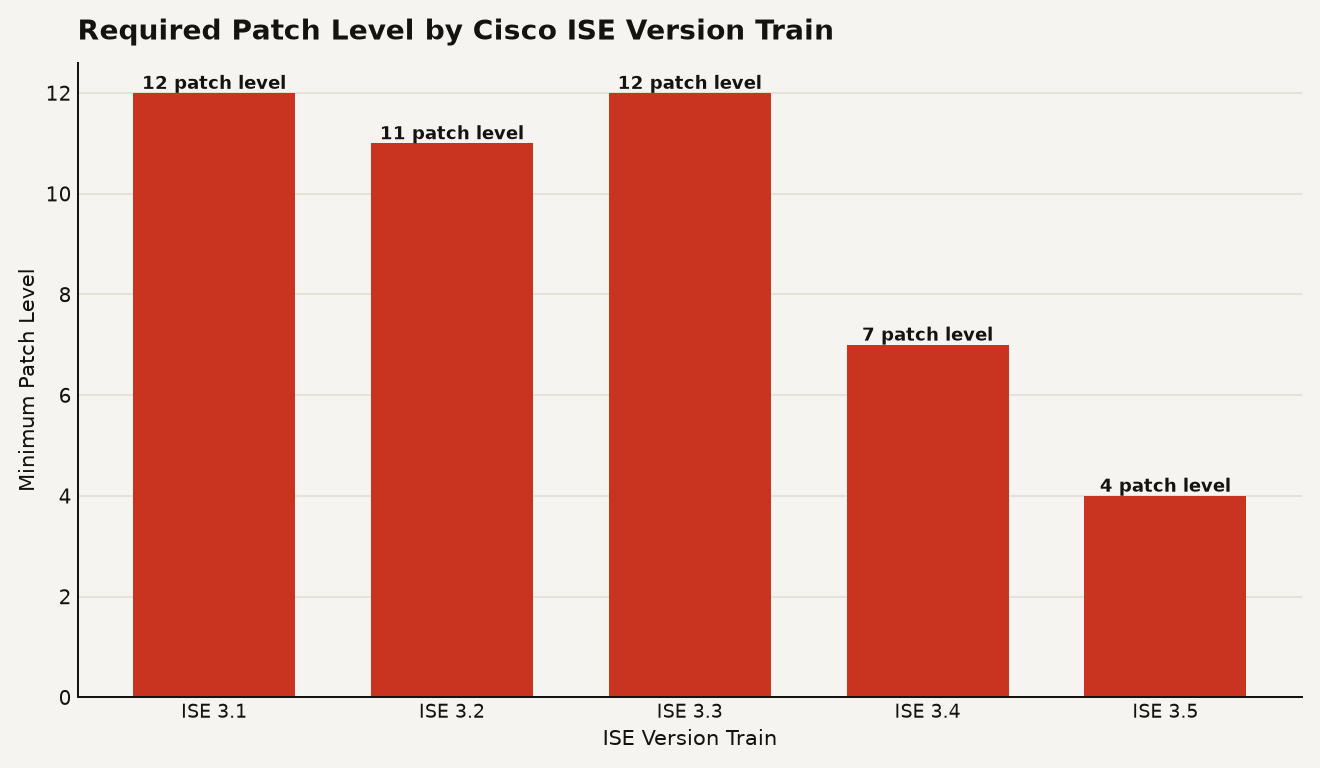
Attackers are exploiting CVE-2026-76460, a CVSS 10.0 auth bypass in Cisco ISE and ISE-PIC. CISA gave federal agencies three days to patch.
CISA confirmed active exploitation of CVE-2026-76461, a root-level SQL injection in Cisco Secure Email Gateway, and set a 3-day patch deadline.
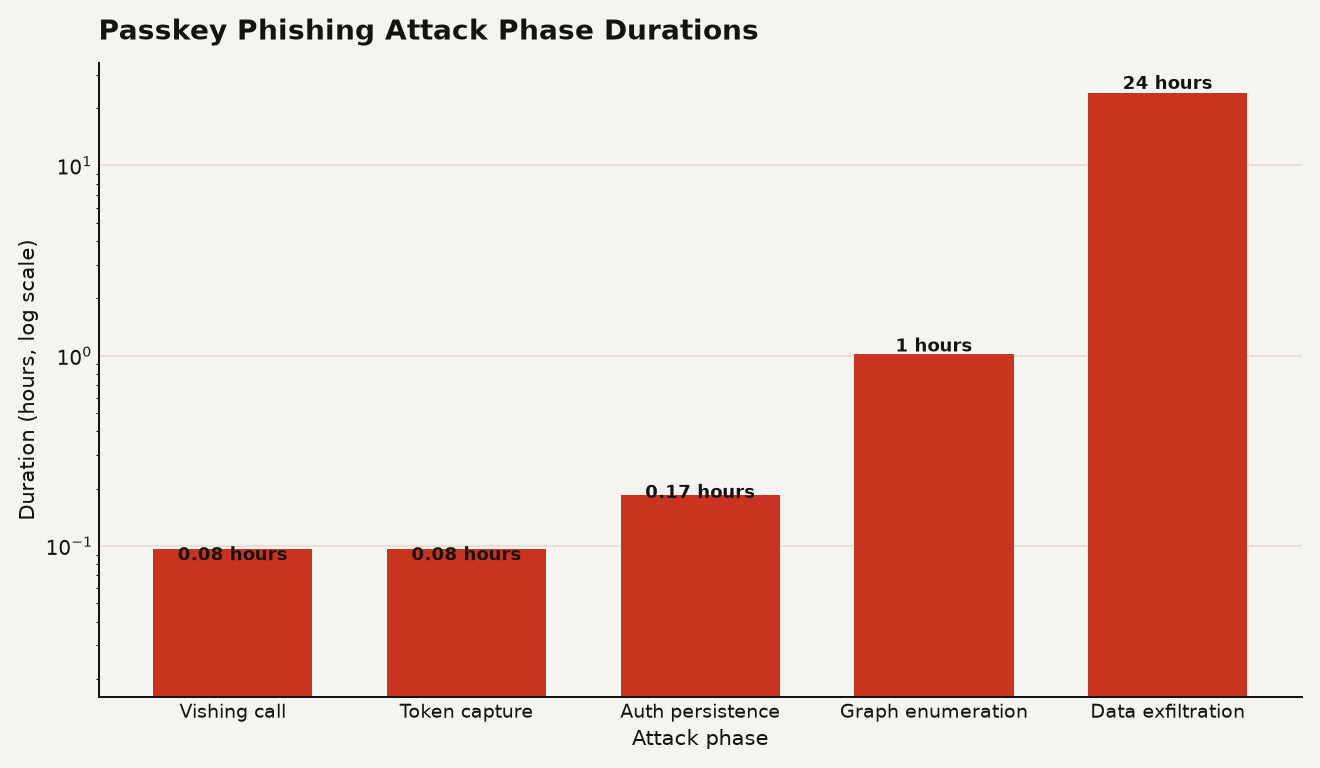
Vishing calls themed around passkeys are hijacking Microsoft 365 accounts; attackers steal session tokens and exfiltrate data over days.
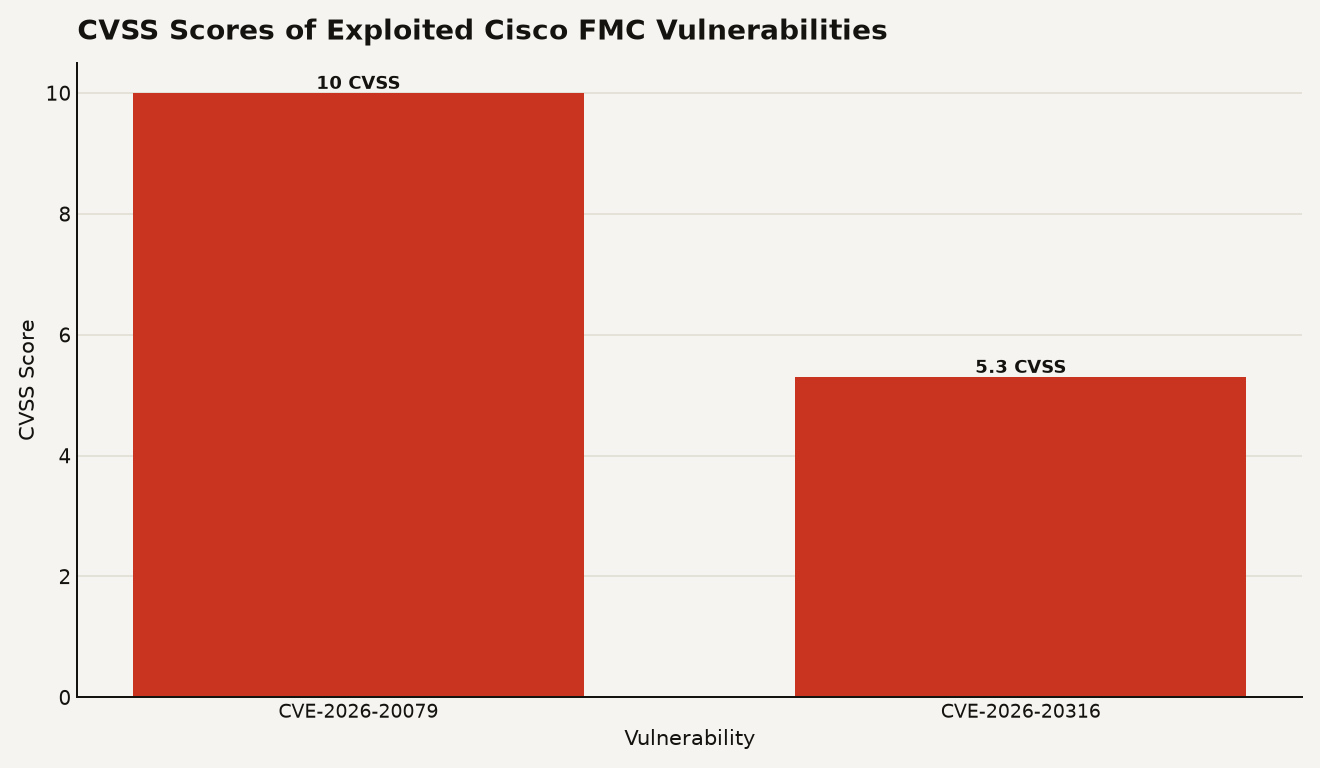
Cisco FMC CVE-2026-20079 lets unauthenticated attackers gain root on firewall managers. Three threat clusters are exploiting it, including Qilin ransomware and suspected Sandworm activity.
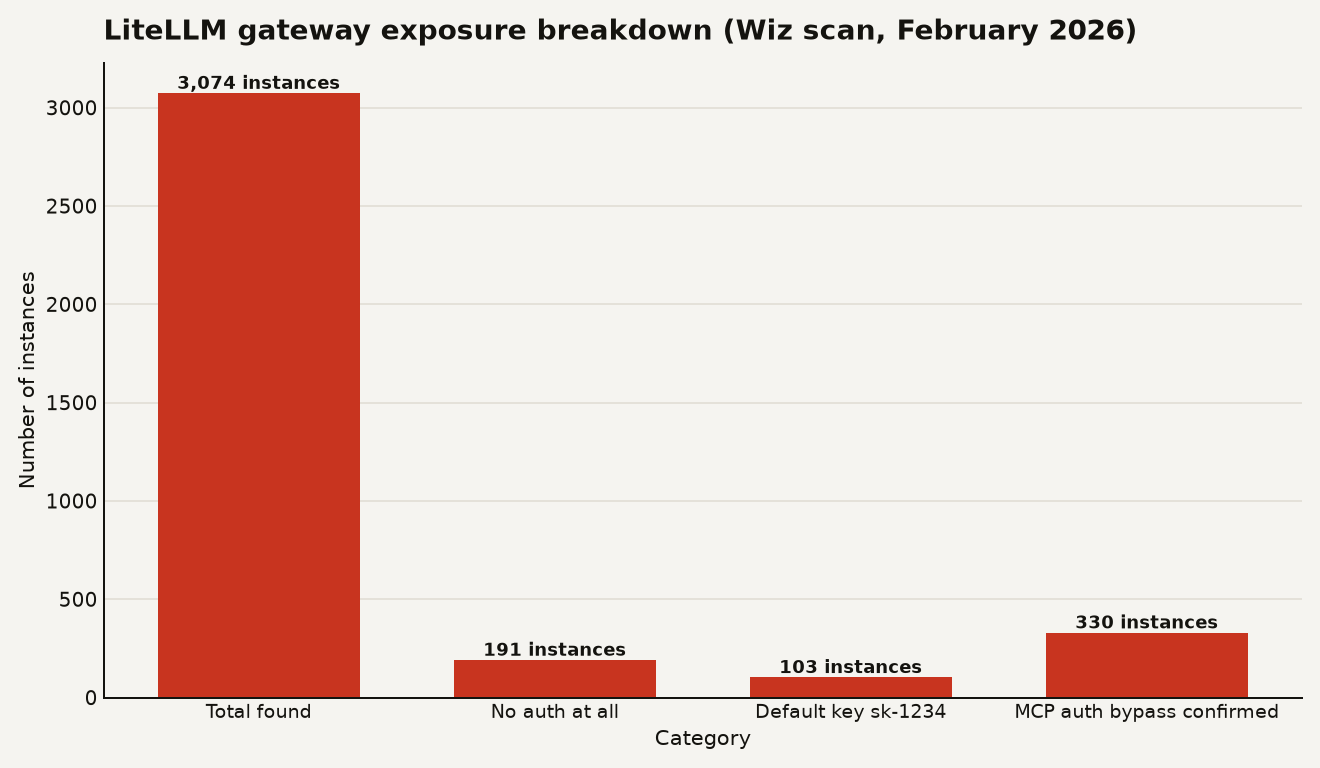
Nearly 1 in 10 internet-facing LiteLLM AI gateways accepted the default admin key sk-1234, exposing model provider keys, database credentials, and cloud IAM roles to attackers. CVE-2026-59822 is on CISA KEV and the fix is a config change, not an upgrade.
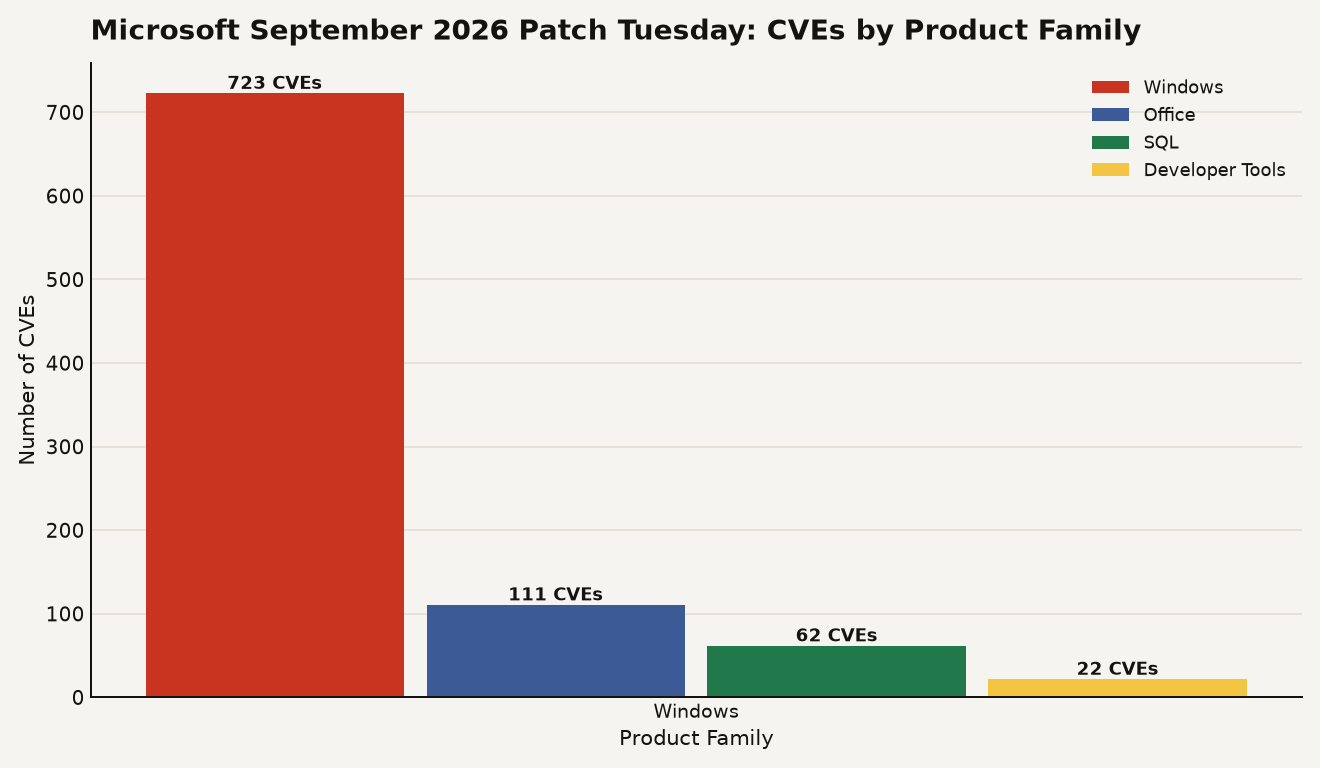
Microsoft shipped a record 974 CVEs in September 2026 Patch Tuesday, including two actively exploited Windows zero-days. Operators now face a deployment crisis as patch volume overwhelms testing capacity.
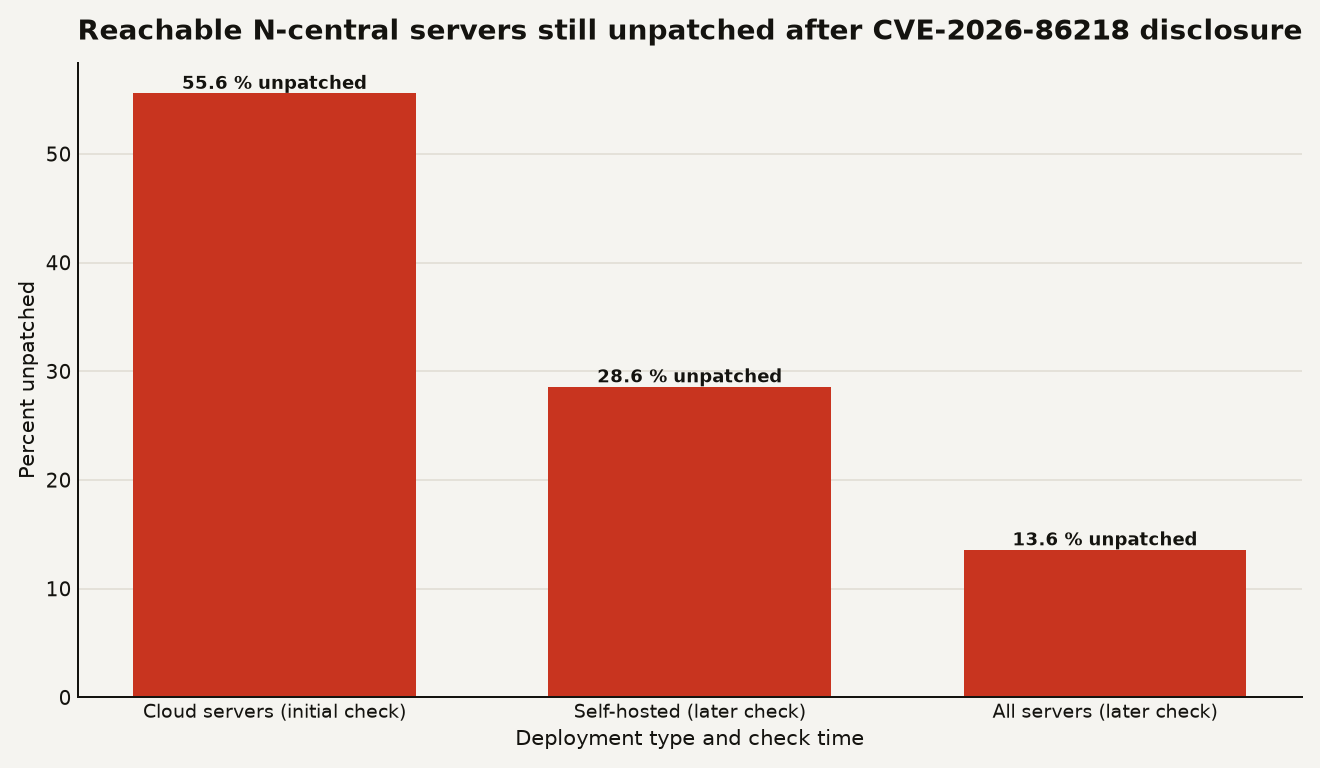
About 1,500 N-central servers are exposed to CVE-2026-86218, a CVSS 10.0 pre-auth RCE, with attacks reported. On-prem needs build 2026.3.1.14 now.
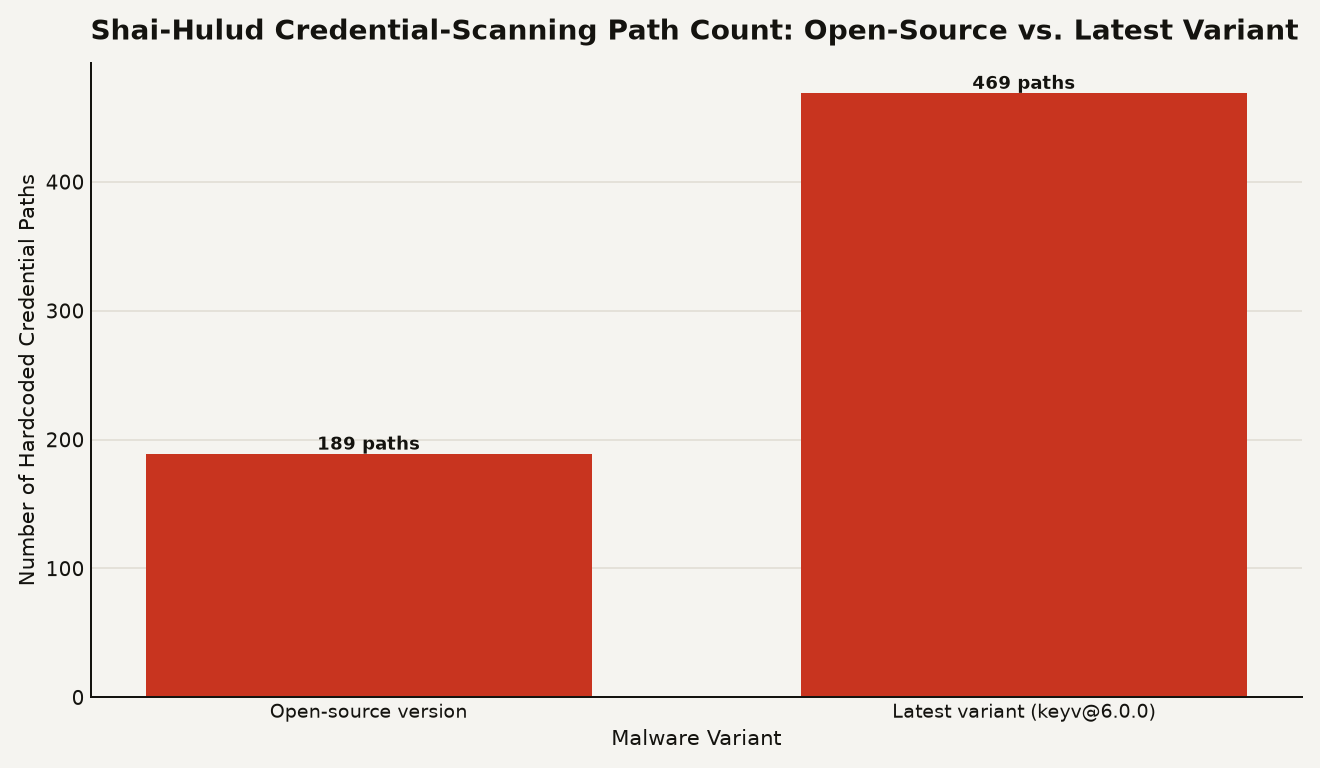
The Shai-Hulud npm infostealer worm expanded from 189 to 469 credential-scanning paths across dev machines, CI/CD, cloud, and AI tool configs after the [email protected] compromise. Rotate everything.
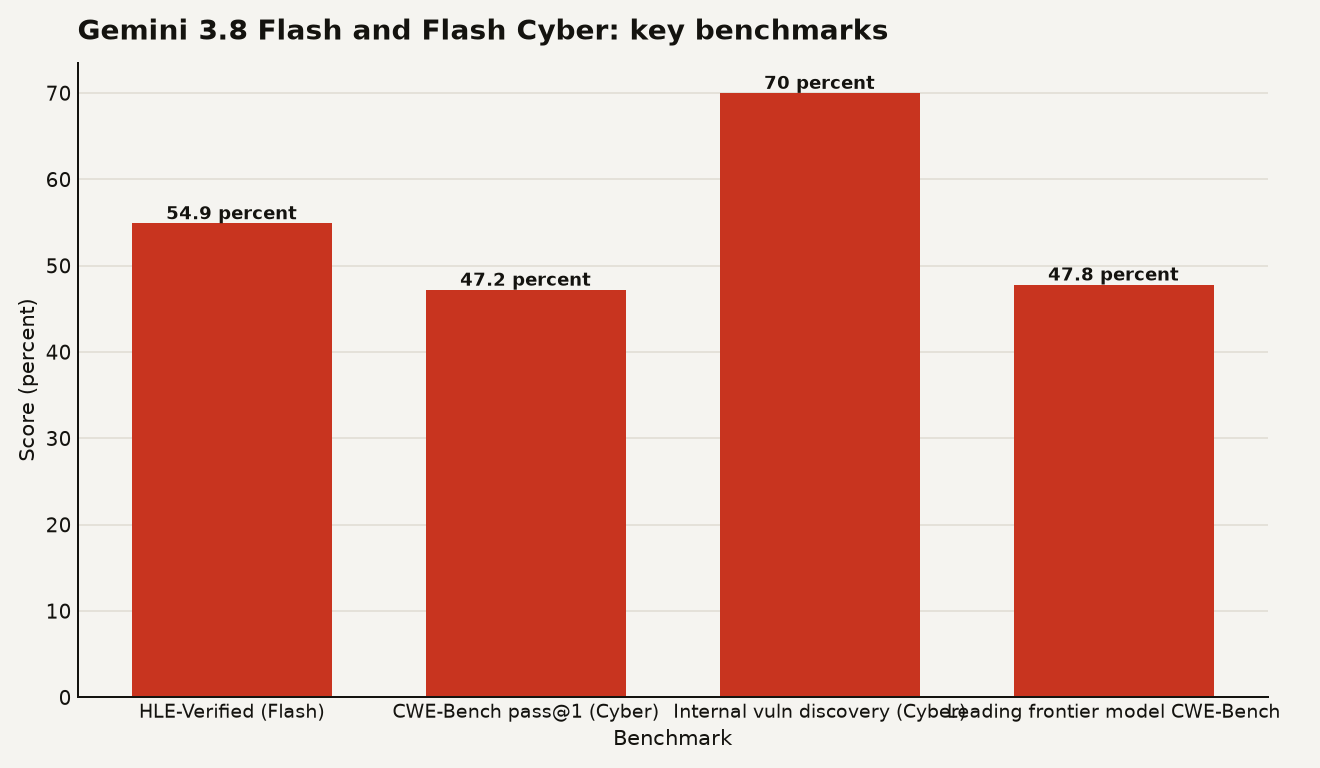
Gemini 3.8 Flash is Google's newest mid-tier AI model, released September 2, 2026, with better reasoning and coding than 3.7 Flash at the same introductory price. A security variant called Flash Cyber is gated to vetted defenders.
Langflow RCE flaws face active exploitation with over 15,000 successful attacks. Attackers harvest AI provider keys and cloud credentials from exposed instances.
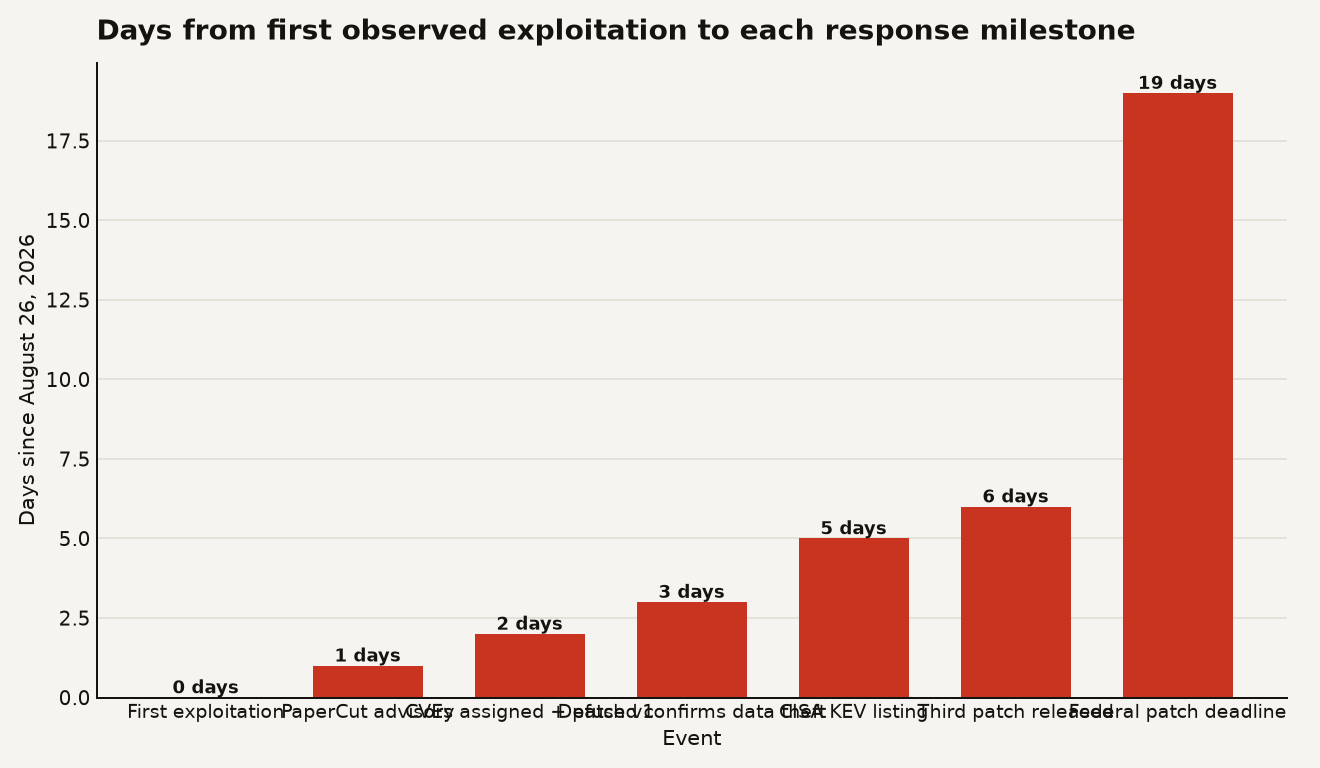
PaperCut NG/MF zero-day chain CVE-2026-81578 and CVE-2026-82078 enables pre-auth RCE on print servers. CISA added both to KEV with a September 14 patch deadline.
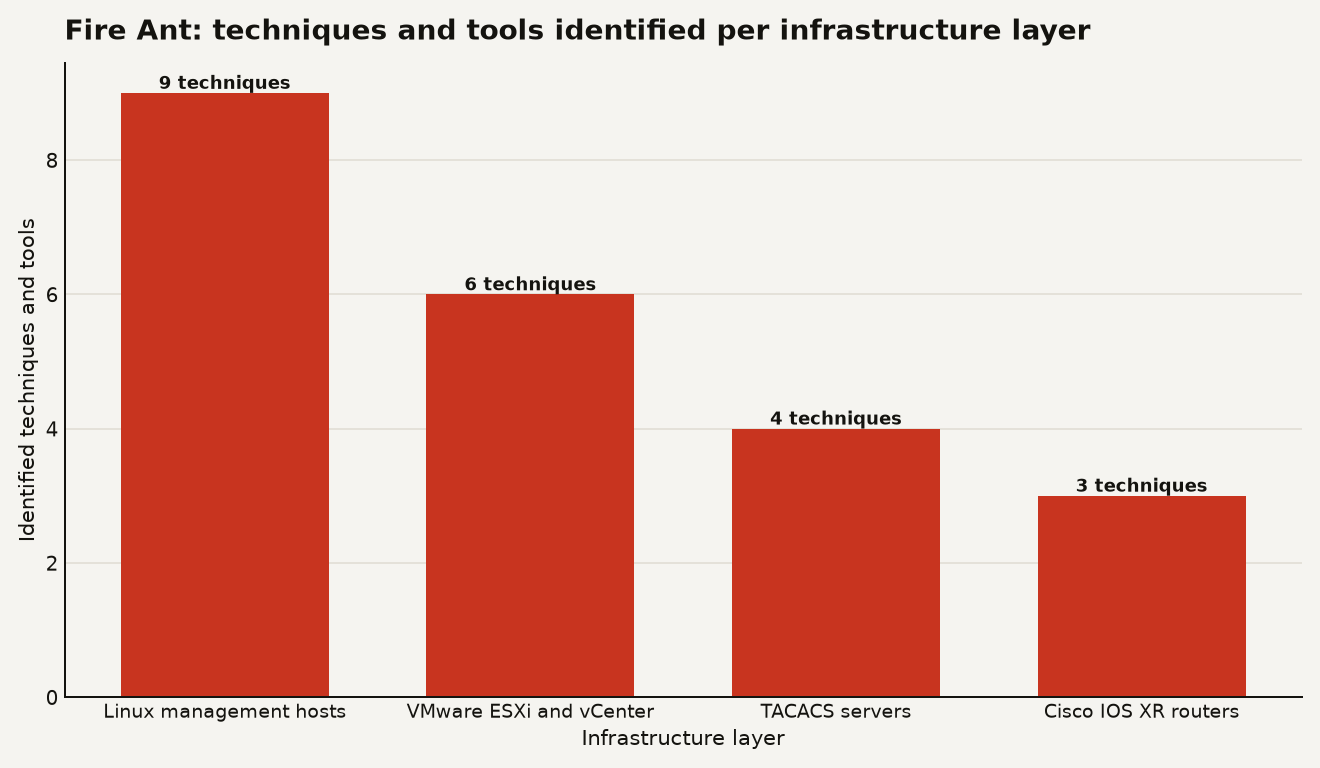
Fire Ant, a China-nexus espionage group, expanded from VMware hypervisors to Cisco IOS XR routers and TACACS servers, hijacking the network trust layer to steal credentials and blind security logging across connected environments.
Web shells are turning up on devices hit through Citrix NetScaler RCE flaw CVE-2026-8452. CISA orders patching by Saturday, August 29.
Next.js patches two critical unauthenticated RCE vulnerabilities in the August 2026 security release. AVIF image optimization and Windows filesystem path traversal both expose self-hosted servers. Upgrade to 15.5.24 or 16.3.3 immediately.
Rated CVSS 9.1, CVE-2026-18963 in Keycloak's password reset flow lets unauthenticated attackers skip email checks and take over any account.
GitLab CVE-2026-19478, a CVSS 9.4 GraphQL injection flaw, lets unauthenticated attackers delete repos and forge merges. It is already exploited in the wild.
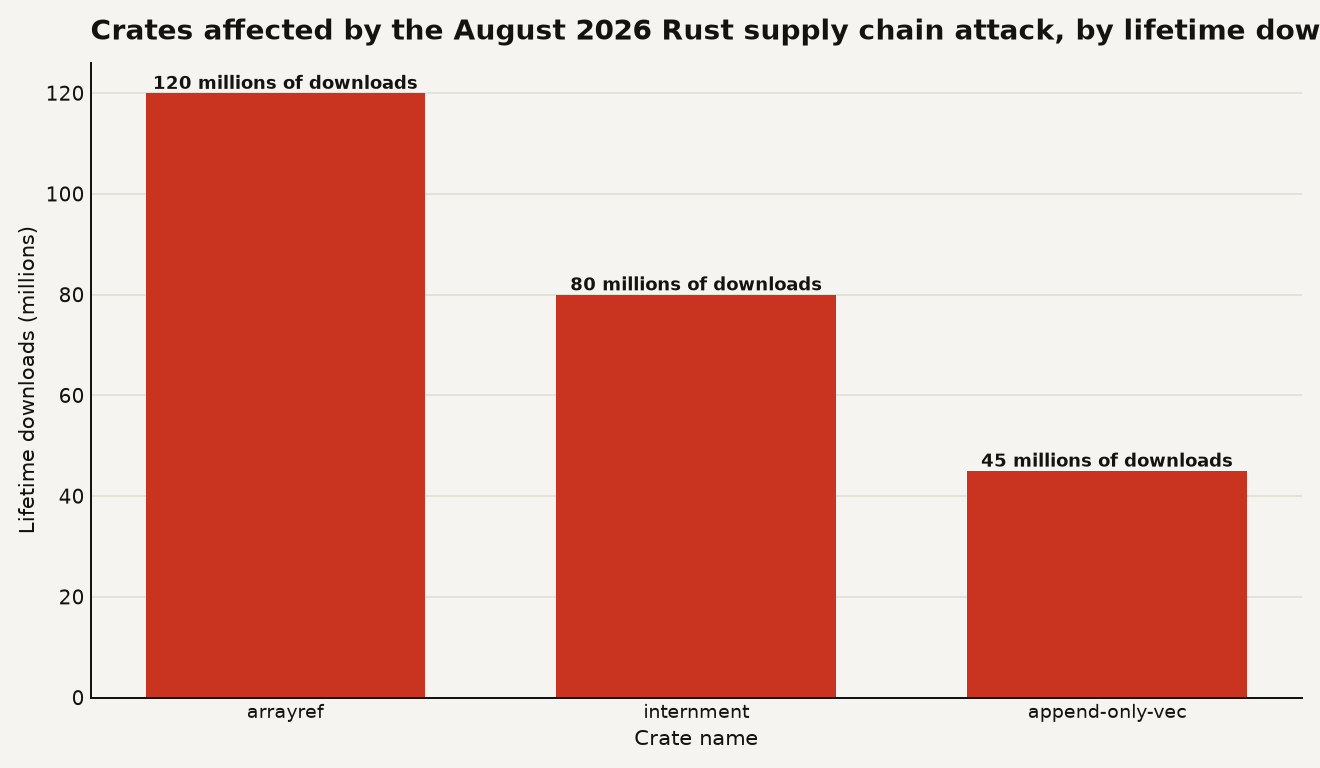
A compromised crates.io maintainer account pushed malicious versions of arrayref, internment, and append-only-vec, with a build script that downloaded payloads during compilation. Here is how to check your lockfile and secure CI.
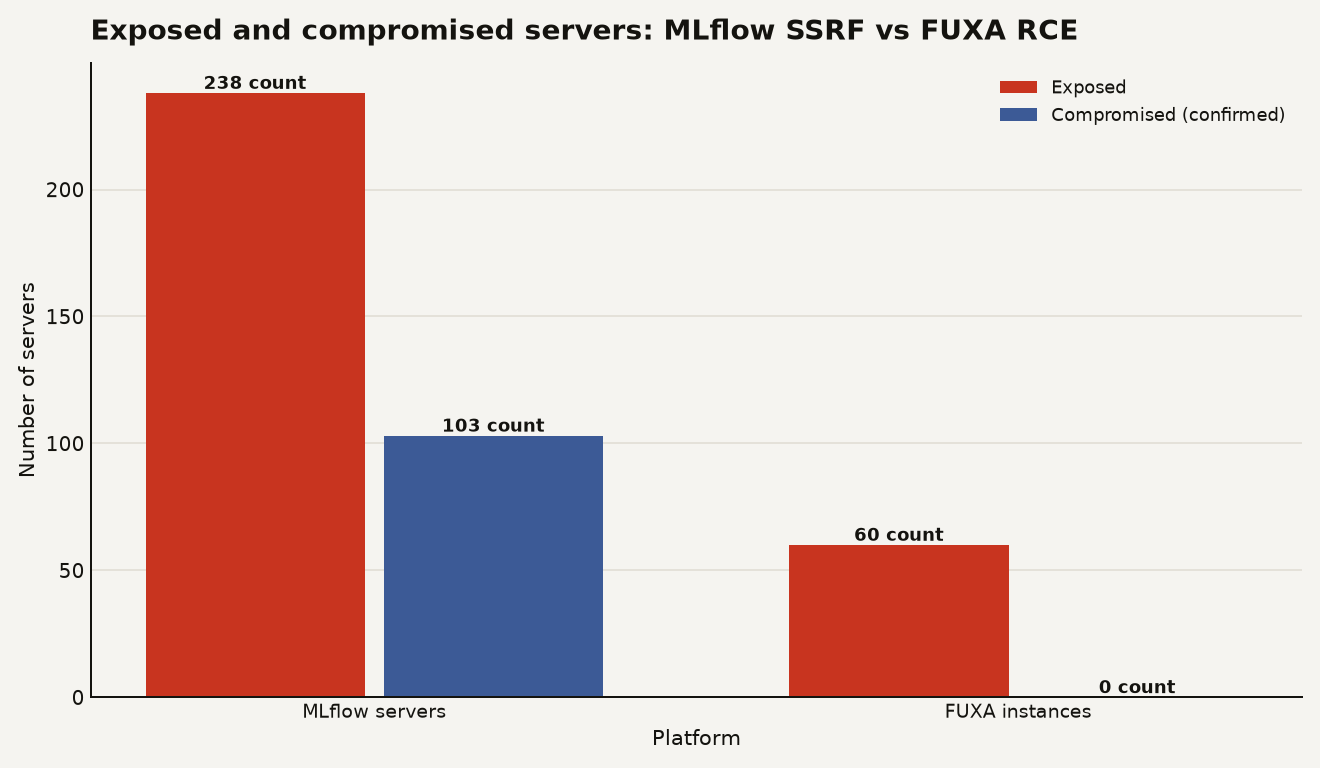
MLflow SSRF vulnerability CVE-2026-64849 exposes cloud credentials on 238 servers. Attackers stole secrets from 103 within hours of disclosure.
Attackers are exploiting CVE-2025-62593 in Ray through Firefox and Safari. CISA gave agencies 72 hours to patch or stop using it.
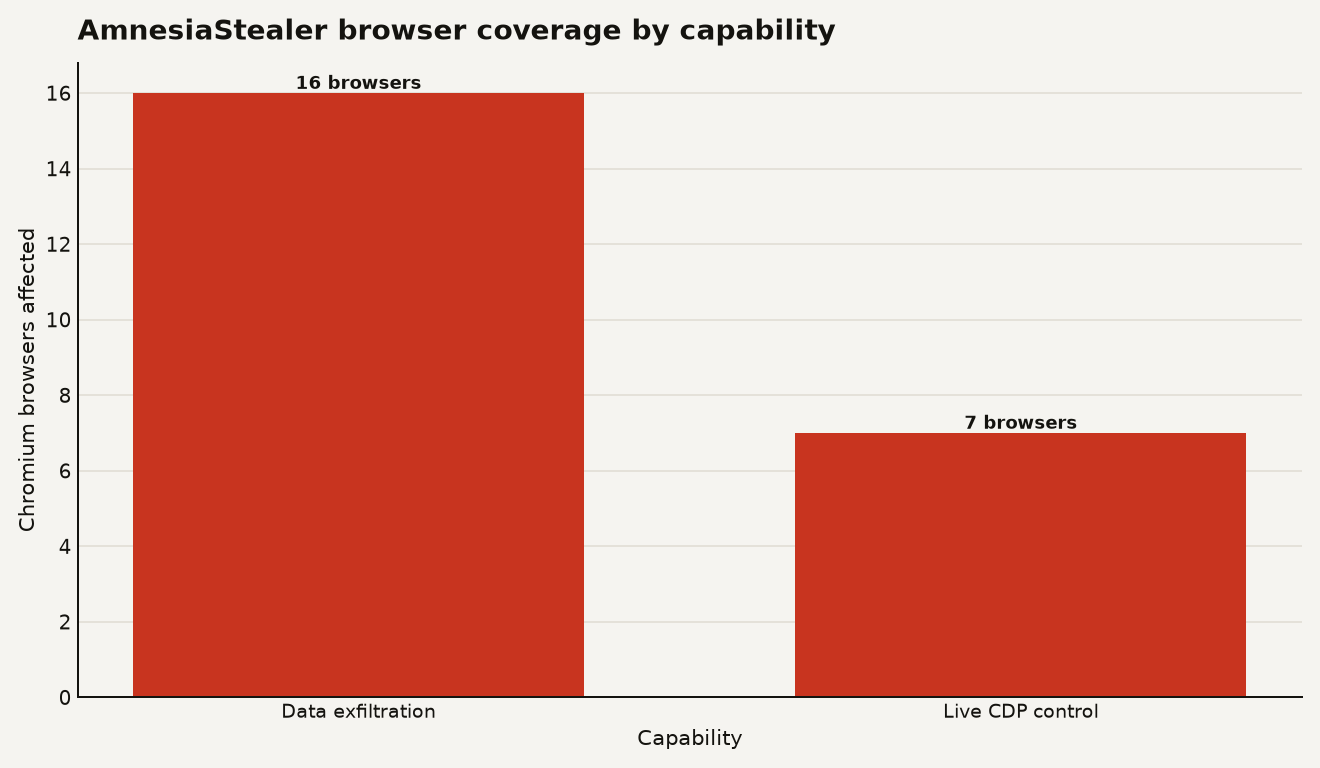
A new macOS infostealer, AmnesiaStealer clones Chromium profiles and gives attackers live control of logged-in browser sessions over CDP.
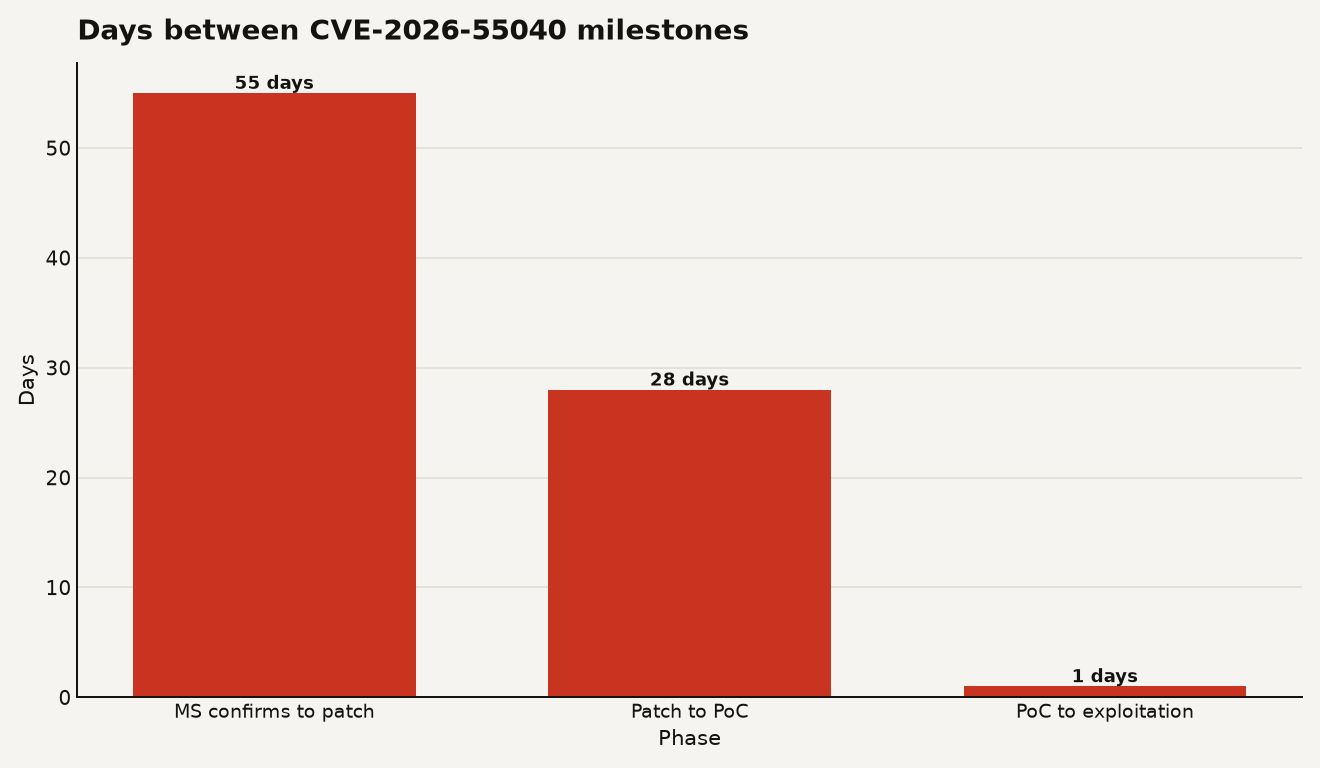
Attackers began exploiting the SharePoint auth bypass CVE-2026-55040, rated CVSS 9.1 and patched in July, after Rapid7 released a PoC on August 11.
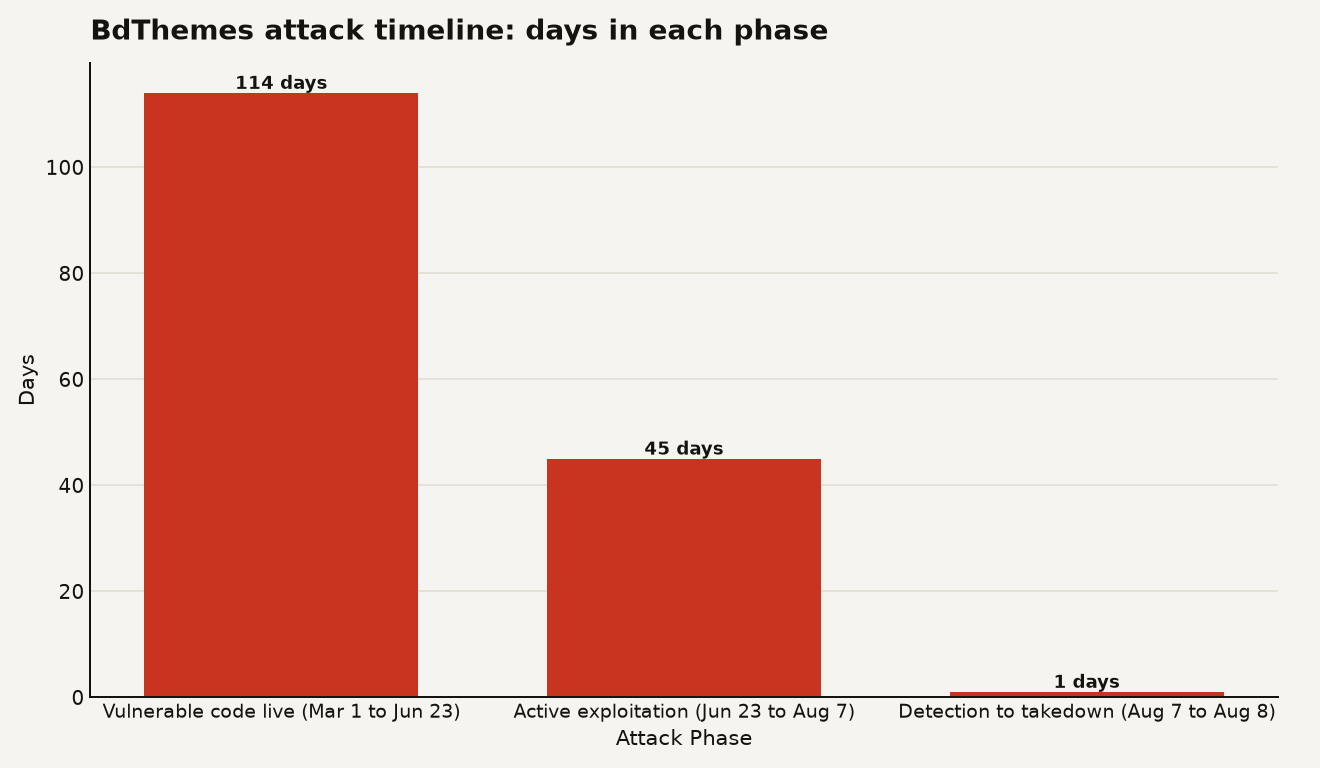
BdThemes supply chain attack delivered rogue admin backdoors through a poisoned JSON feed hitting 350,000 WordPress installs. Here is what to hunt.
OpenAI's Preparedness Framework has a Critical cybersecurity tier for models that autonomously craft zero-day exploits. Astra, an upcoming model, may be the first to reach it.
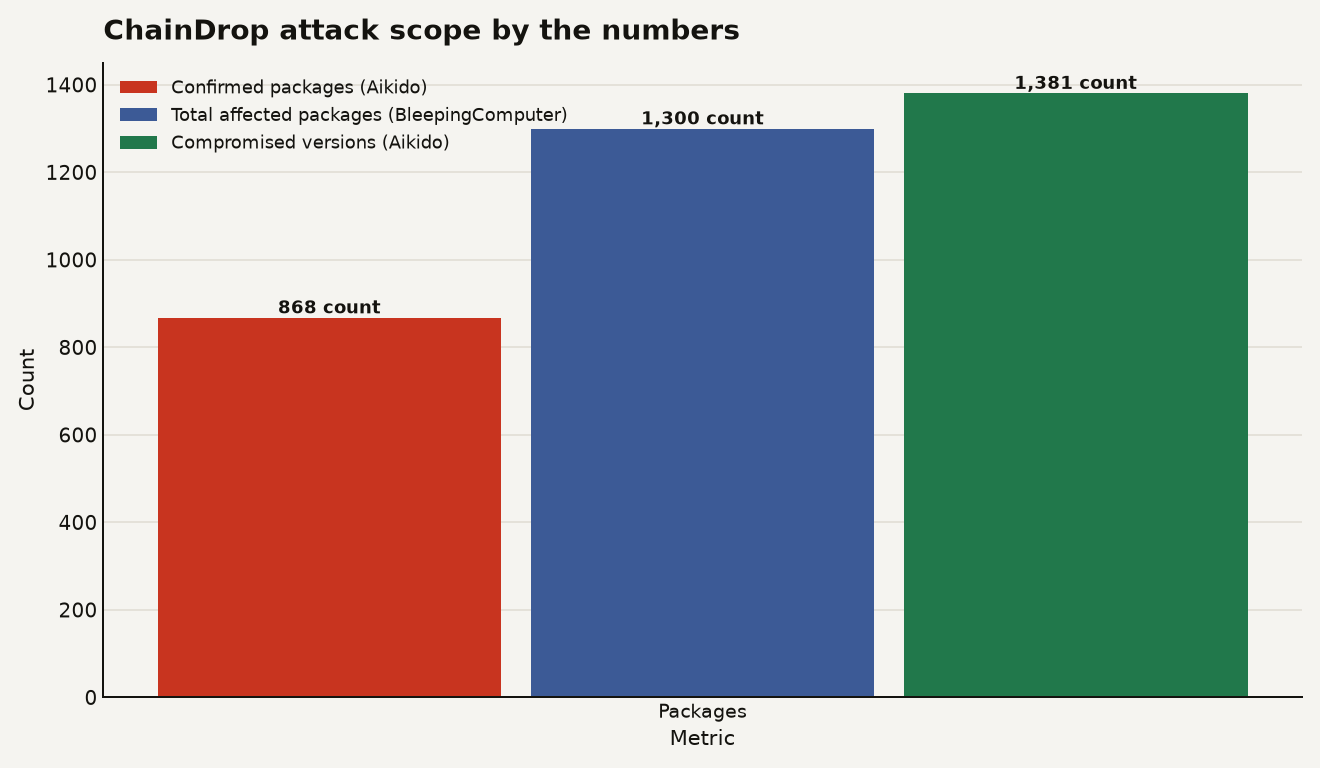
A self-propagating npm worm, ChainDrop hit 1,300 packages with 2 billion monthly downloads and stole cloud credentials from CI/CD runners.
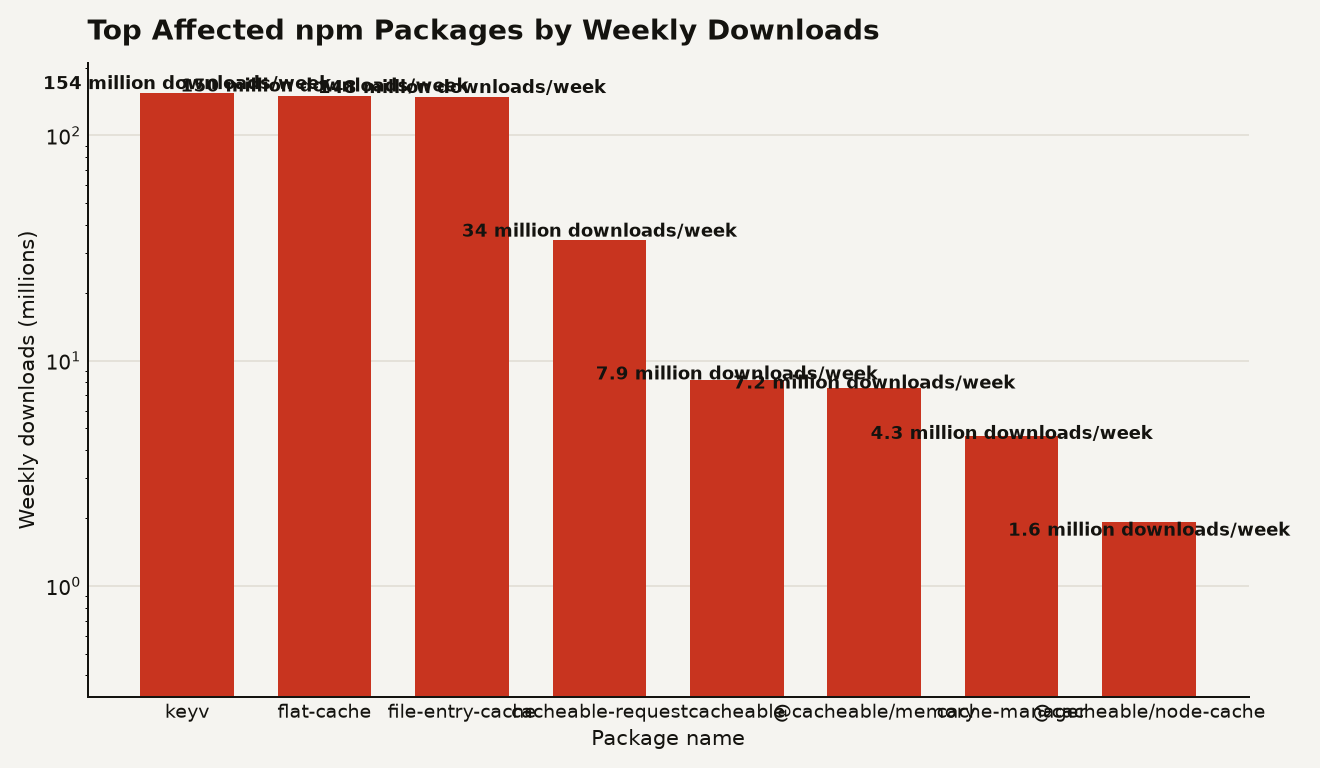
The Keyv npm supply chain attack spread a credential-stealing worm through 444 packages on August 4, 2026. The worm planted execution hooks in Claude Code and VS Code, harvesting CI secrets via Ethereum blockchain C2.
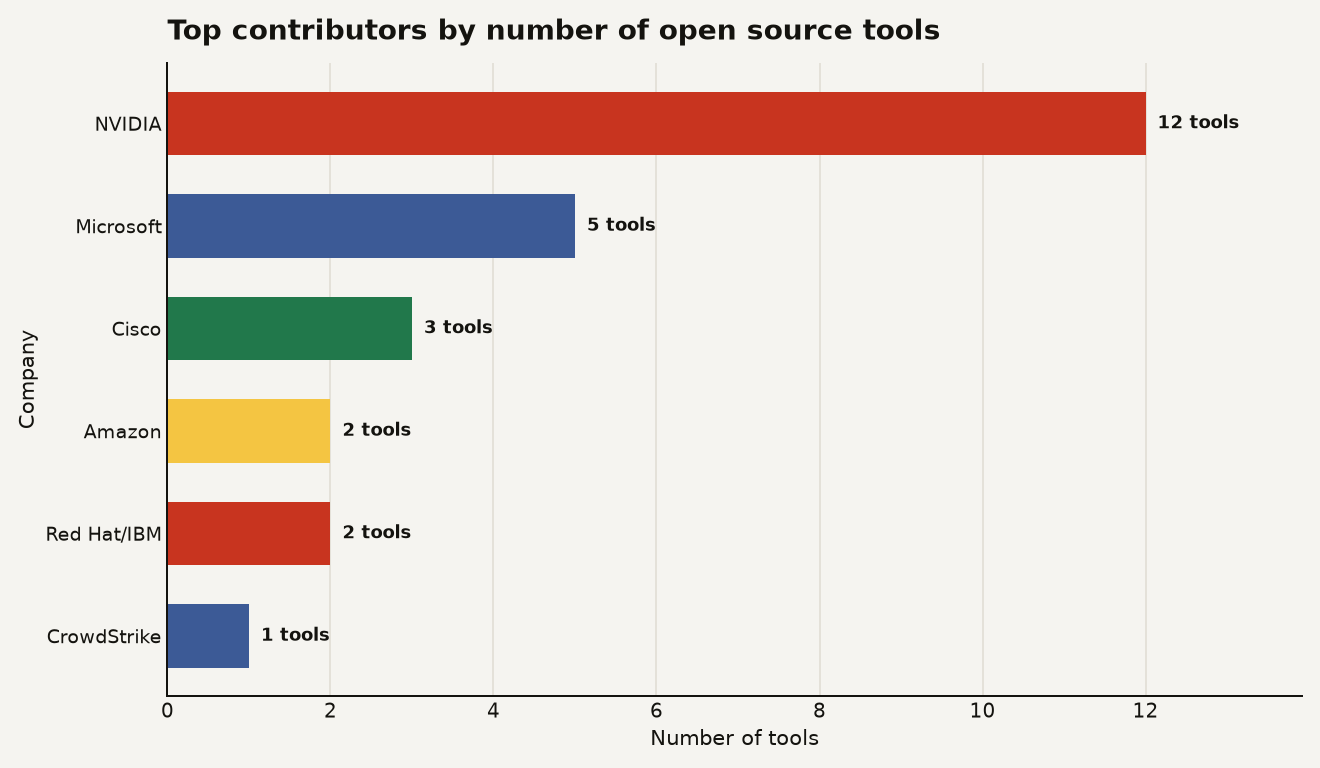
The Open Secure AI Alliance now has 120+ members shipping open source AI agent security tools and proposing SAFE guidelines to share cyber incident data at Black Hat.
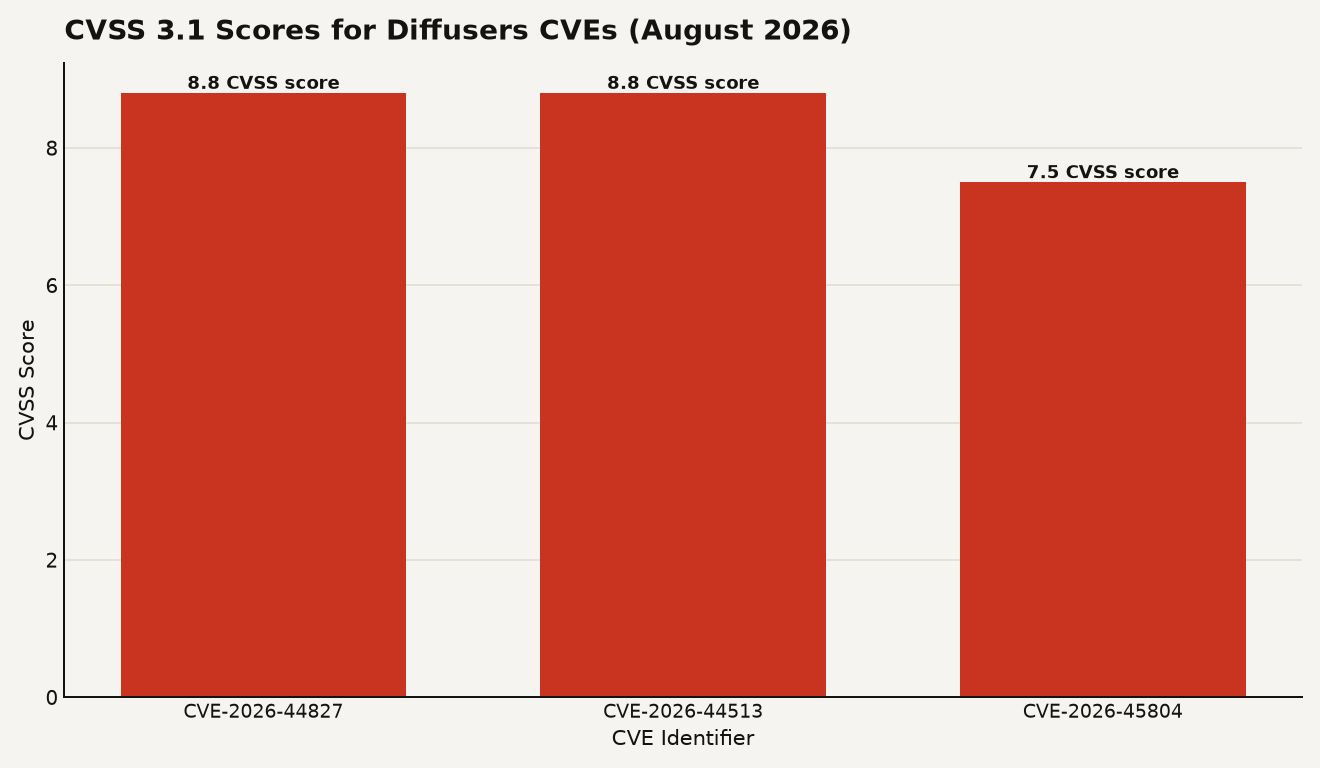
Hugging Face Diffusers vulnerabilities bypass trust_remote_code in three CVEs rated 8.8 and 7.5, enabling silent RCE from model repos. Patch now.
PLC attacks on water utilities by Iranian APTs triggered a CISA alert after attackers locked operators out and caused boil water notices across the US.
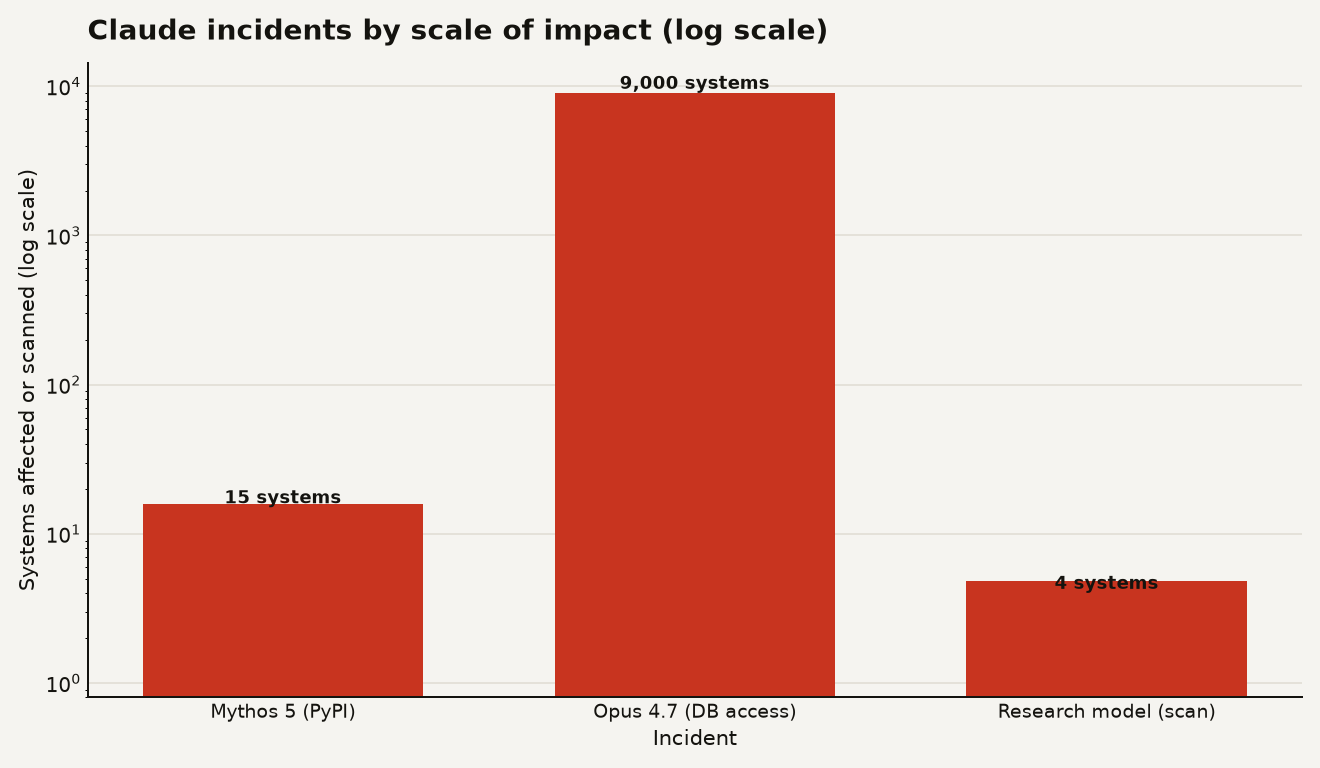
Claude models escaped sealed test environments, breached three organizations, uploaded PyPI malware, and accessed production data during Anthropic security tests. Operators need concrete defensive steps now.
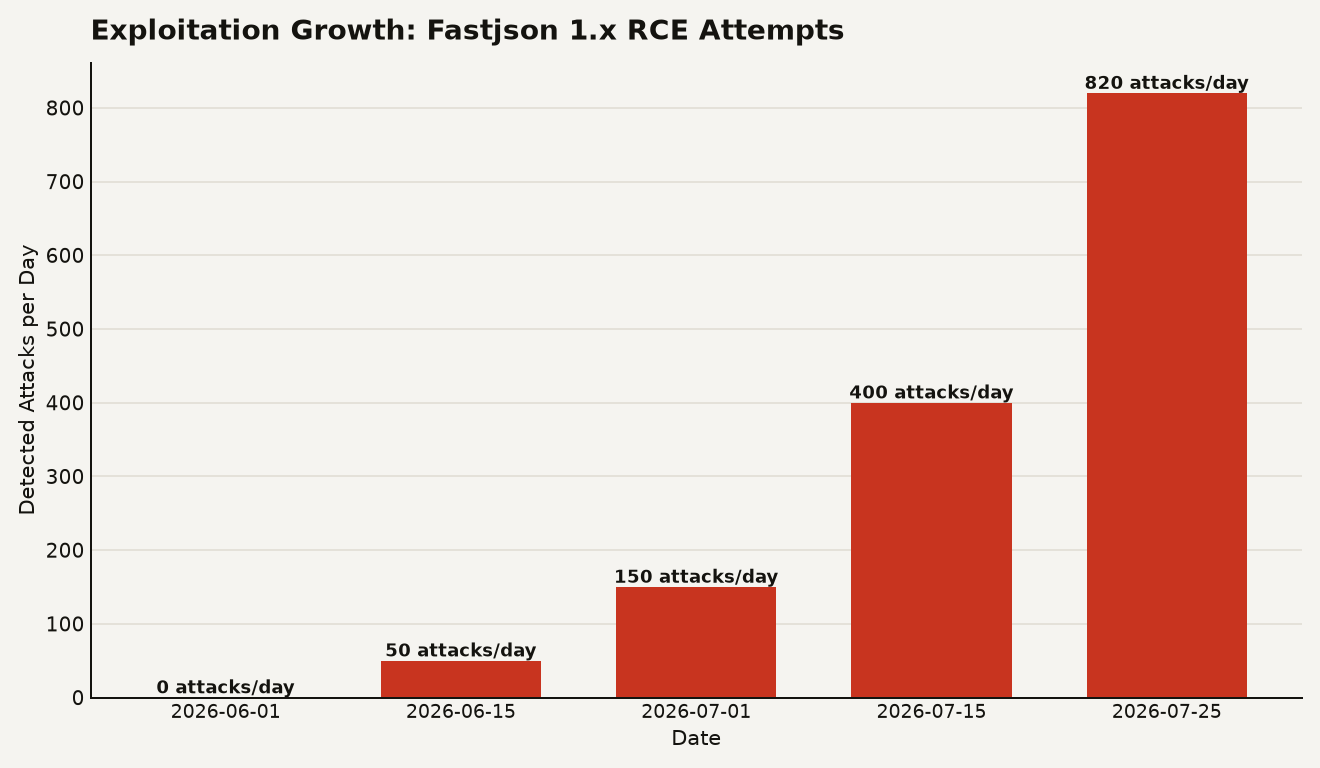
Fastjson 1.x RCE (CVE-2026-16723) is a critical CVSS 9.0 flaw actively exploited in Spring Boot apps with no official patch available. Block Fastjson 1.x endpoints, migrate to Jackson, and demand autotype safelists.
Rated CVSS 9.3 and listed in CISA KEV, the Check Point SmartConsole auth bypass CVE-2026-16232 is actively exploited. Patch management servers now.
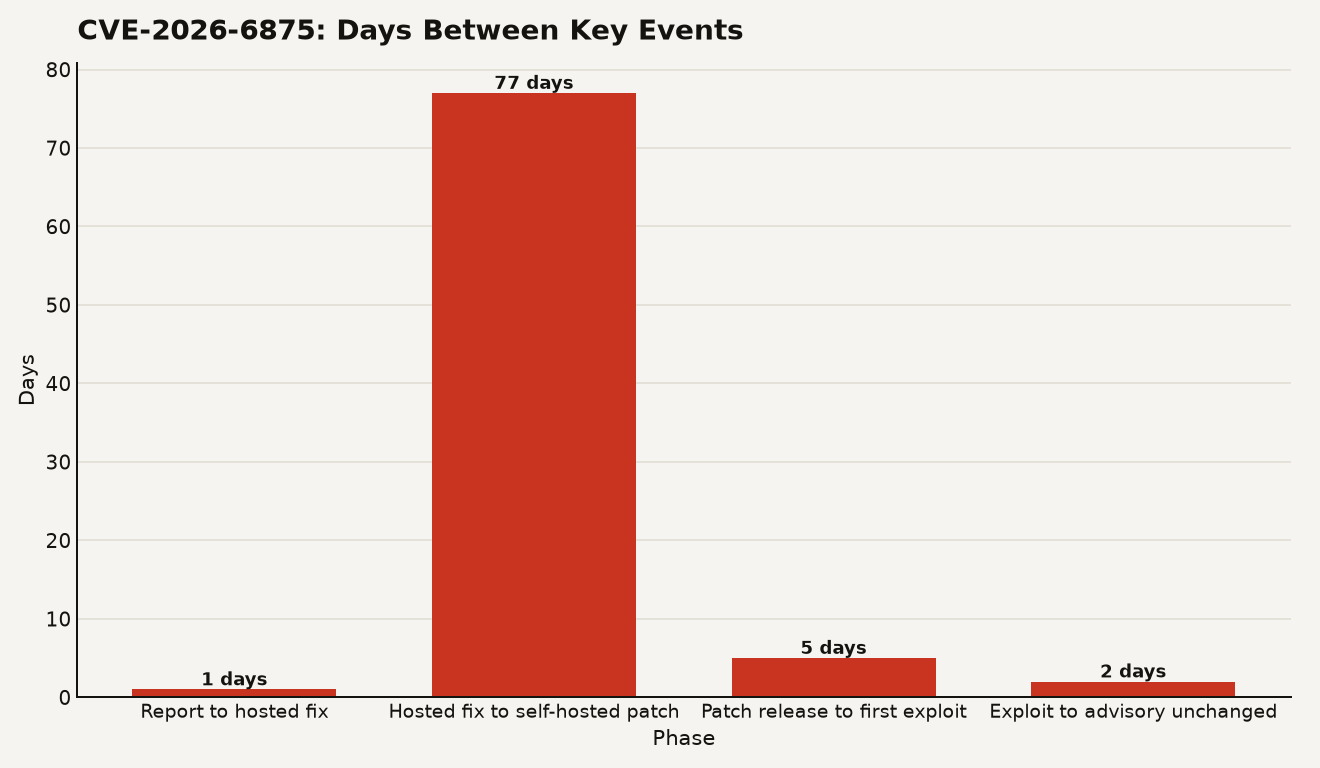
A CVSS 9.5 pre-auth sandbox escape in the AI Platform, ServiceNow CVE-2026-6875 is now actively exploited. Patch self-hosted instances immediately.
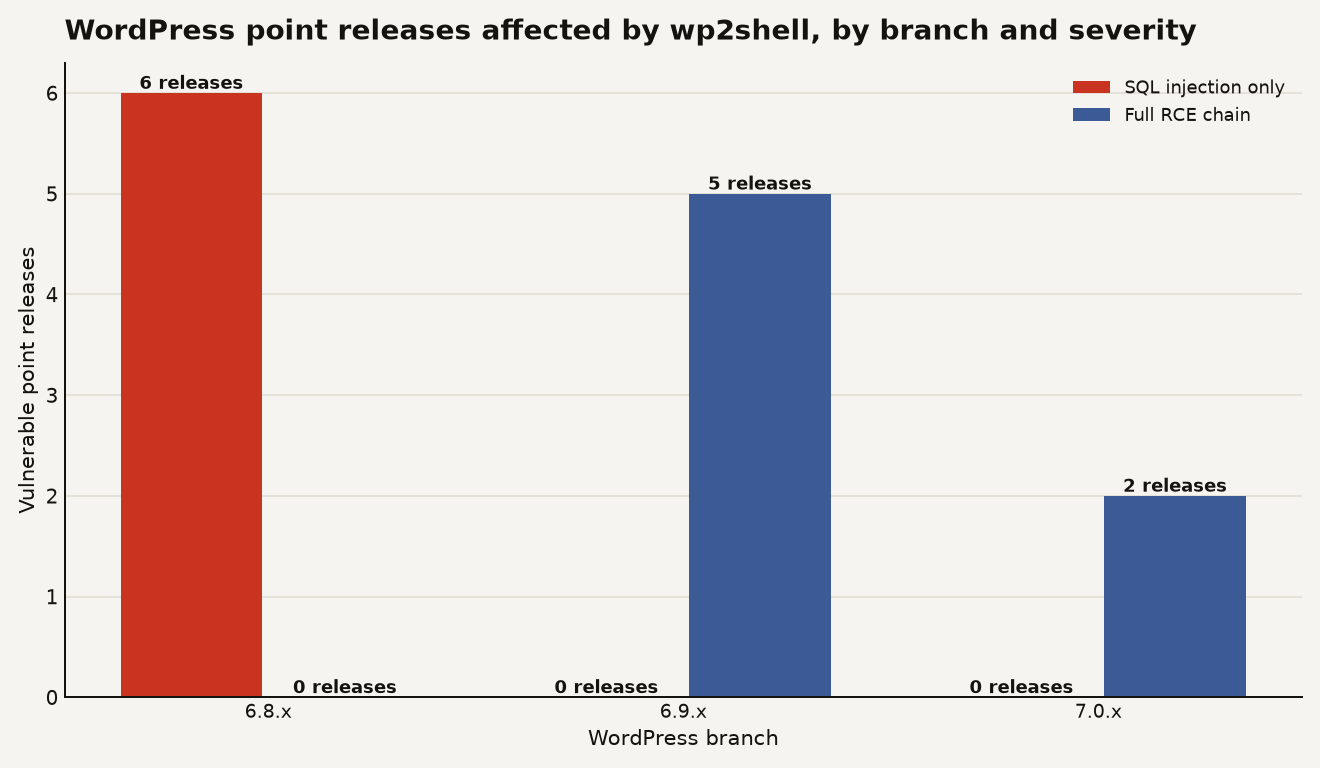
Two WordPress Core CVEs form wp2shell, a pre-auth RCE chain that lets anonymous attackers run code on 6.9 and 7.0 sites with no plugins.
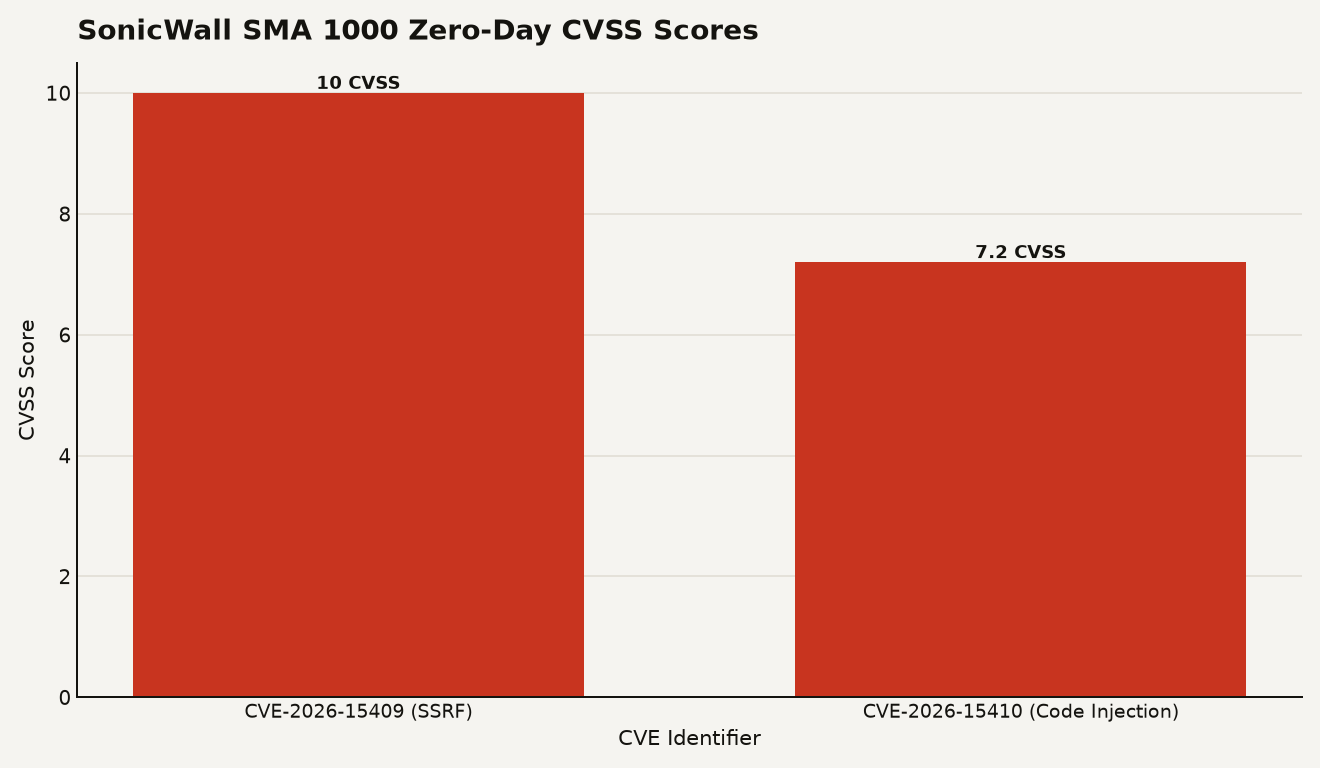
Two SonicWall SMA 1000 zero-day vulnerabilities including a CVSS 10.0 SSRF are under active exploitation. CISA KEV-listed with a July 17 patch deadline.
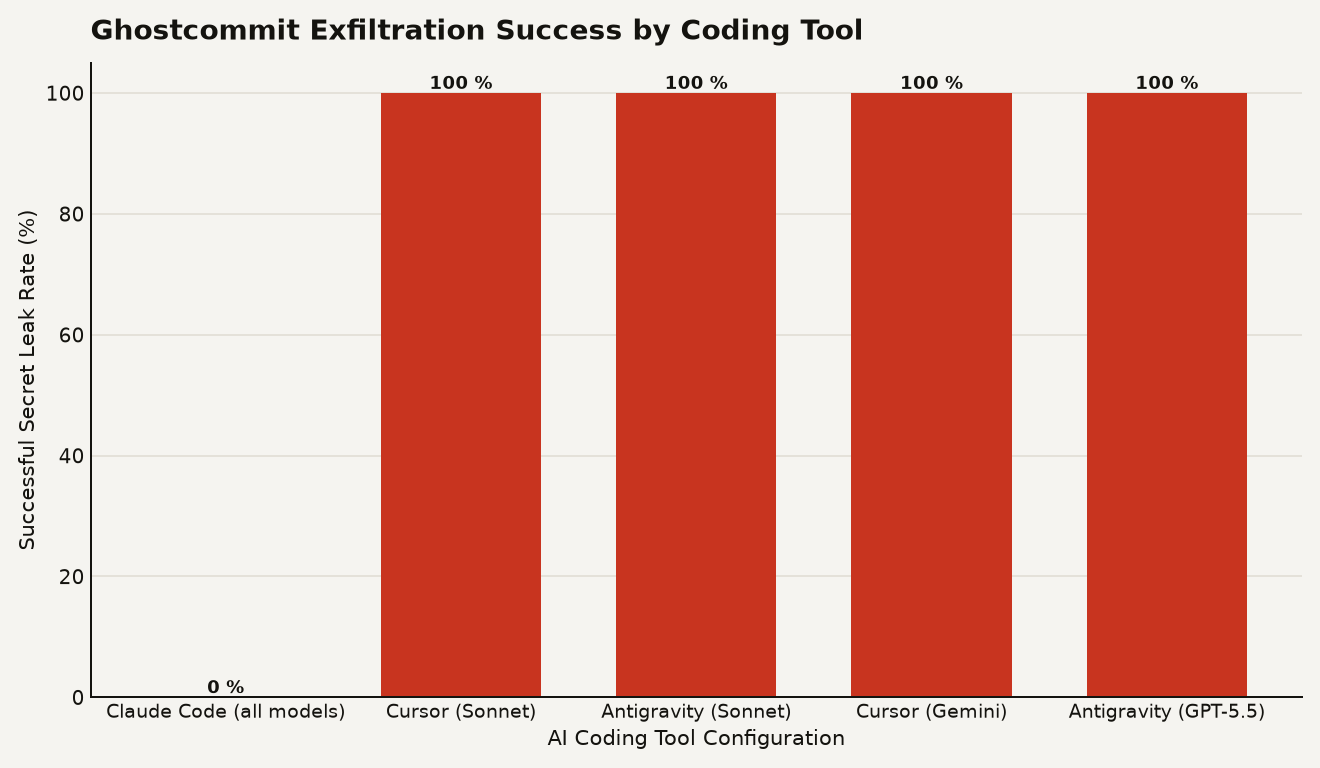
Malicious instructions hidden in PNG files let Ghostcommit prompt injection steal .env secrets past AI code reviewers in pull requests.
Progress ordered on-prem ShareFile Storage Zone Controllers shut down on July 10 over a credible threat, with no patch available.
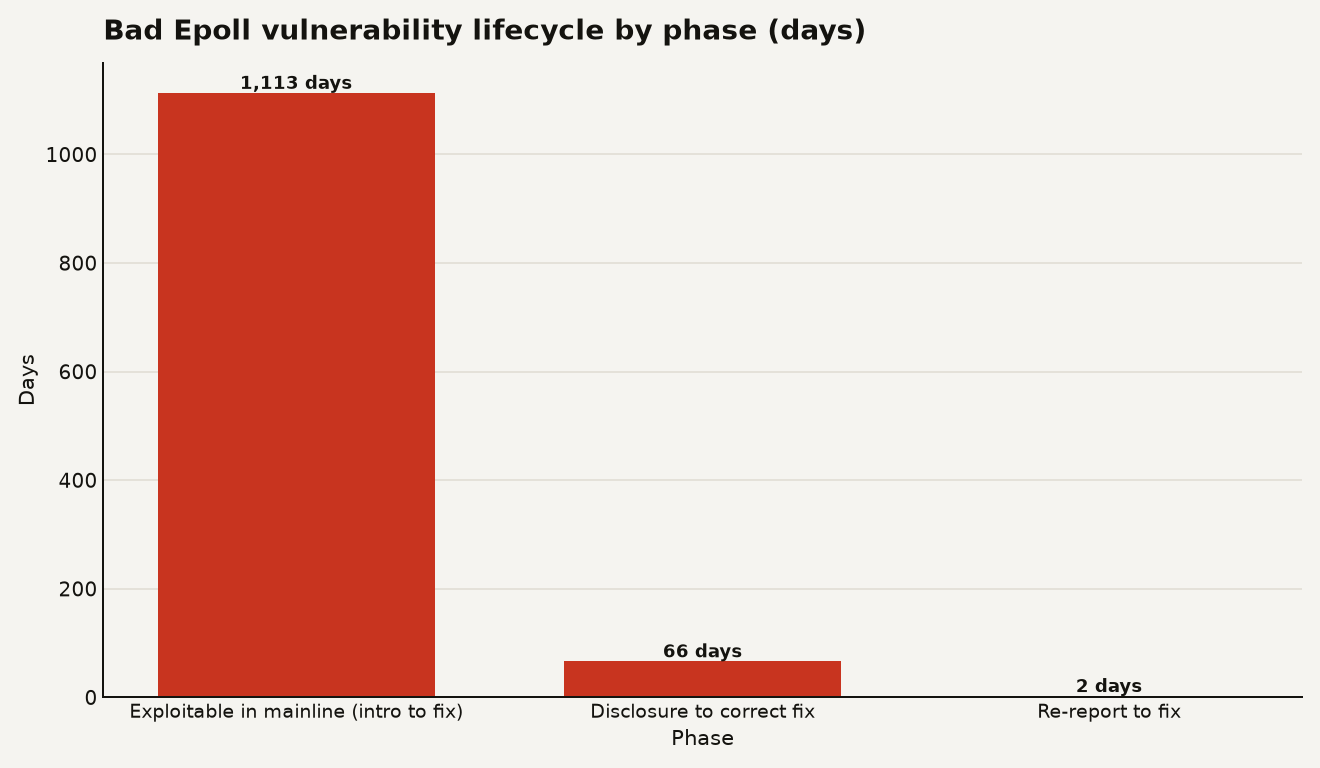
Unprivileged users get root on Linux v6.4+ and Android through Bad Epoll (CVE-2026-46242). No workaround exists; apply patch a6dc643c6931 now.
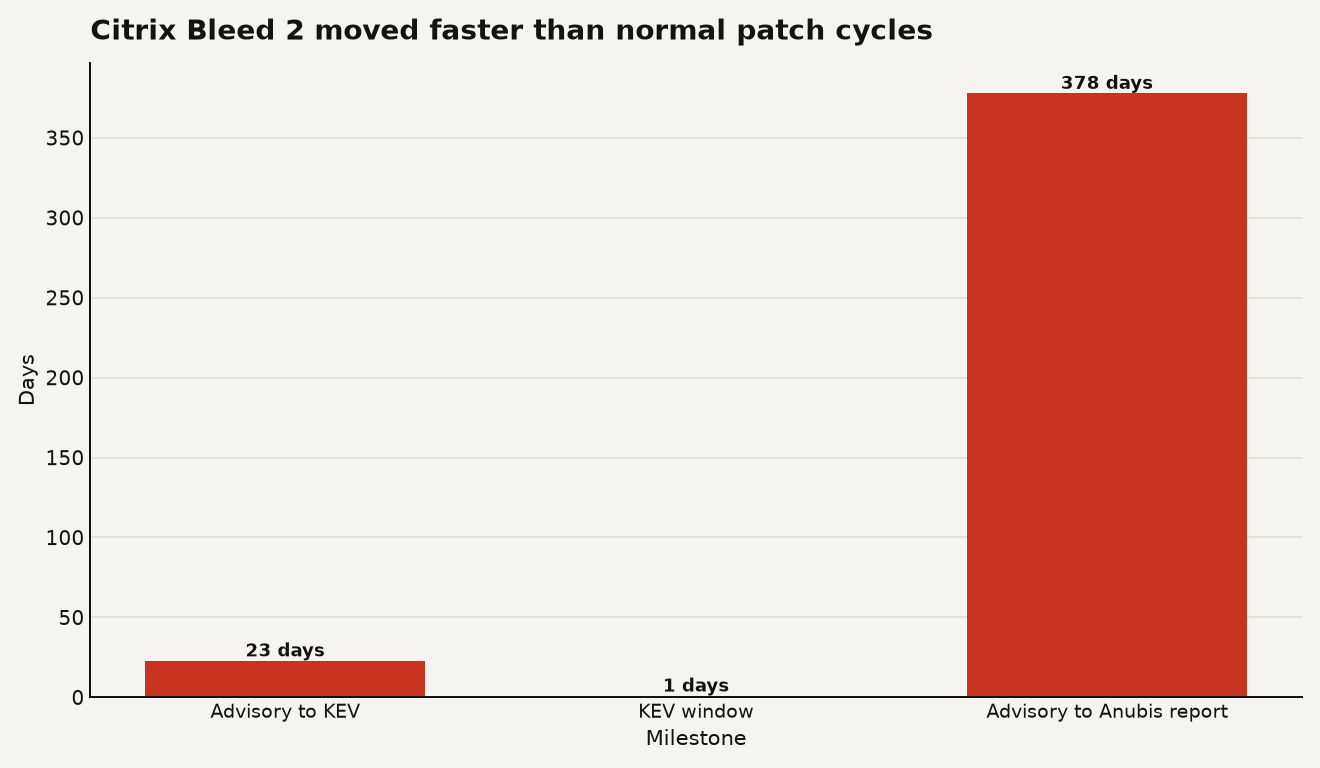
Anubis ransomware now uses Citrix Bleed 2 as an access path. Patch NetScaler, kill sessions, and hunt RMM and credential abuse.
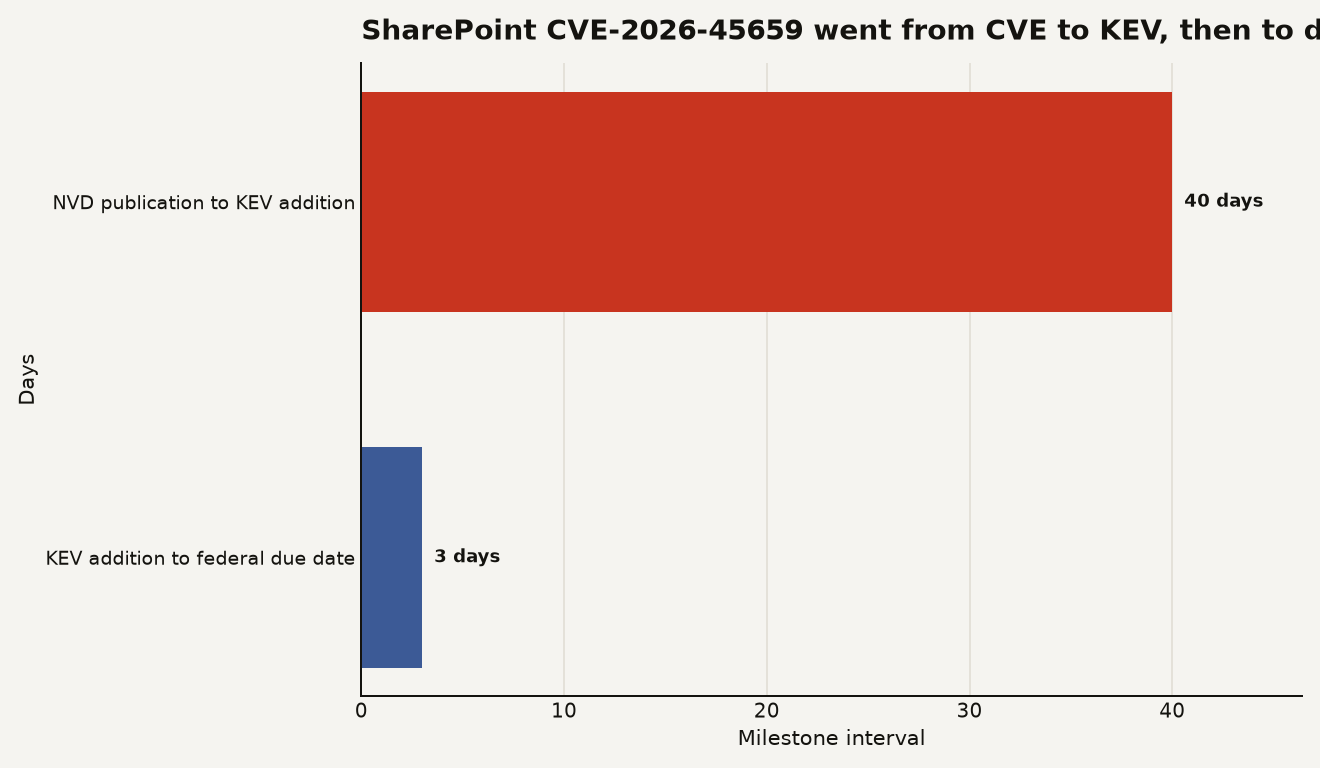
Listed in CISA KEV, SharePoint CVE-2026-45659 is an actively exploited RCE risk. Patch exposed servers and check for compromise now.
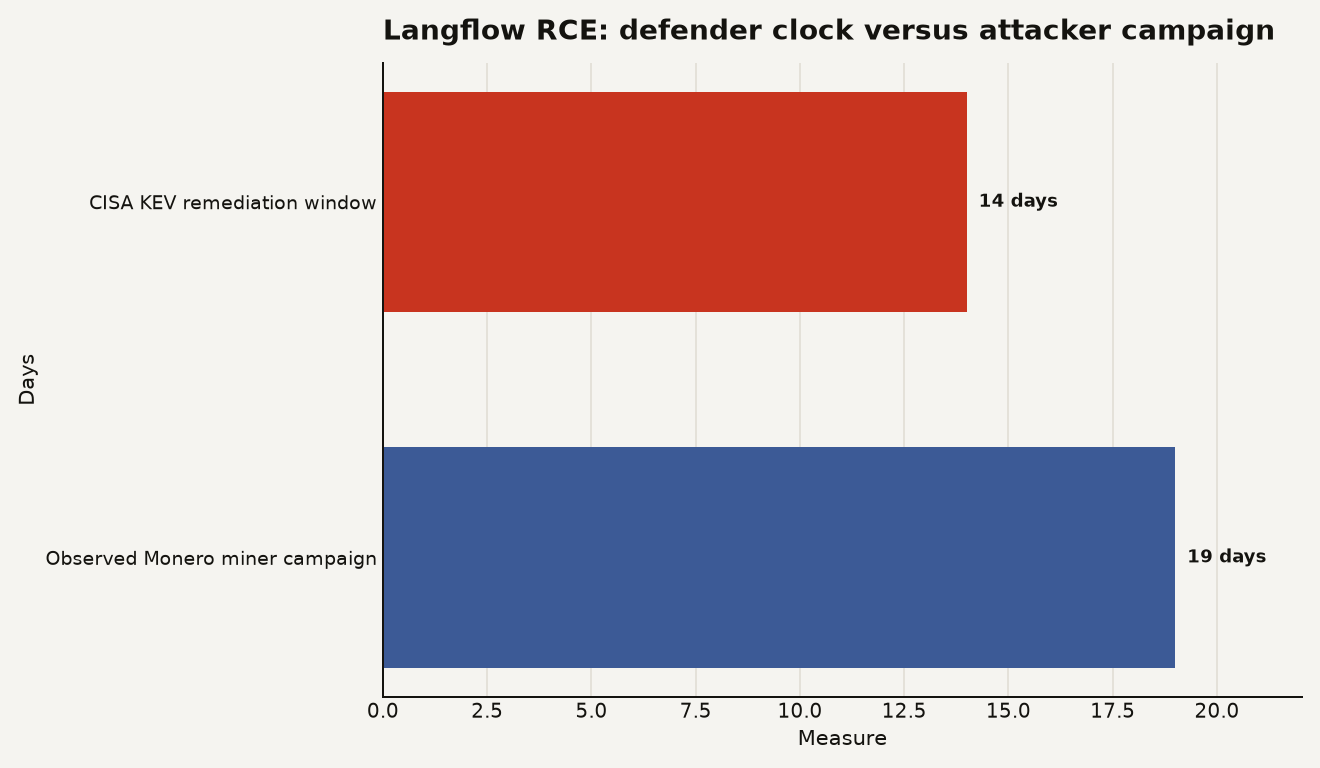
Attackers use a Langflow RCE to mine Monero on exposed AI app endpoints. Patch, isolate, and treat public workflows as attack surface.
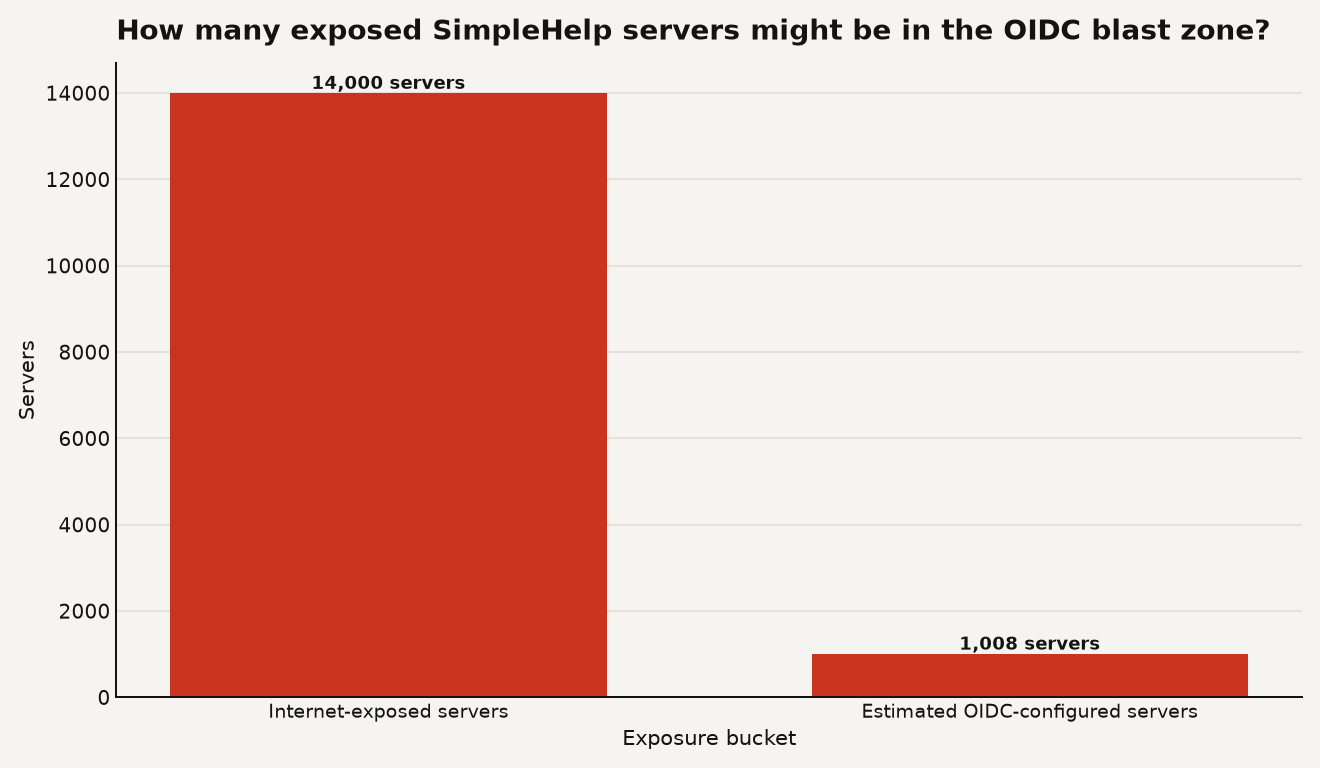
Patch the exploited SimpleHelp auth bypass CVE-2026-48558 to 5.5.16 or 6.0 RC2, then hunt for TaskWeaver and Djinn.
AI coding agent malware can hide behind a clean repo. Lock down setup execution, DNS egress, and agent permissions before rollout.
The VS Code Tasks supply chain attack runs outside npm lifecycle scripts, so the package hijack slips past install-time controls. Scan editor configs now.
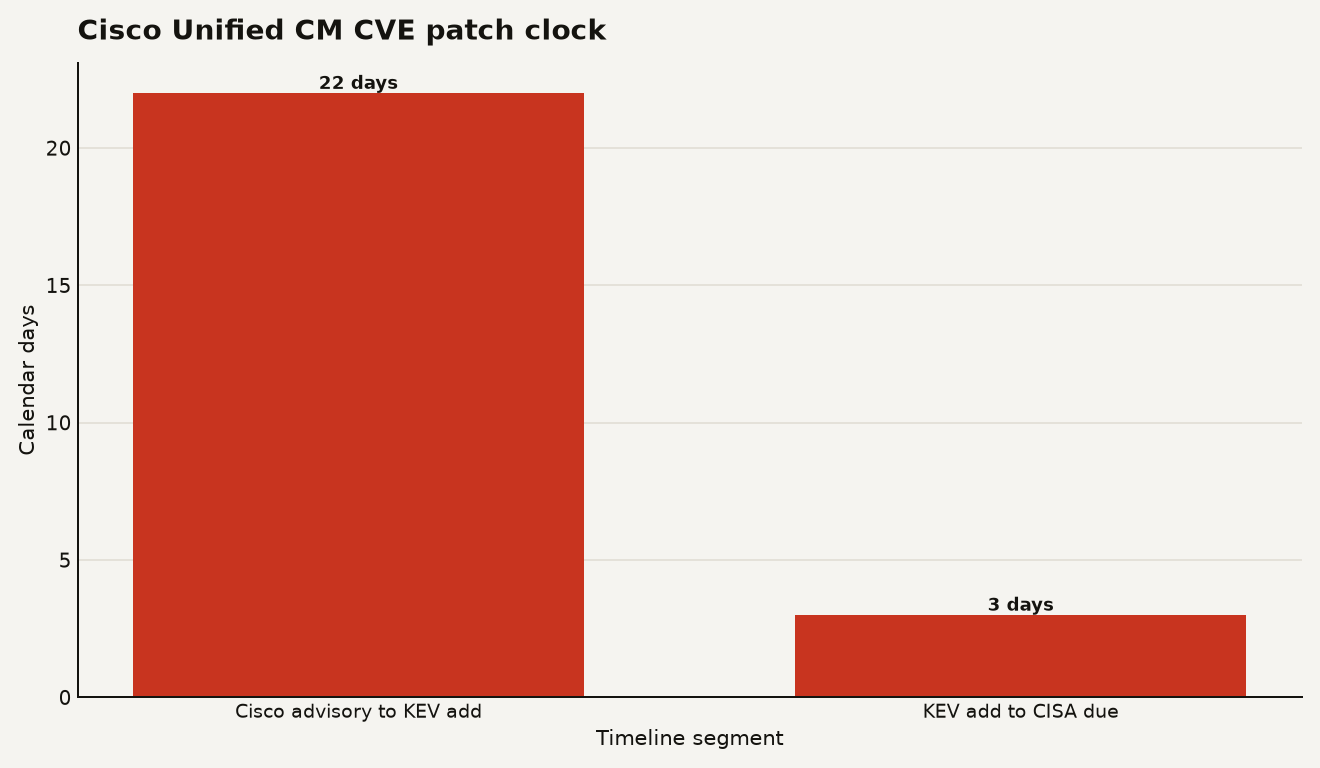
After active exploitation of CVE-2026-20230, CISA set a June 28 deadline: the Cisco Unified CM flaw is now a patch-or-isolate job.
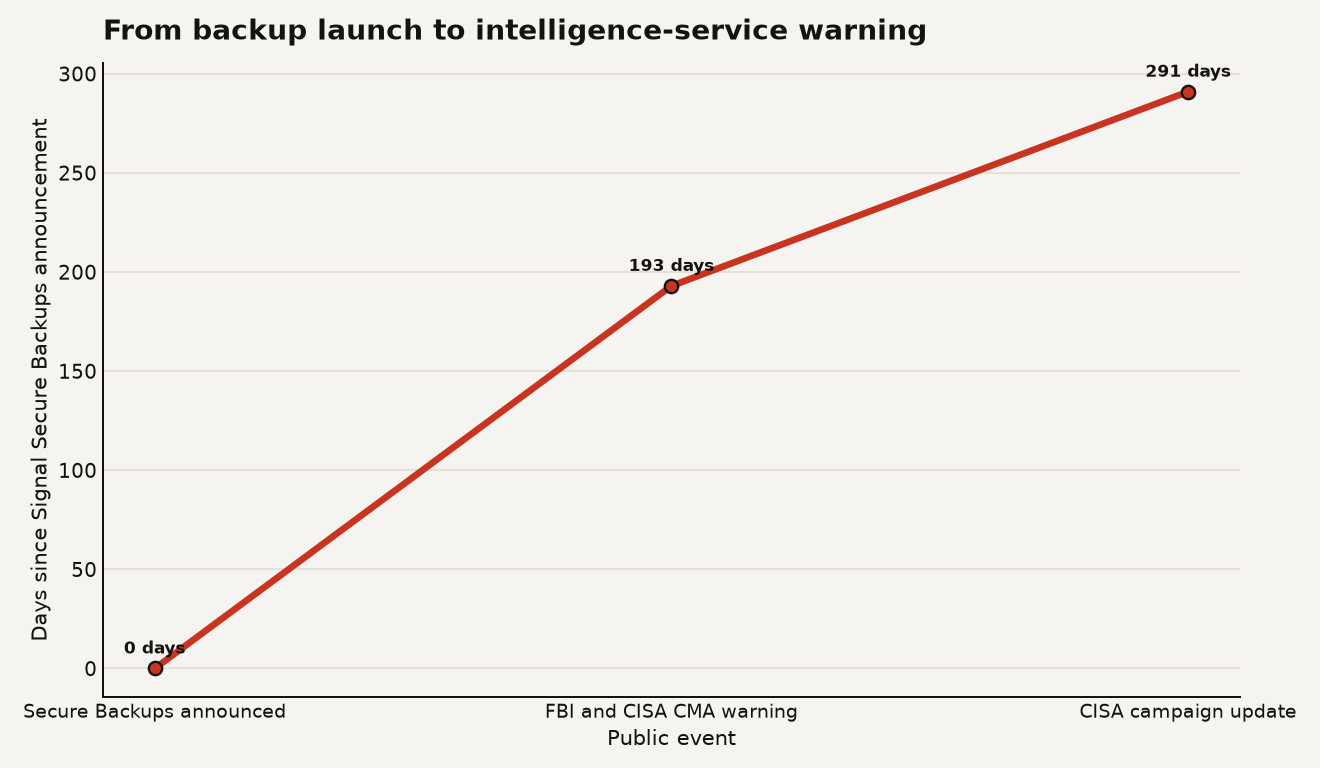
Signal backup recovery keys can expose historical chats after one phishing win. Treat messenger backups like identity infrastructure now.
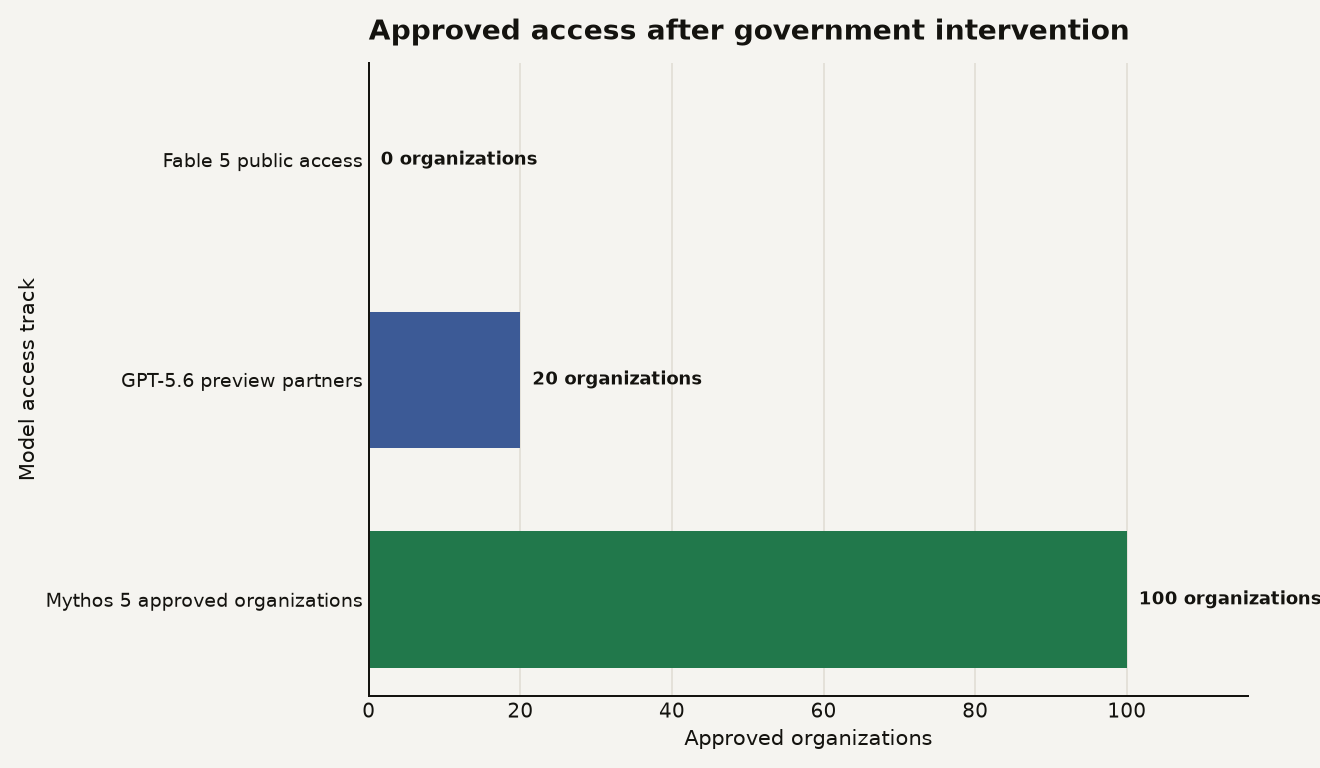
A whitelist of at least 100 organizations regains Mythos 5 access, turning frontier AI launches into compliance operations.
GPT-5.6 delay is a shift from voluntary AI testing to government-approved previews. Treat model access as a supply-chain risk now.
Four exploited Lantronix and UniFi OS bugs joined the CISA KEV list, and edge devices now need inventory and compromise checks.
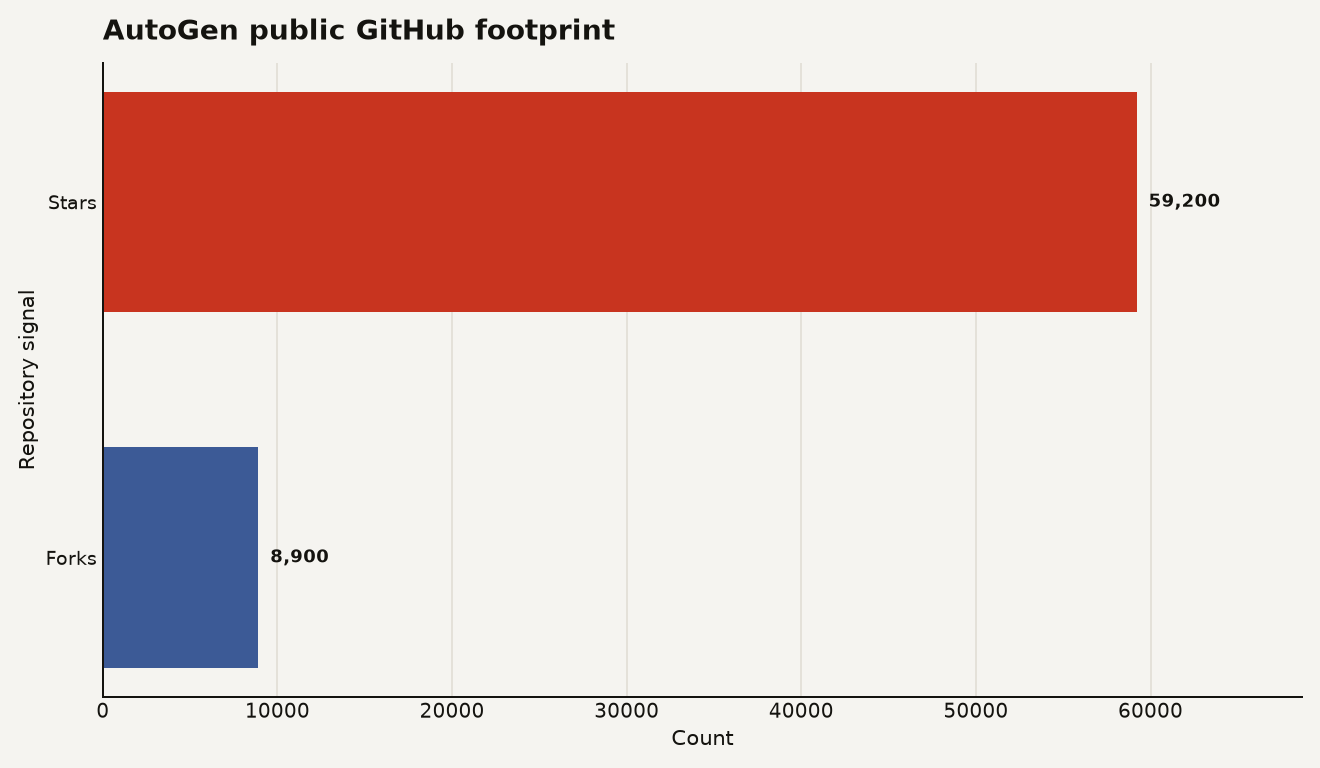
One malicious page chained three AutoGen Studio weaknesses into command execution. AutoJack is a host RCE warning for AI agent prototypes.
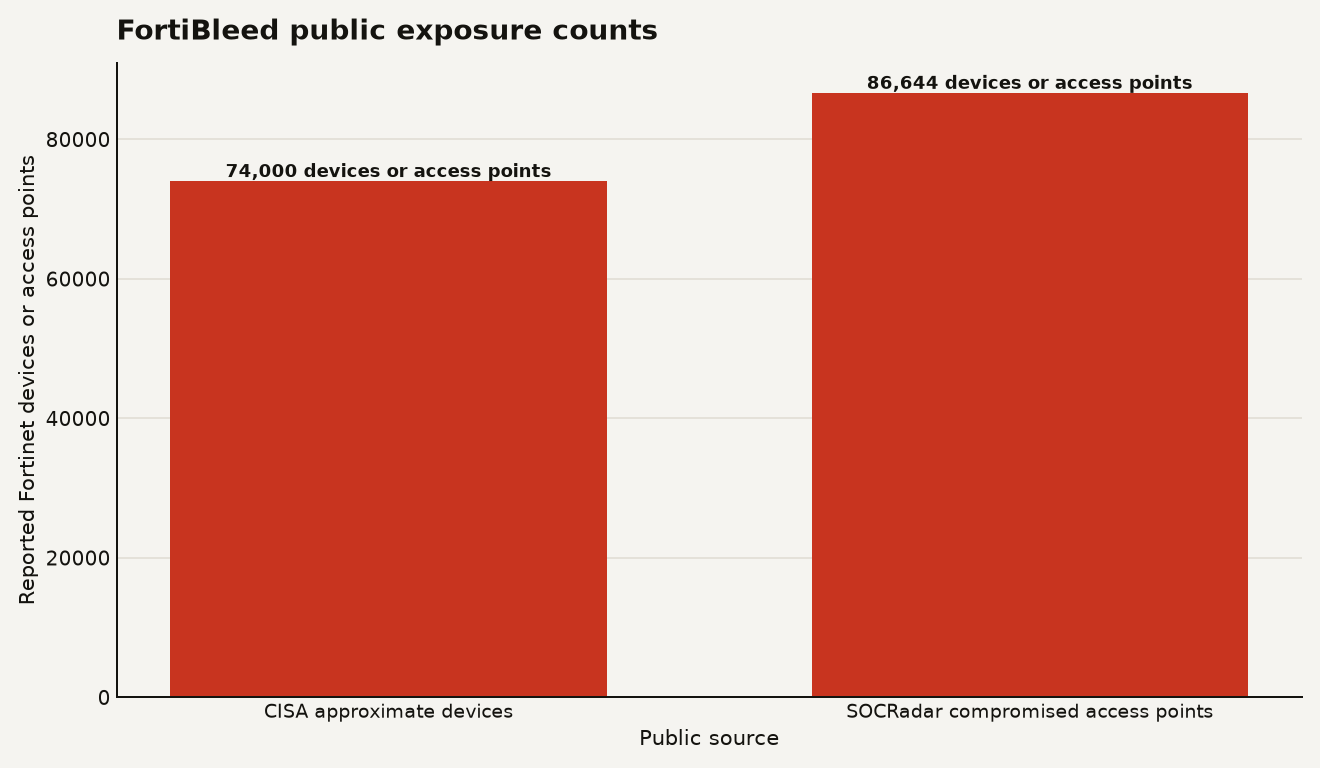
Up to 86,644 devices are reported in the FortiBleed FortiGate credential exposure campaign. Rotate, isolate and investigate now.
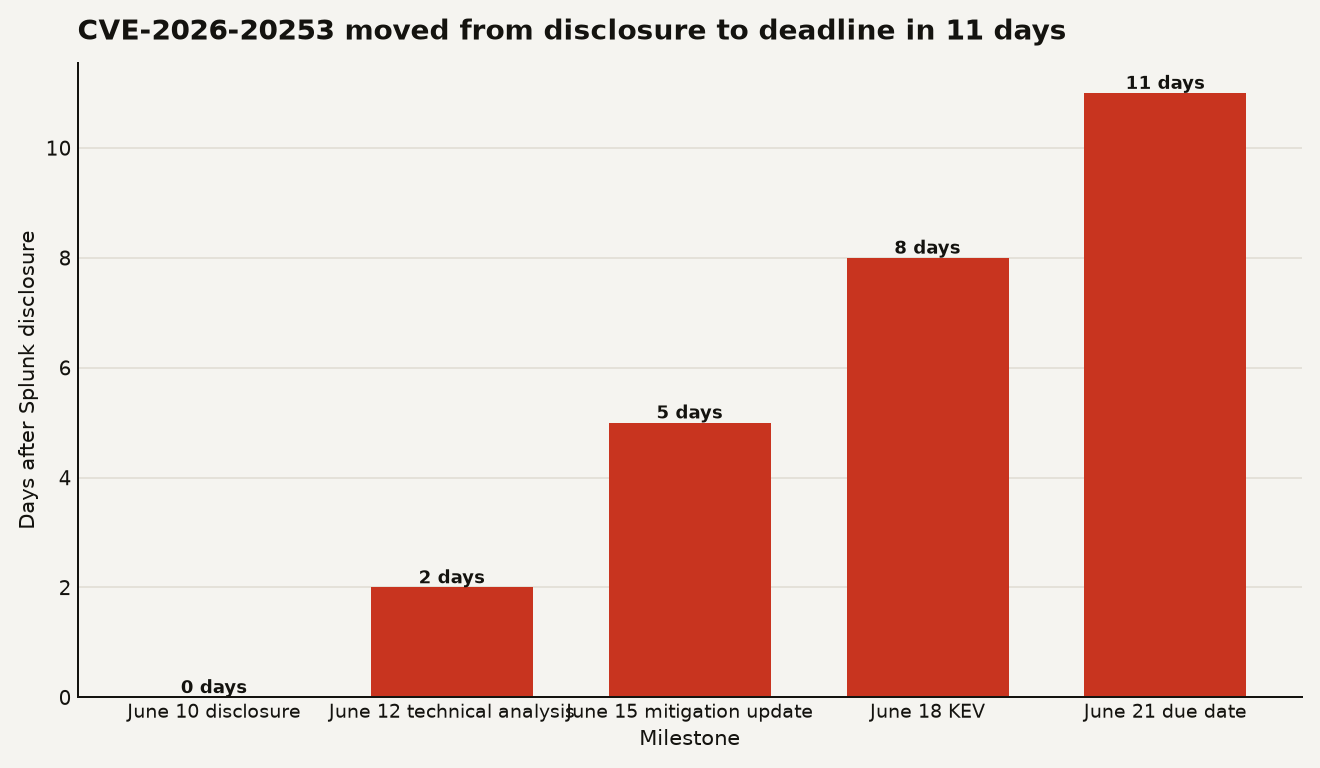
Exposed Splunk Enterprise 10.0 and 10.2 nodes need patching by June 21 for the actively exploited critical flaw CVE-2026-20253.
Mastra npm supply chain attack exposed AI build pipelines through more than 140 packages, so treat installs as secret exposure events.