Cyber security
Unpatched NetScaler RCE zero-days force weekend shutdowns
With no fix available for two exploited Citrix NetScaler RCE zero-days, operators must isolate or shut down appliances before Monday.
12 stories tagged rce.
With no fix available for two exploited Citrix NetScaler RCE zero-days, operators must isolate or shut down appliances before Monday.
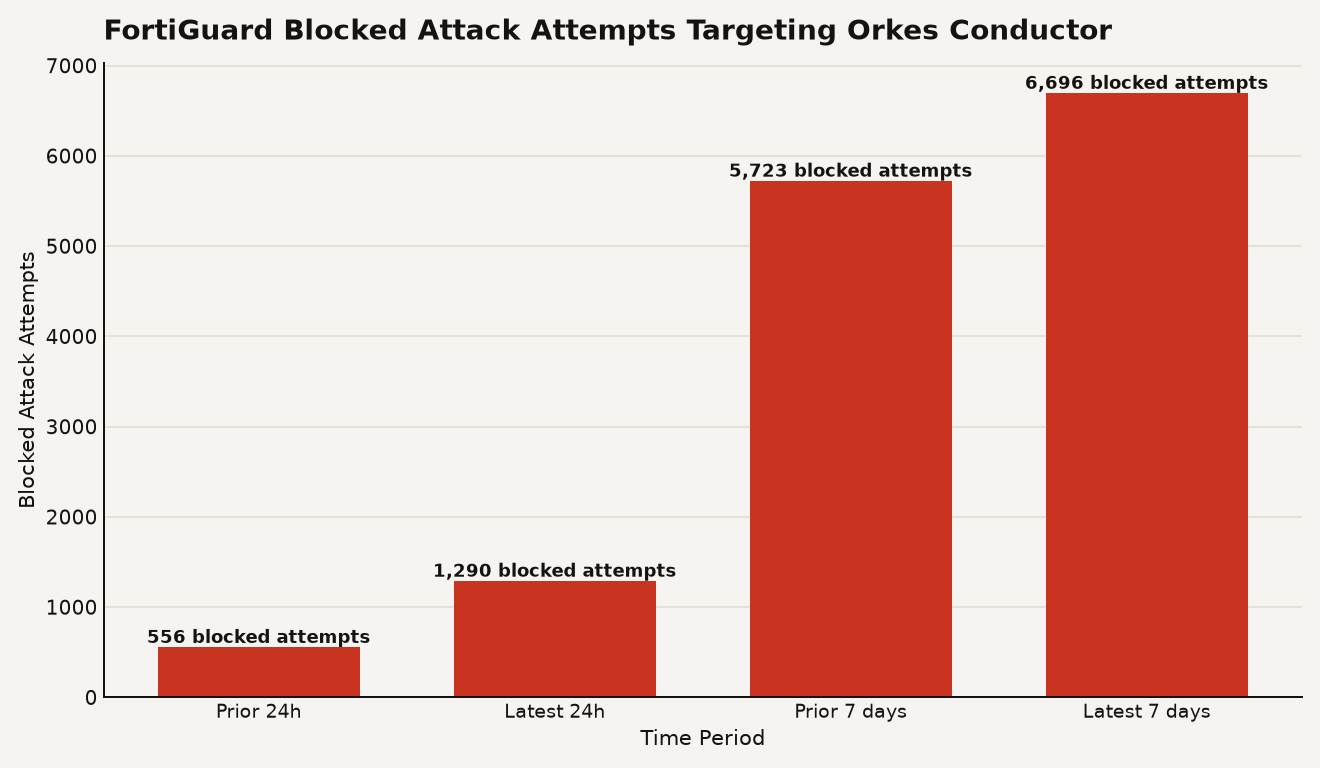
Exploited since August 2026, Orkes Conductor CVE-2026-58138 is a CVSS 9.8 unauthenticated RCE in GraalVM script evaluators. Upgrade to 3.30.2.
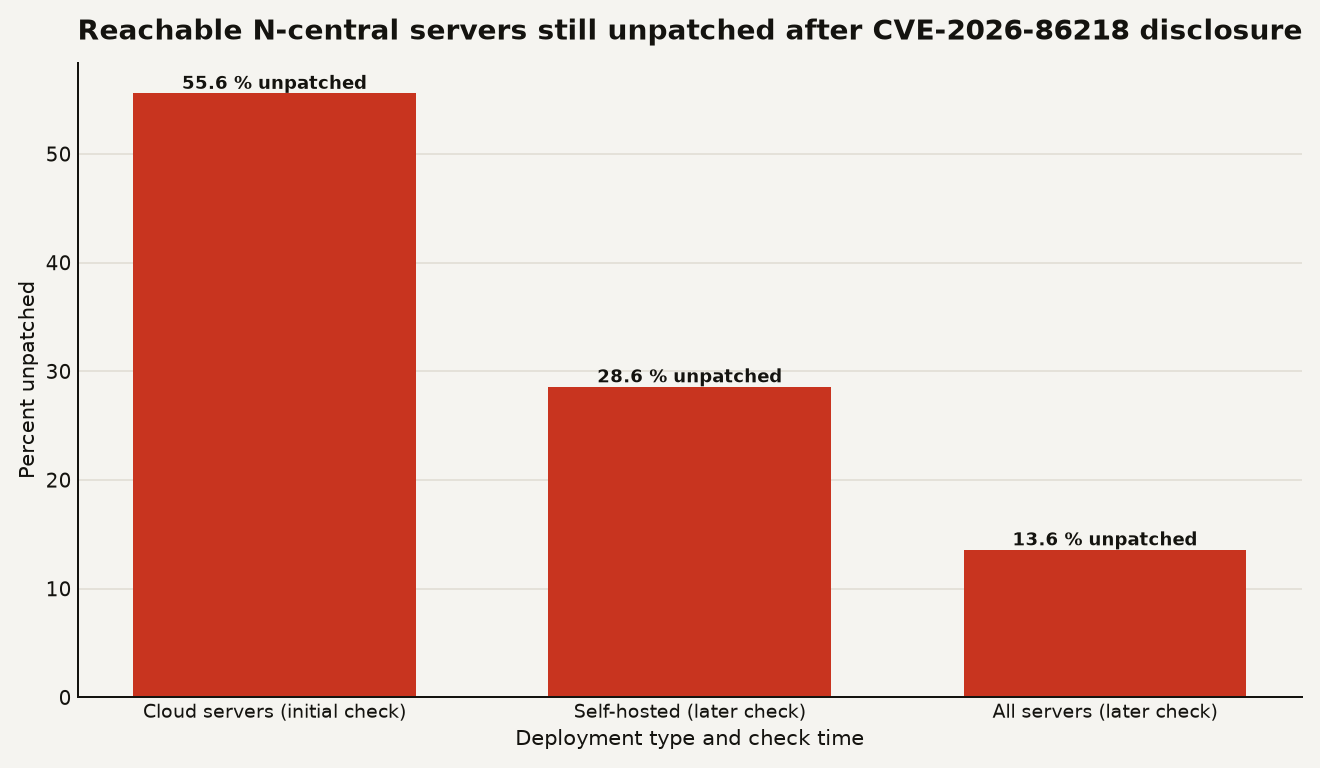
About 1,500 N-central servers are exposed to CVE-2026-86218, a CVSS 10.0 pre-auth RCE, with attacks reported. On-prem needs build 2026.3.1.14 now.
Langflow RCE flaws face active exploitation with over 15,000 successful attacks. Attackers harvest AI provider keys and cloud credentials from exposed instances.
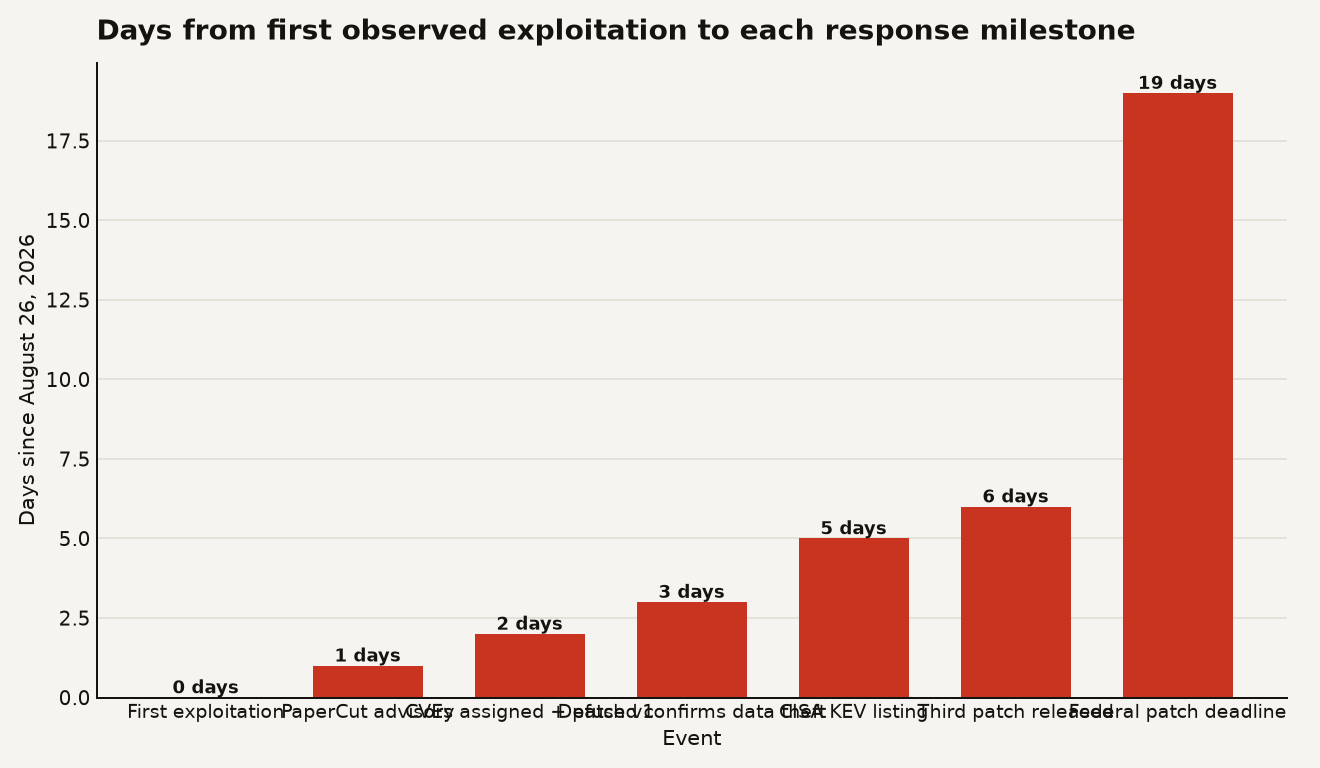
PaperCut NG/MF zero-day chain CVE-2026-81578 and CVE-2026-82078 enables pre-auth RCE on print servers. CISA added both to KEV with a September 14 patch deadline.
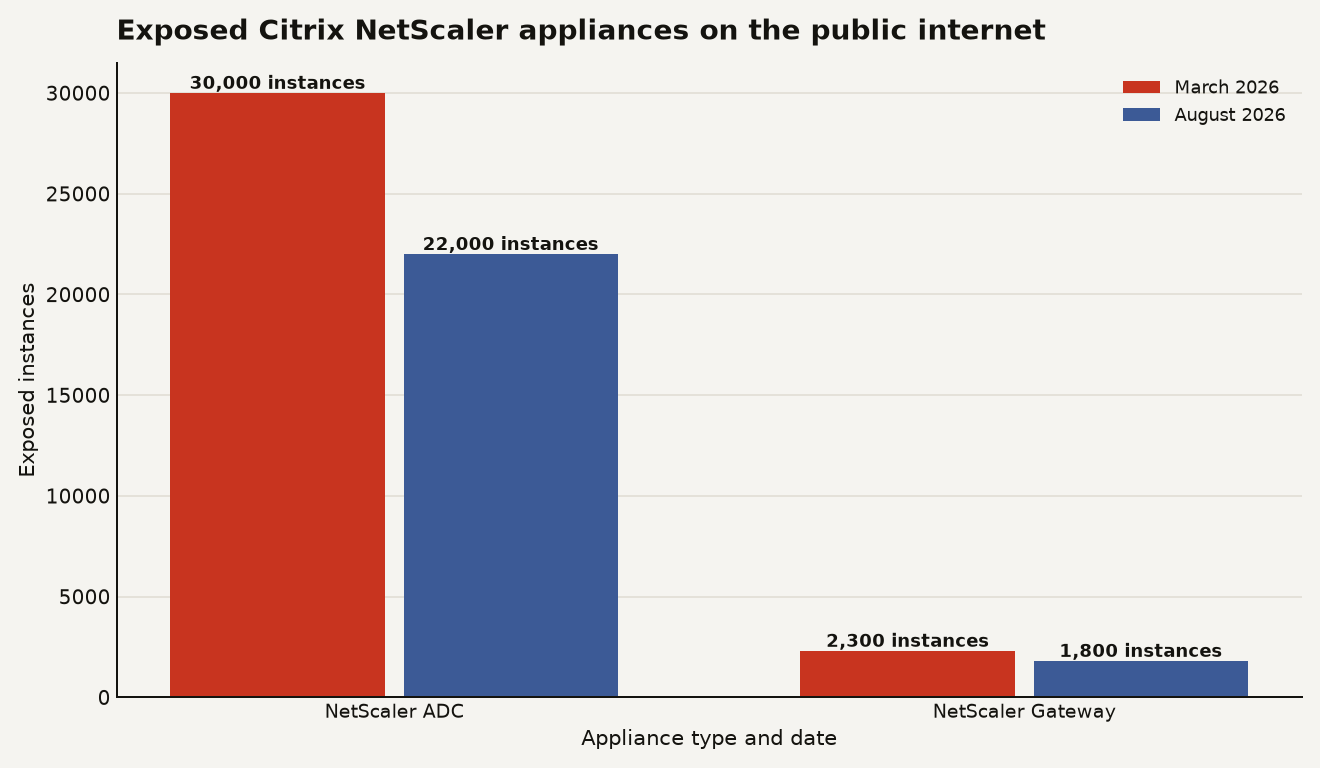
Web shells are turning up on devices hit through Citrix NetScaler RCE flaw CVE-2026-8452. CISA orders patching by Saturday, August 29.
Next.js patches two critical unauthenticated RCE vulnerabilities in the August 2026 security release. AVIF image optimization and Windows filesystem path traversal both expose self-hosted servers. Upgrade to 15.5.24 or 16.3.3 immediately.
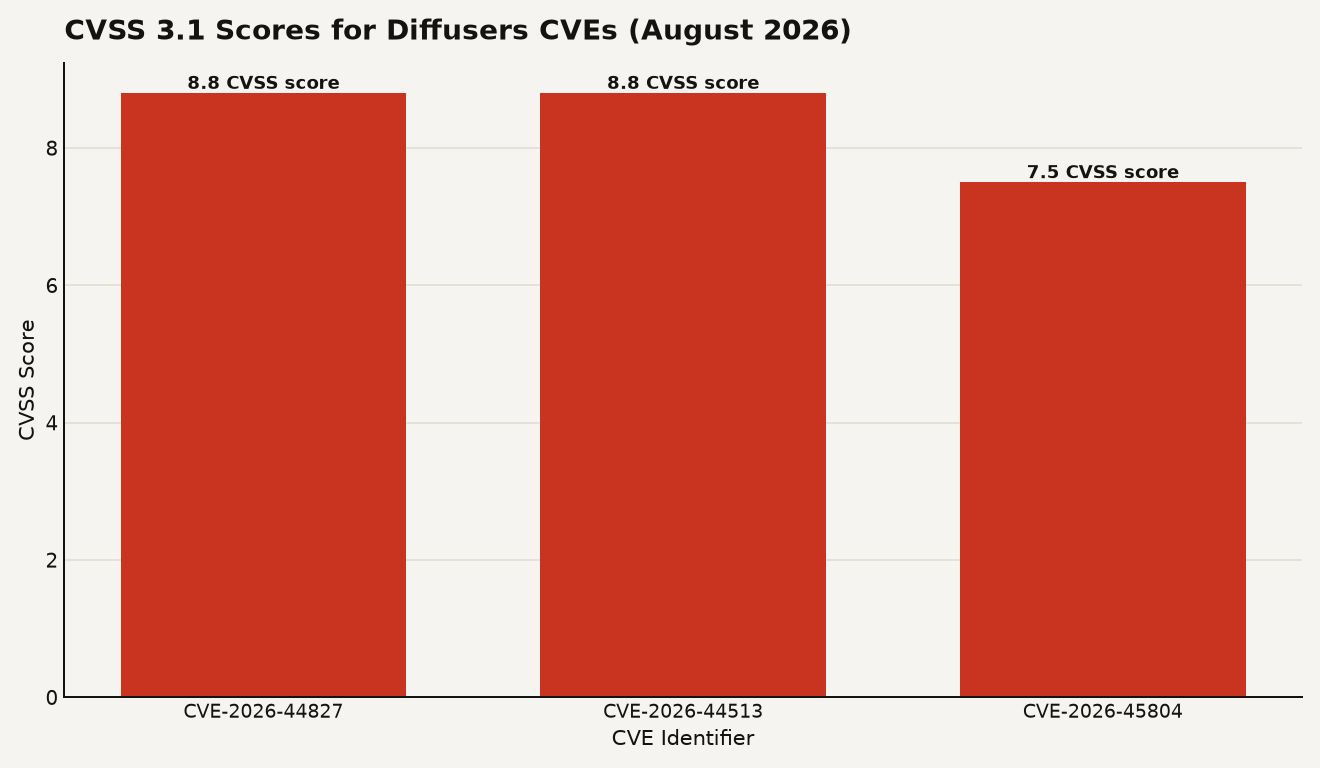
Hugging Face Diffusers vulnerabilities bypass trust_remote_code in three CVEs rated 8.8 and 7.5, enabling silent RCE from model repos. Patch now.
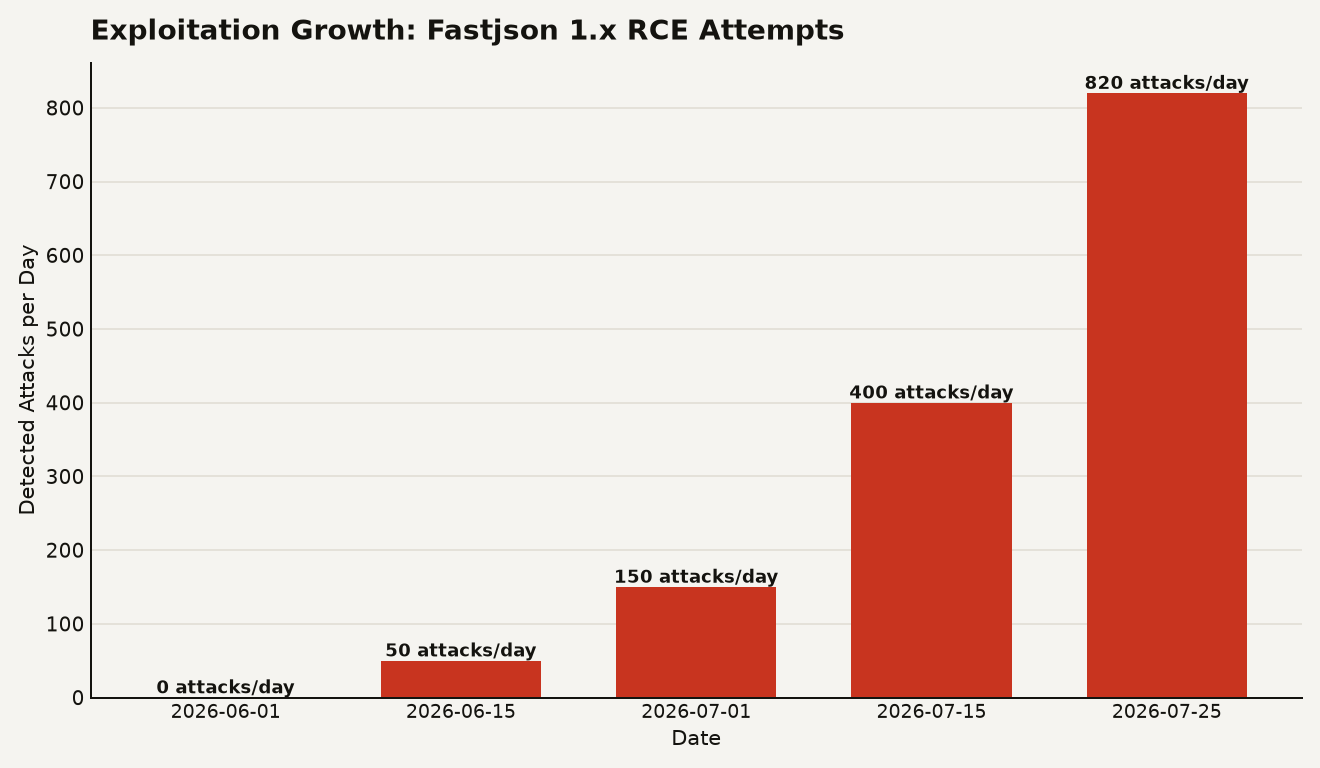
Fastjson 1.x RCE (CVE-2026-16723) is a critical CVSS 9.0 flaw actively exploited in Spring Boot apps with no official patch available. Block Fastjson 1.x endpoints, migrate to Jackson, and demand autotype safelists.
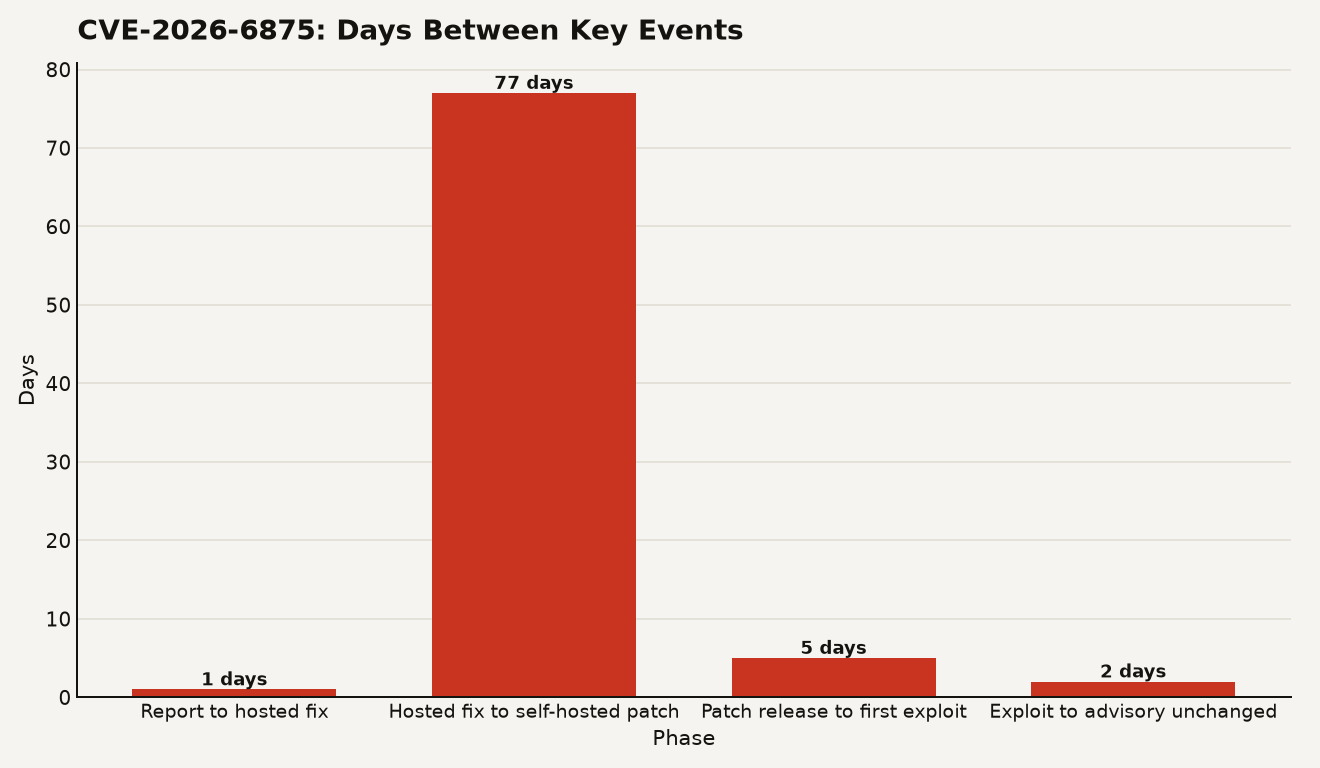
A CVSS 9.5 pre-auth sandbox escape in the AI Platform, ServiceNow CVE-2026-6875 is now actively exploited. Patch self-hosted instances immediately.
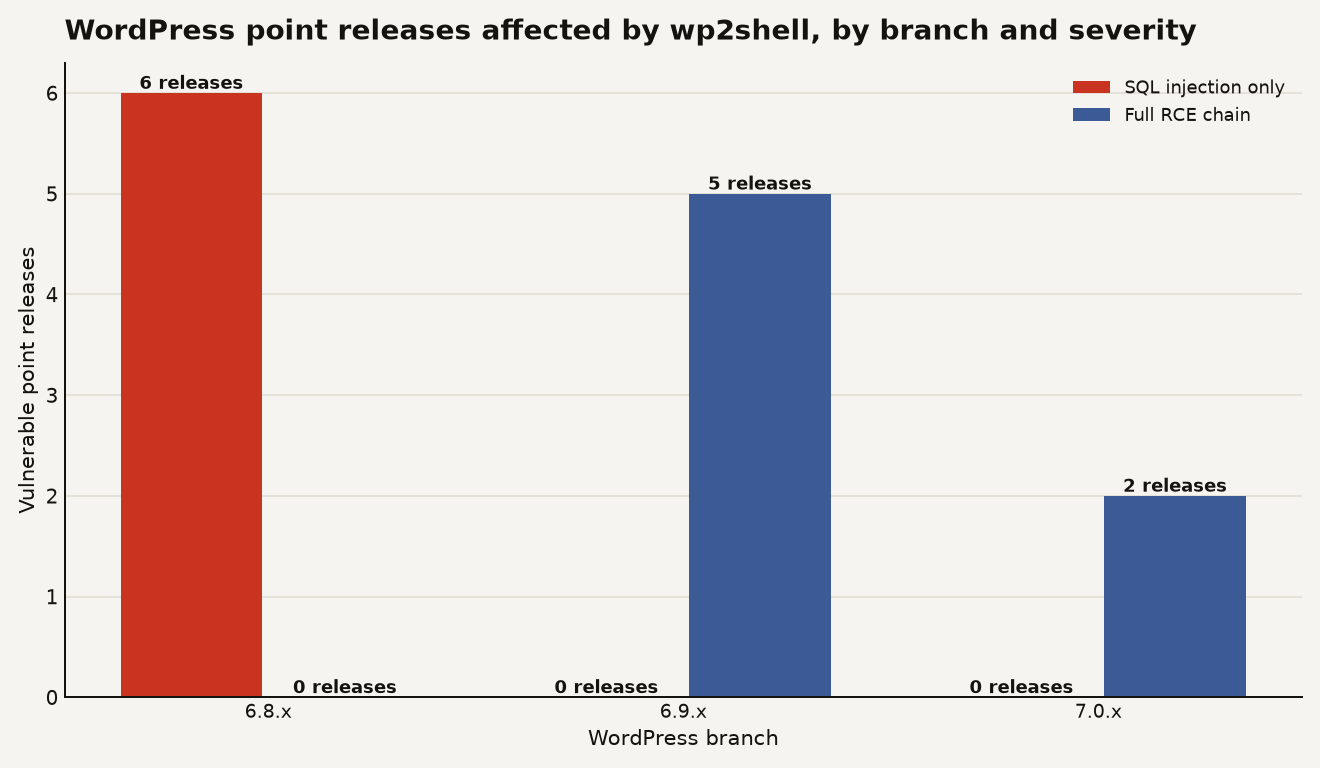
Two WordPress Core CVEs form wp2shell, a pre-auth RCE chain that lets anonymous attackers run code on 6.9 and 7.0 sites with no plugins.
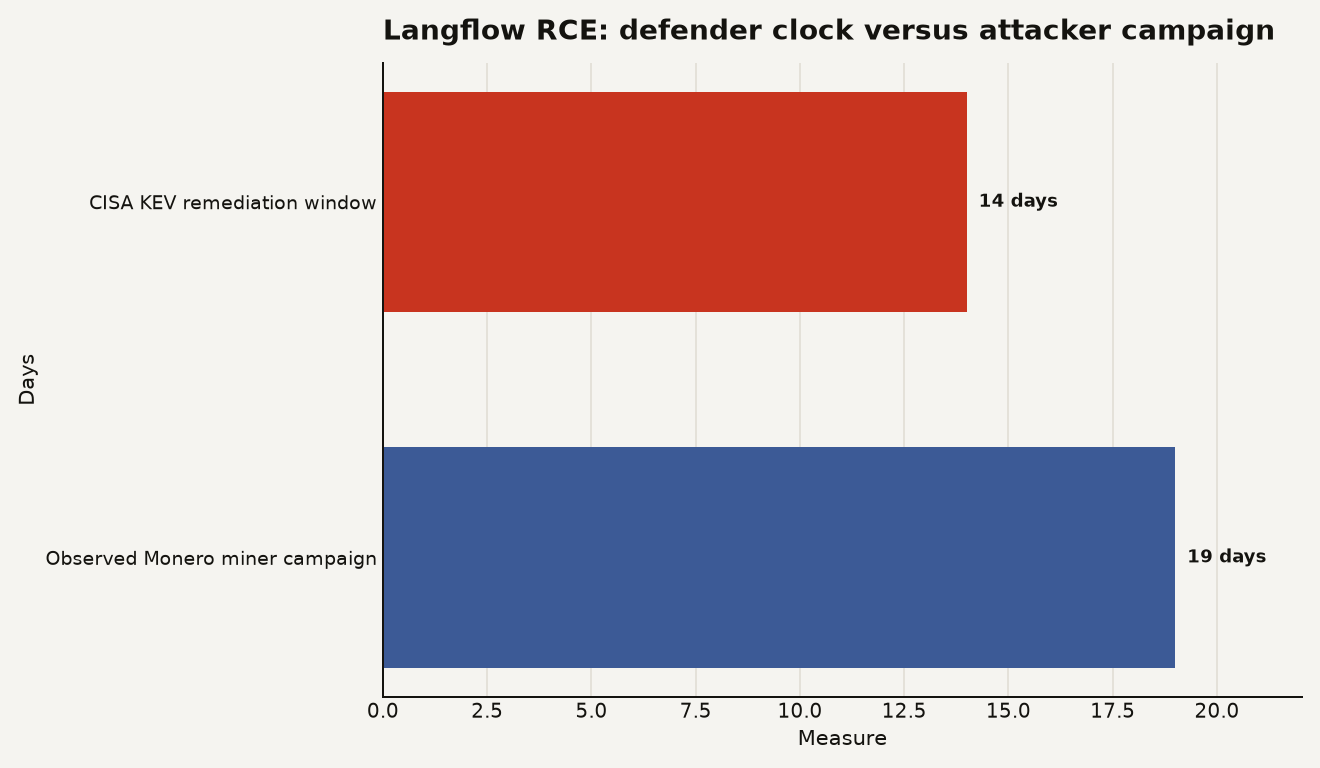
Attackers use a Langflow RCE to mine Monero on exposed AI app endpoints. Patch, isolate, and treat public workflows as attack surface.