Cyber security
Keycloak password reset flaw lets attackers take over any account
Rated CVSS 9.1, CVE-2026-18963 in Keycloak's password reset flow lets unauthenticated attackers skip email checks and take over any account.
2 stories tagged identity.
Rated CVSS 9.1, CVE-2026-18963 in Keycloak's password reset flow lets unauthenticated attackers skip email checks and take over any account.
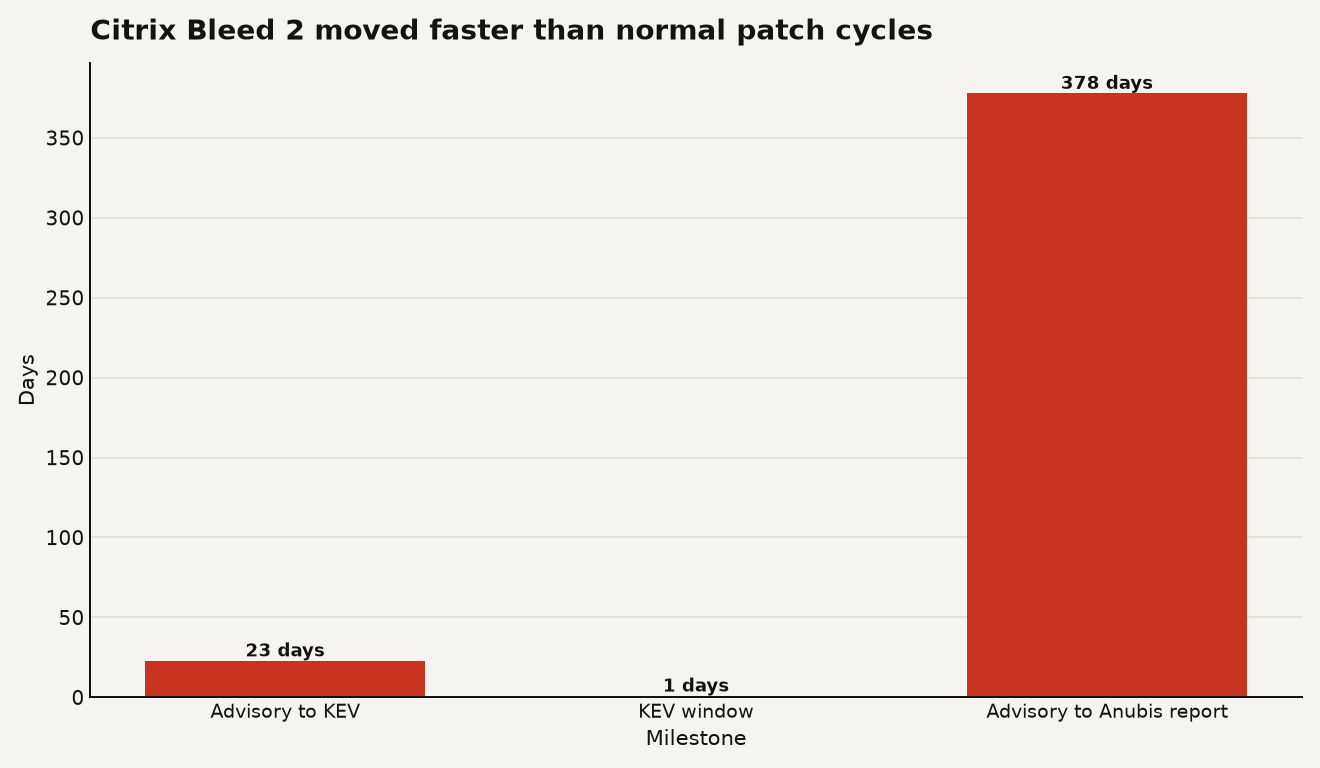
Anubis ransomware now uses Citrix Bleed 2 as an access path. Patch NetScaler, kill sessions, and hunt RMM and credential abuse.