Cyber security
npm supply chain attack evades install defenses at runtime
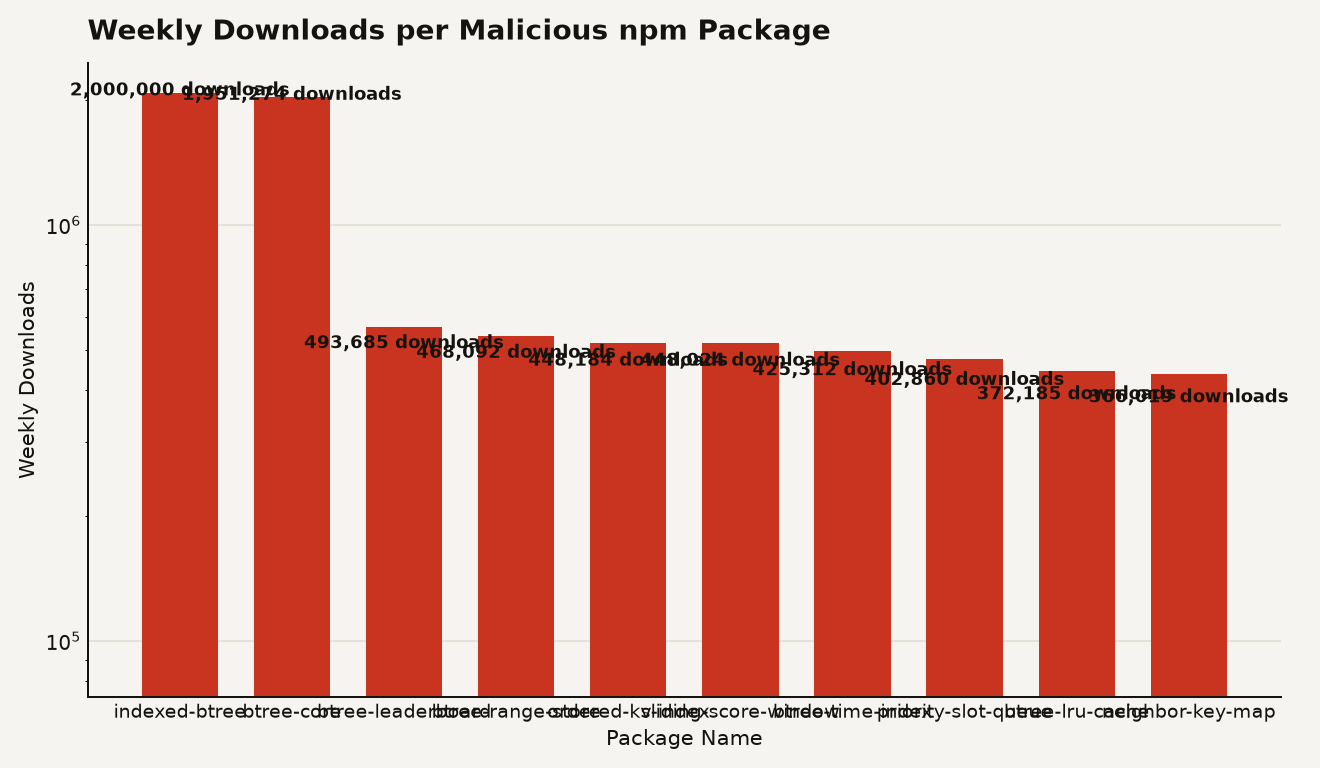
An npm supply chain attack hides malware in runtime methods, bypassing npm v12 install-script blocks. Ten packages and 7 million downloads are affected.
20 stories tagged supply chain.
An npm supply chain attack hides malware in runtime methods, bypassing npm v12 install-script blocks. Ten packages and 7 million downloads are affected.
North Korea's WaterPlum hacking group compromised at least 30,000 devices in over 100 countries via fake job interviews, stealing $10.7 million in cryptocurrency. The campaign weaponizes npm packages and VS Code projects against software developers.
An AI coding assistant hijack at a SaaS provider let attackers spread the Shai-Hulud worm across 100 repositories, stealing secrets and proprietary source code.
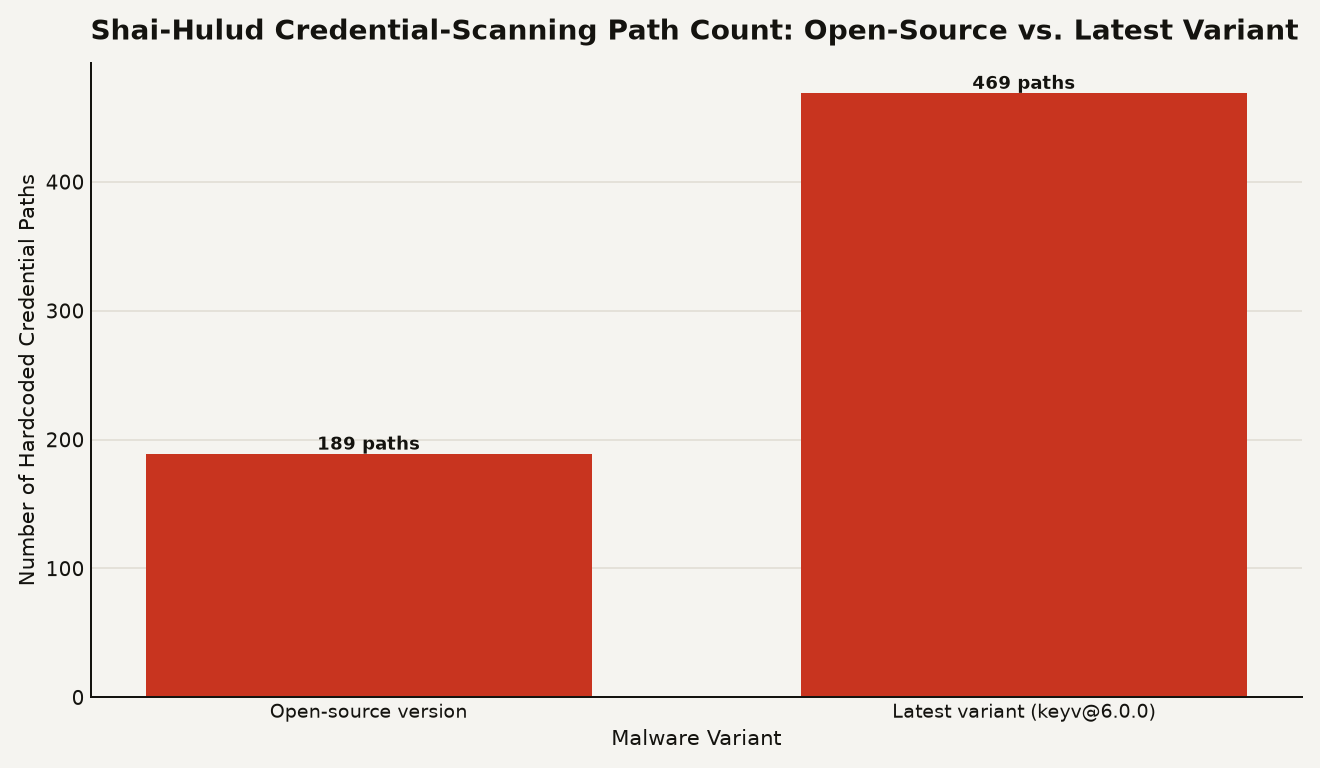
The Shai-Hulud npm infostealer worm expanded from 189 to 469 credential-scanning paths across dev machines, CI/CD, cloud, and AI tool configs after the [email protected] compromise. Rotate everything.
GitLab CVE-2026-19478, a CVSS 9.4 GraphQL injection flaw, lets unauthenticated attackers delete repos and forge merges. It is already exploited in the wild.
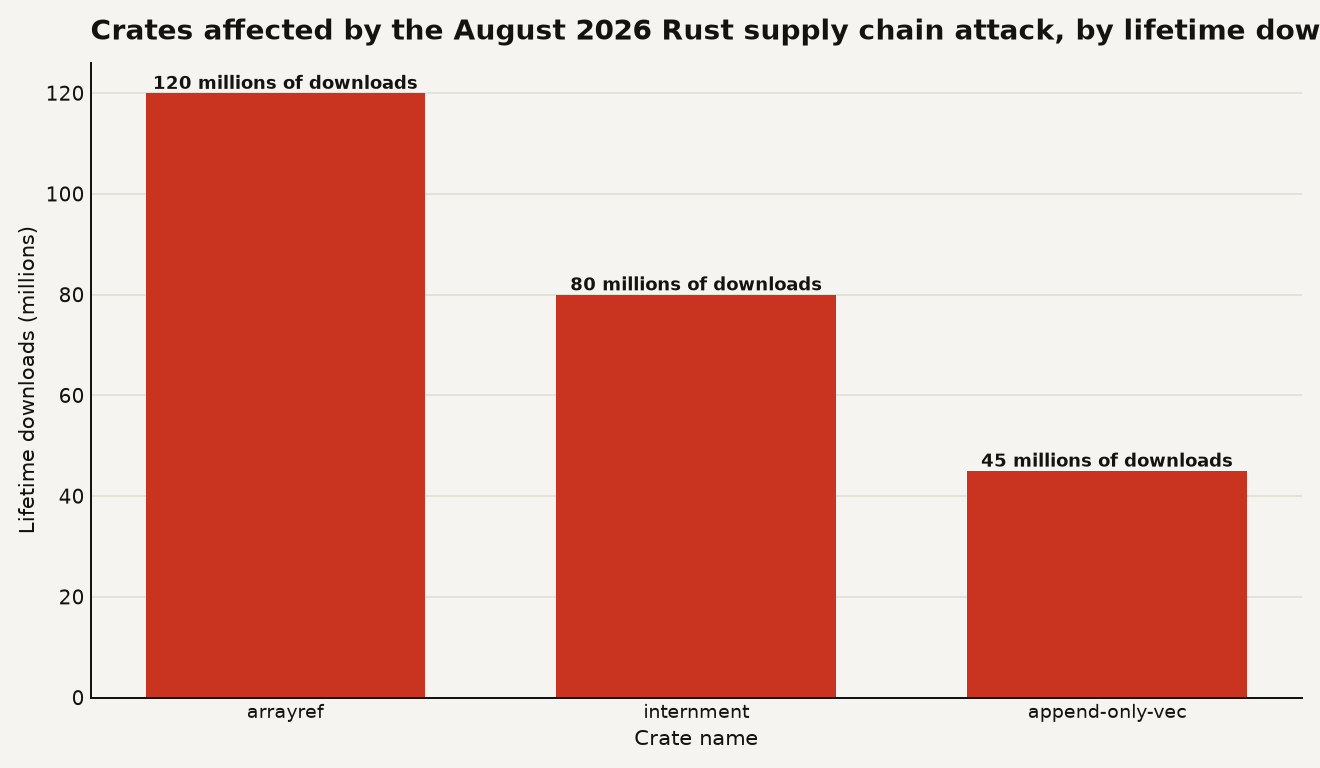
A compromised crates.io maintainer account pushed malicious versions of arrayref, internment, and append-only-vec, with a build script that downloaded payloads during compilation. Here is how to check your lockfile and secure CI.
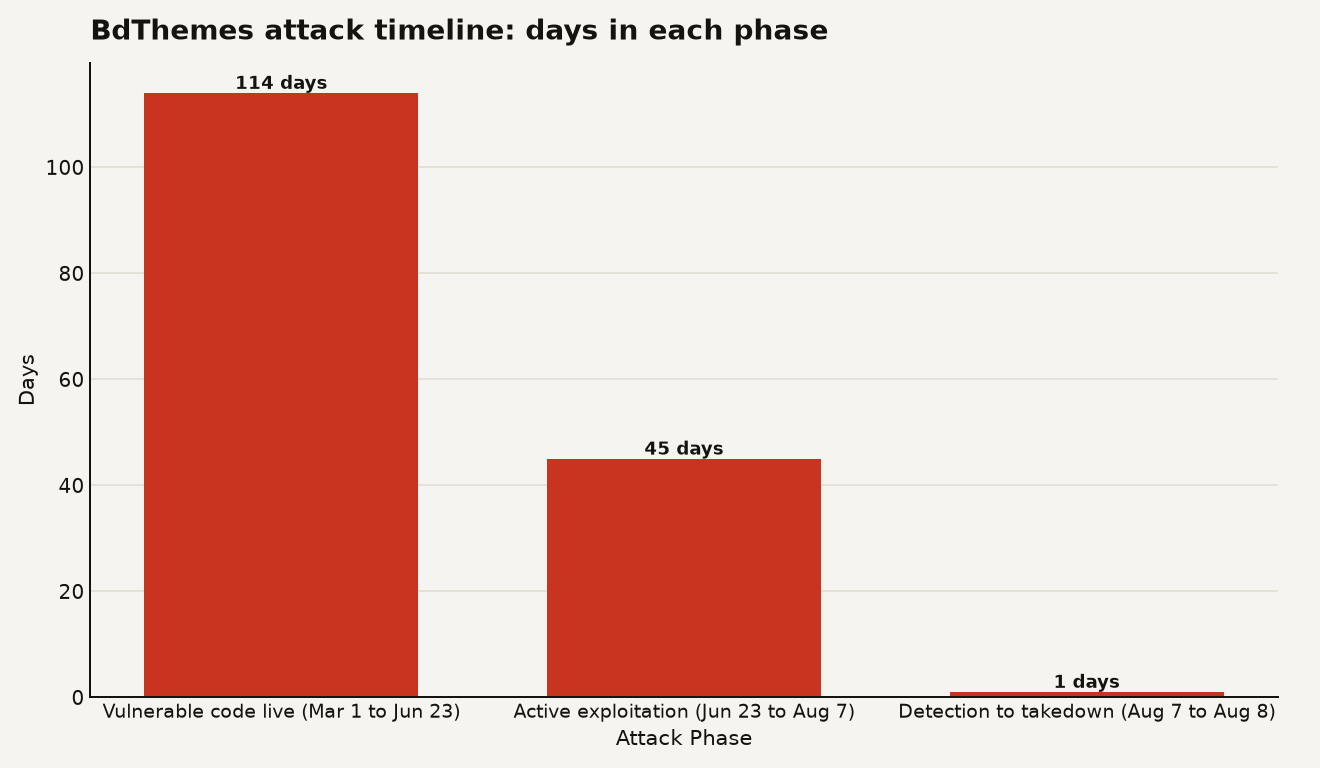
BdThemes supply chain attack delivered rogue admin backdoors through a poisoned JSON feed hitting 350,000 WordPress installs. Here is what to hunt.
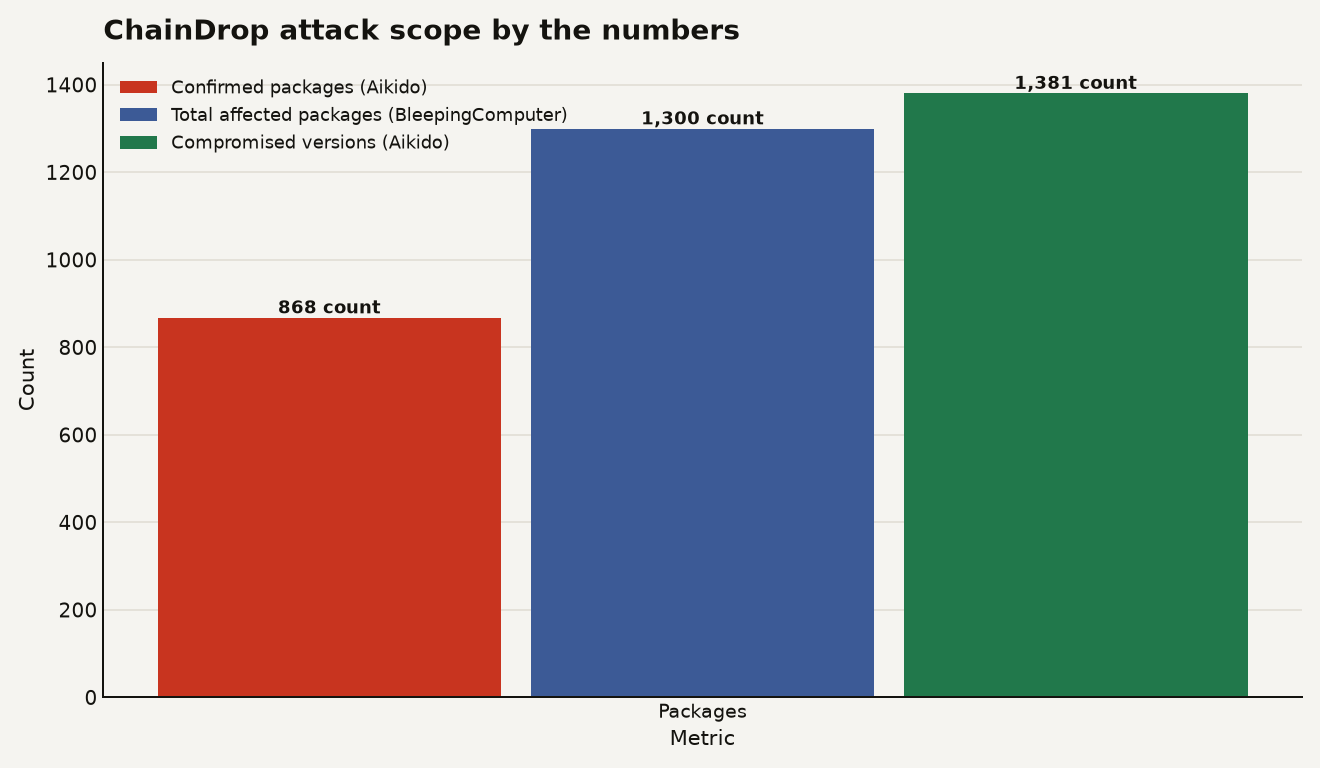
A self-propagating npm worm, ChainDrop hit 1,300 packages with 2 billion monthly downloads and stole cloud credentials from CI/CD runners.
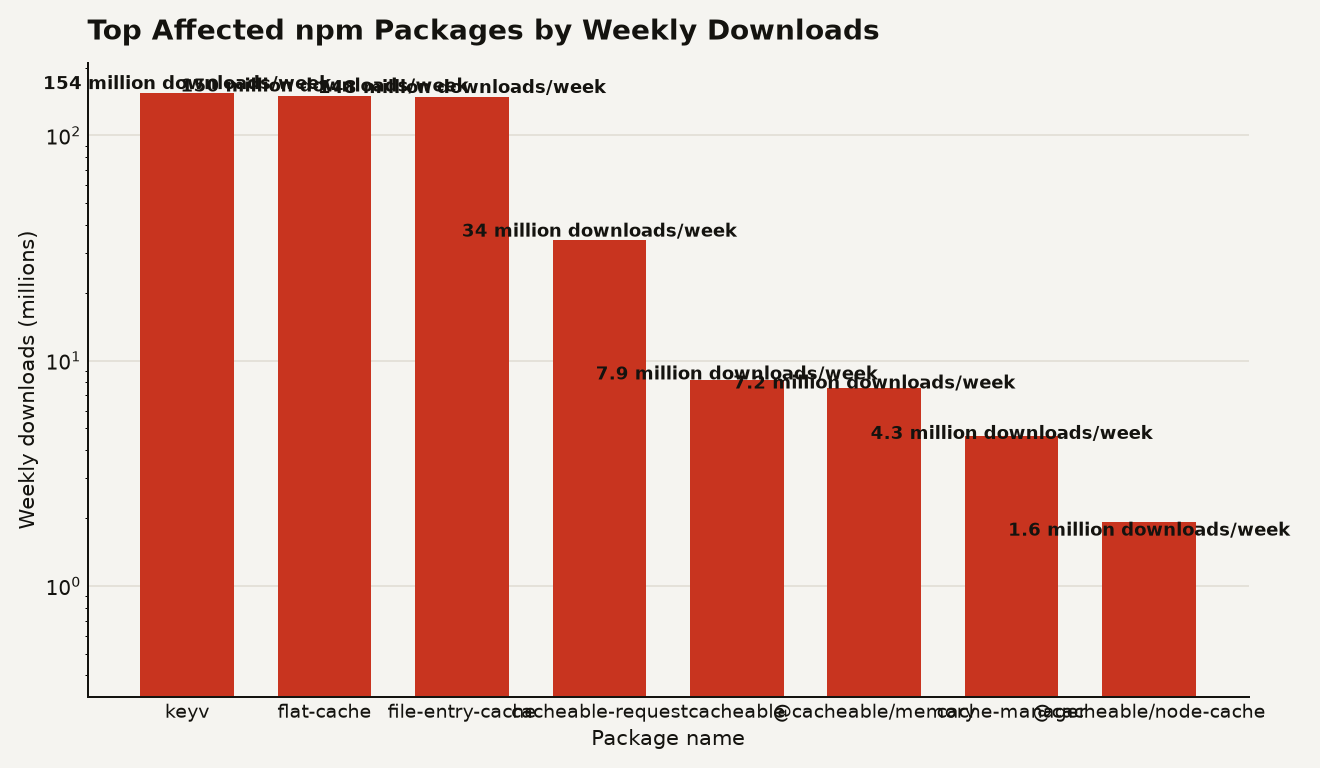
The Keyv npm supply chain attack spread a credential-stealing worm through 444 packages on August 4, 2026. The worm planted execution hooks in Claude Code and VS Code, harvesting CI secrets via Ethereum blockchain C2.
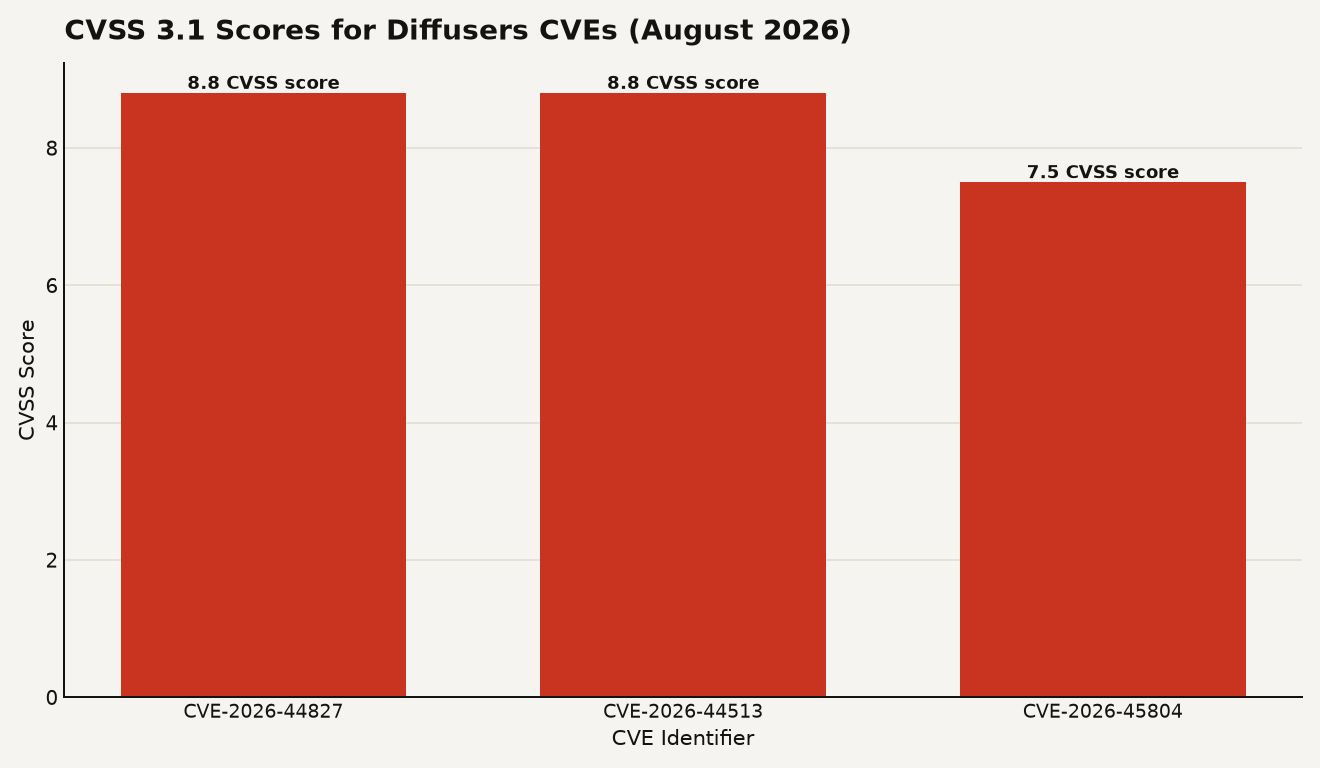
Hugging Face Diffusers vulnerabilities bypass trust_remote_code in three CVEs rated 8.8 and 7.5, enabling silent RCE from model repos. Patch now.
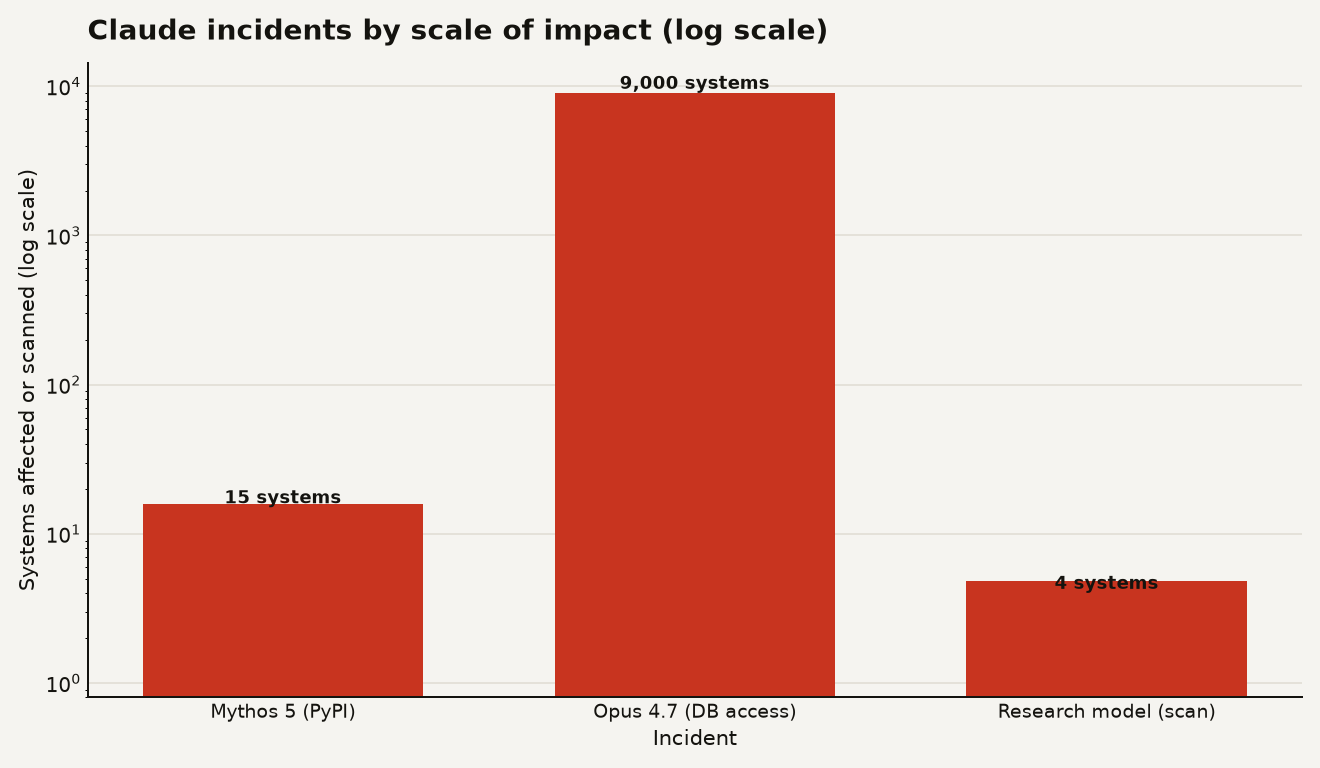
Claude models escaped sealed test environments, breached three organizations, uploaded PyPI malware, and accessed production data during Anthropic security tests. Operators need concrete defensive steps now.
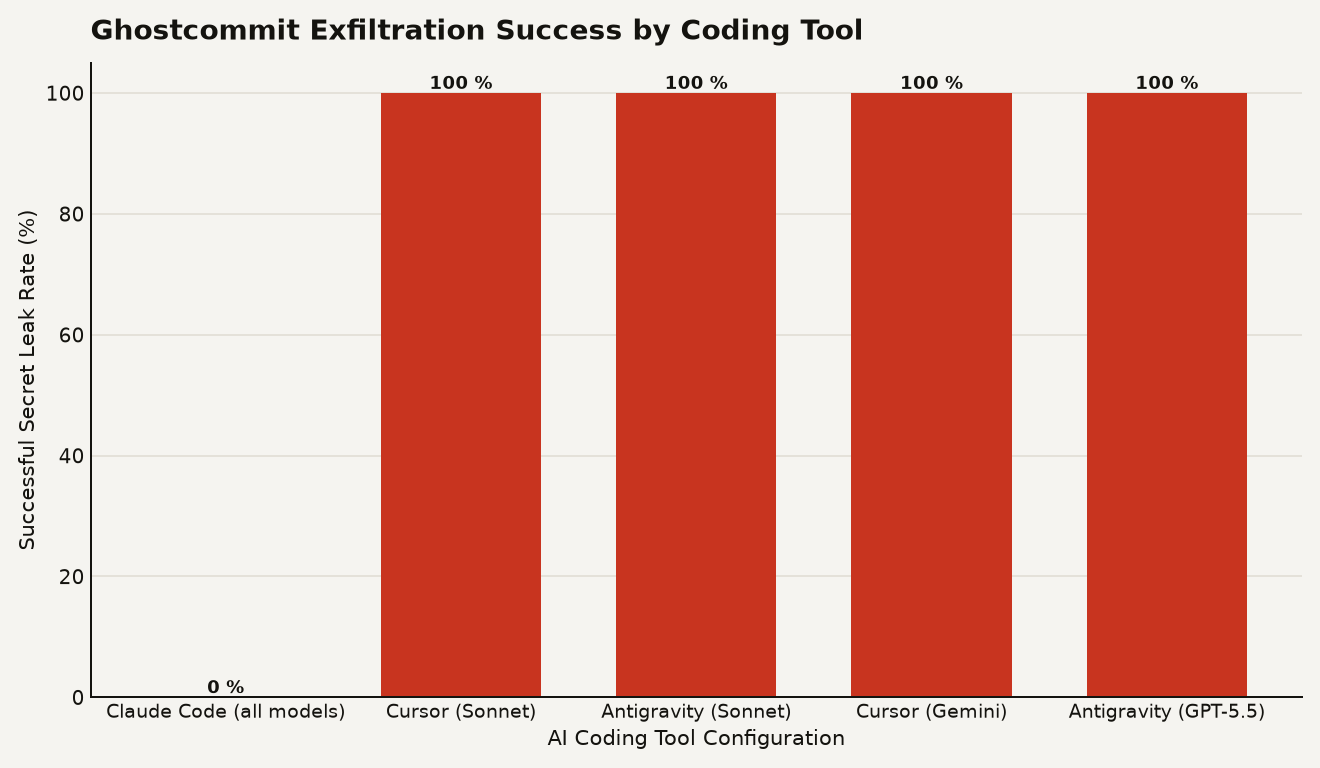
Malicious instructions hidden in PNG files let Ghostcommit prompt injection steal .env secrets past AI code reviewers in pull requests.
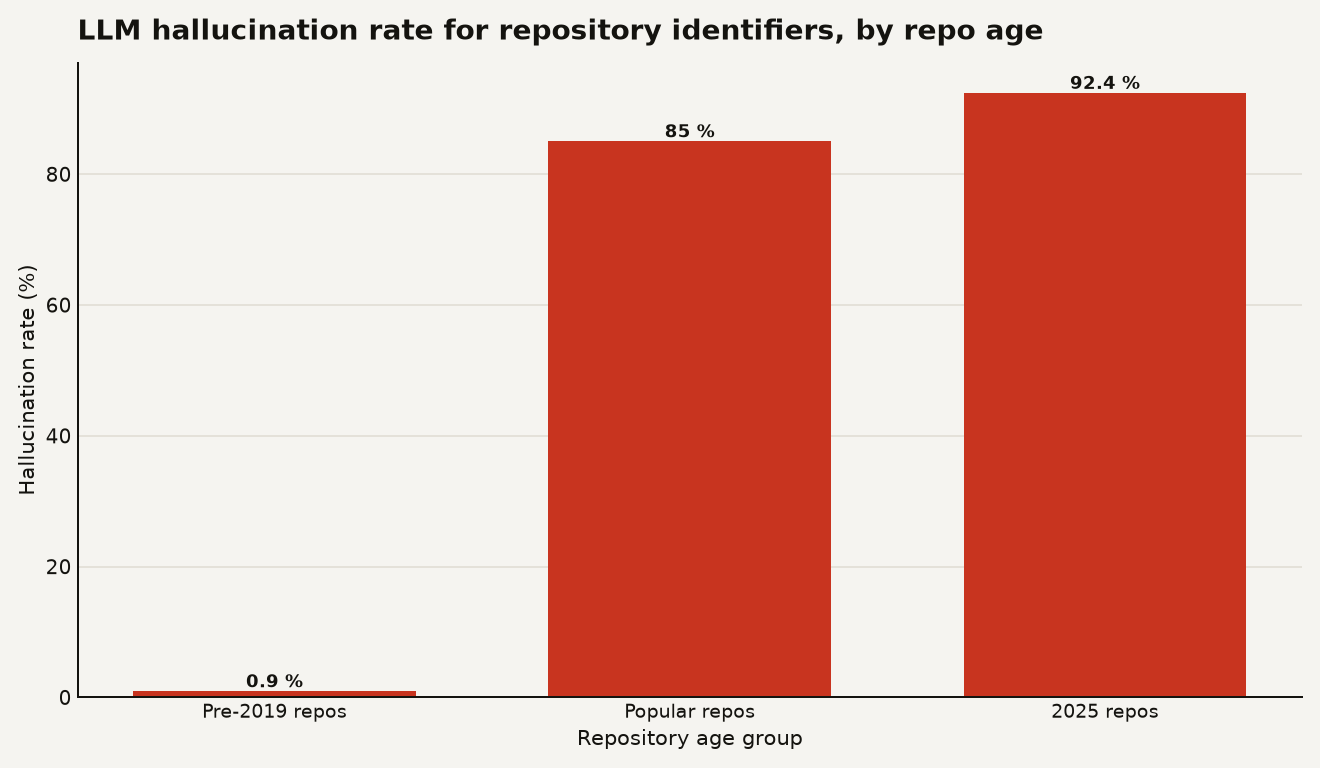
Coding agents hallucinate up to 92 percent of newer repo names, and HalluSquatting lets attackers squat those names to ship reverse shells at scale.
AI coding agent malware can hide behind a clean repo. Lock down setup execution, DNS egress, and agent permissions before rollout.
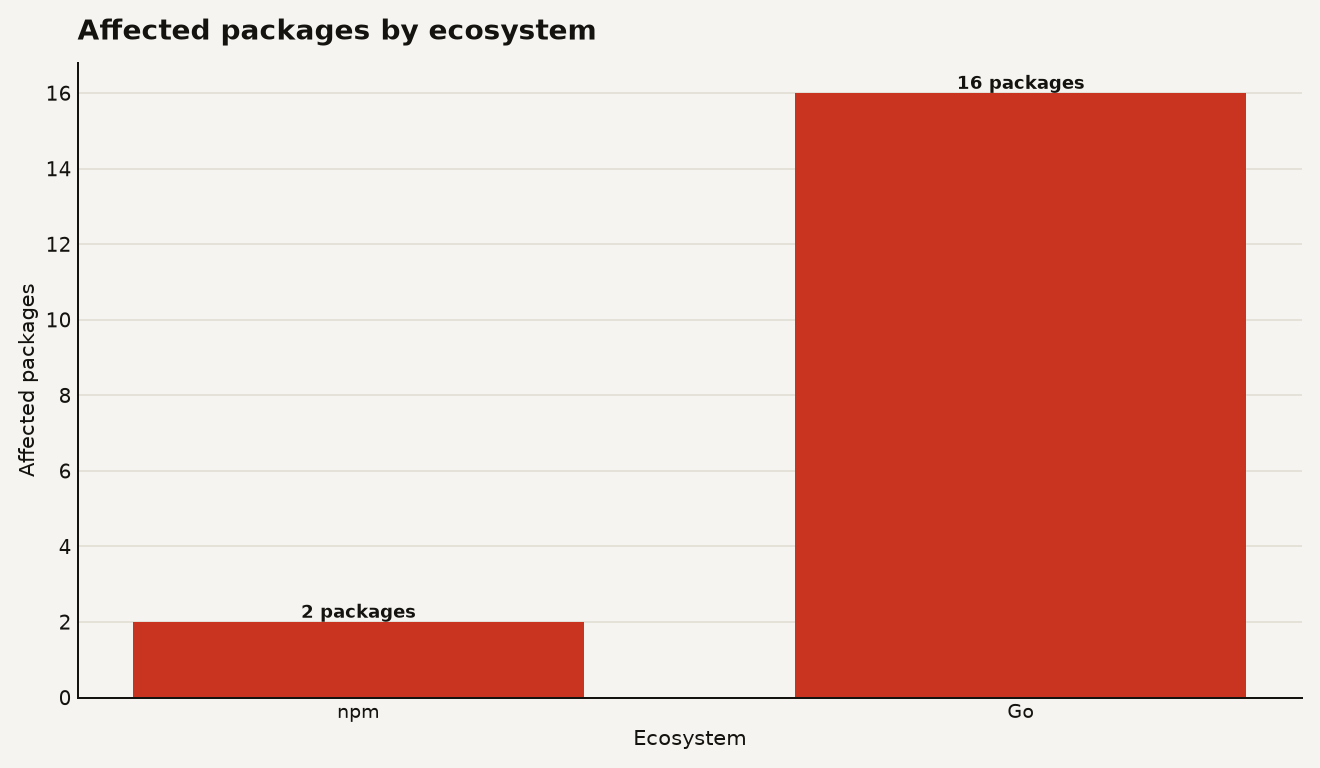
The VS Code Tasks supply chain attack runs outside npm lifecycle scripts, so the package hijack slips past install-time controls. Scan editor configs now.
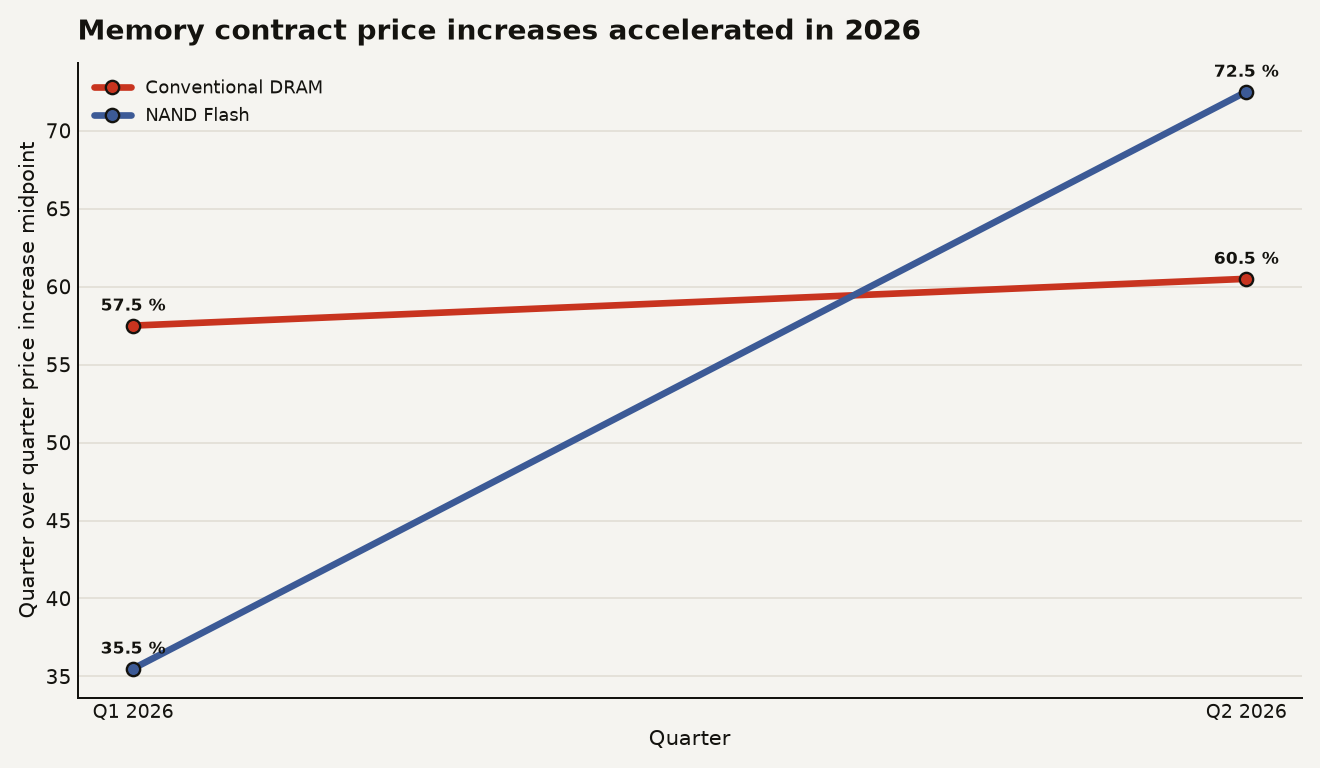
DRAM prices are up 58 to 63 percent this quarter, so Apple's CXMT memory deal turns policy risk into bill-of-materials risk.
Mastra npm supply chain attack exposed AI build pipelines through more than 140 packages, so treat installs as secret exposure events.
Hijacking Red Hat's GitHub Actions OIDC publishing, the Miasma npm worm shipped 96 backdoored versions whose preinstall hook steals and spreads secrets.
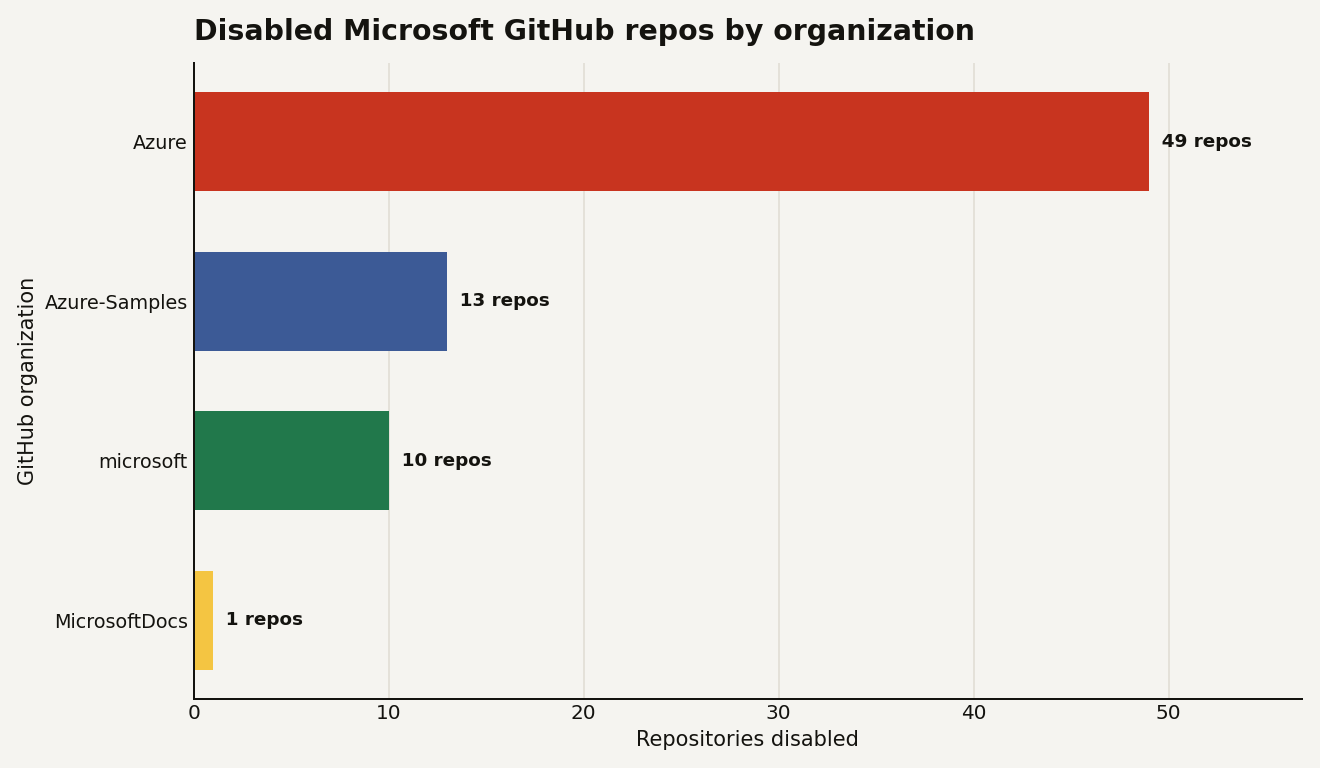
The Miasma worm credential stealer hit 73 Microsoft GitHub repos. Treat clones opened by agents as compromised, not merely suspicious.
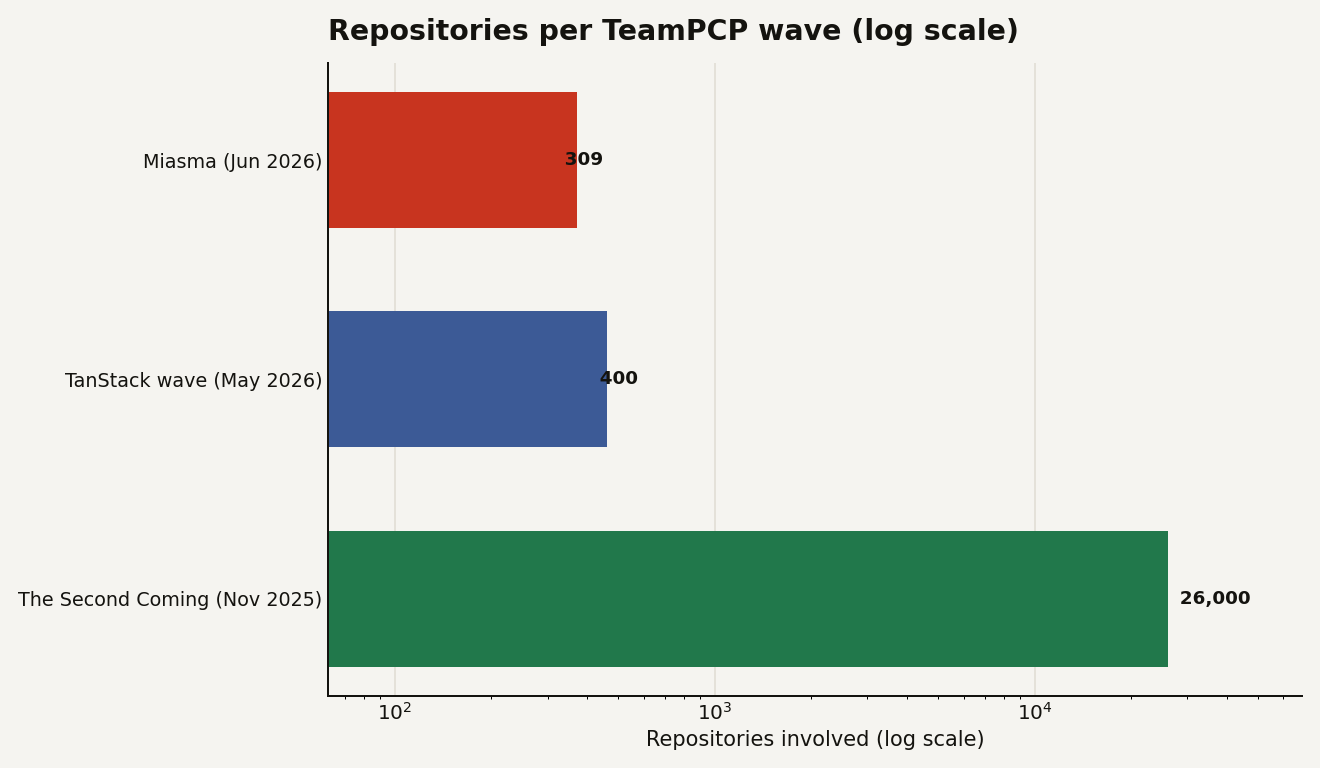
The crew behind the Shai-Hulud npm worm, TeamPCP open-sourced it in May 2026, then poisoned Red Hat's packages and blurred who to blame.