Cyber security
npm supply chain attack evades install defenses at runtime
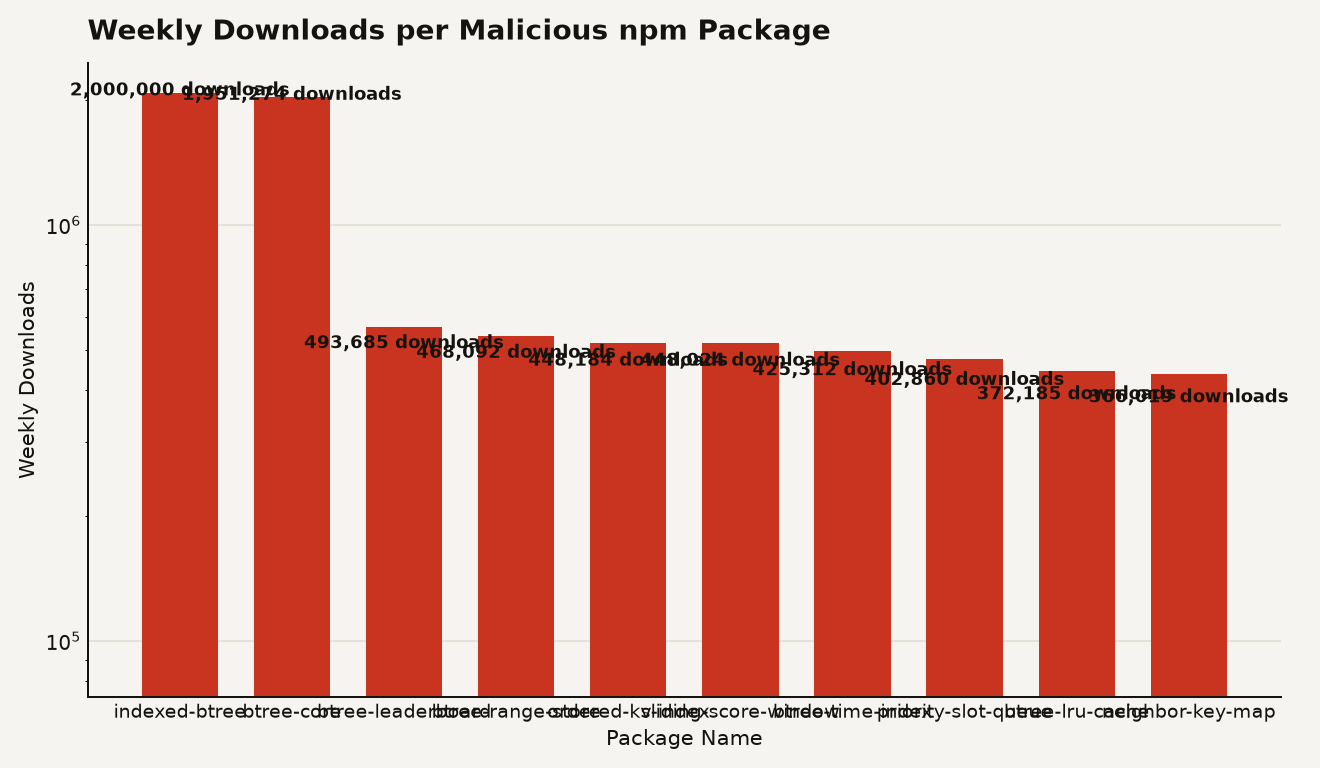
An npm supply chain attack hides malware in runtime methods, bypassing npm v12 install-script blocks. Ten packages and 7 million downloads are affected.
8 stories tagged npm.
An npm supply chain attack hides malware in runtime methods, bypassing npm v12 install-script blocks. Ten packages and 7 million downloads are affected.
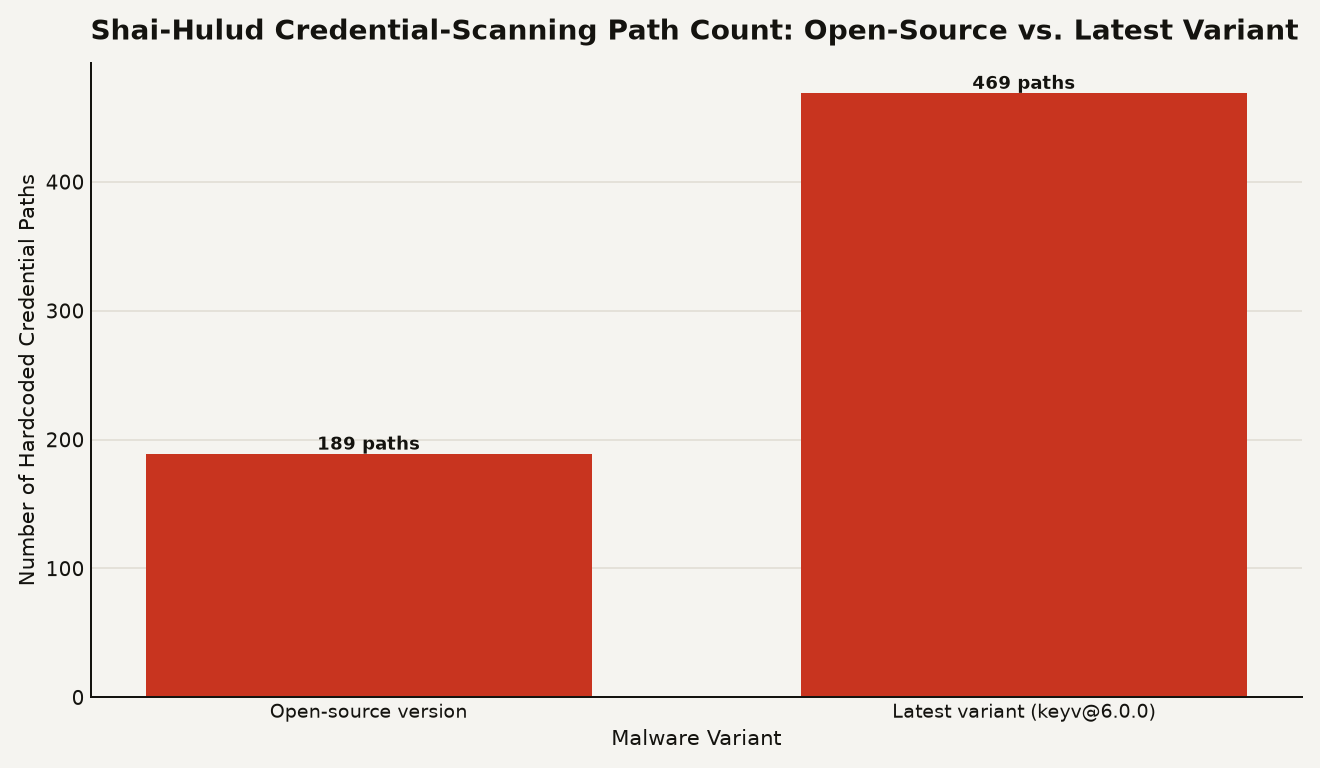
The Shai-Hulud npm infostealer worm expanded from 189 to 469 credential-scanning paths across dev machines, CI/CD, cloud, and AI tool configs after the [email protected] compromise. Rotate everything.
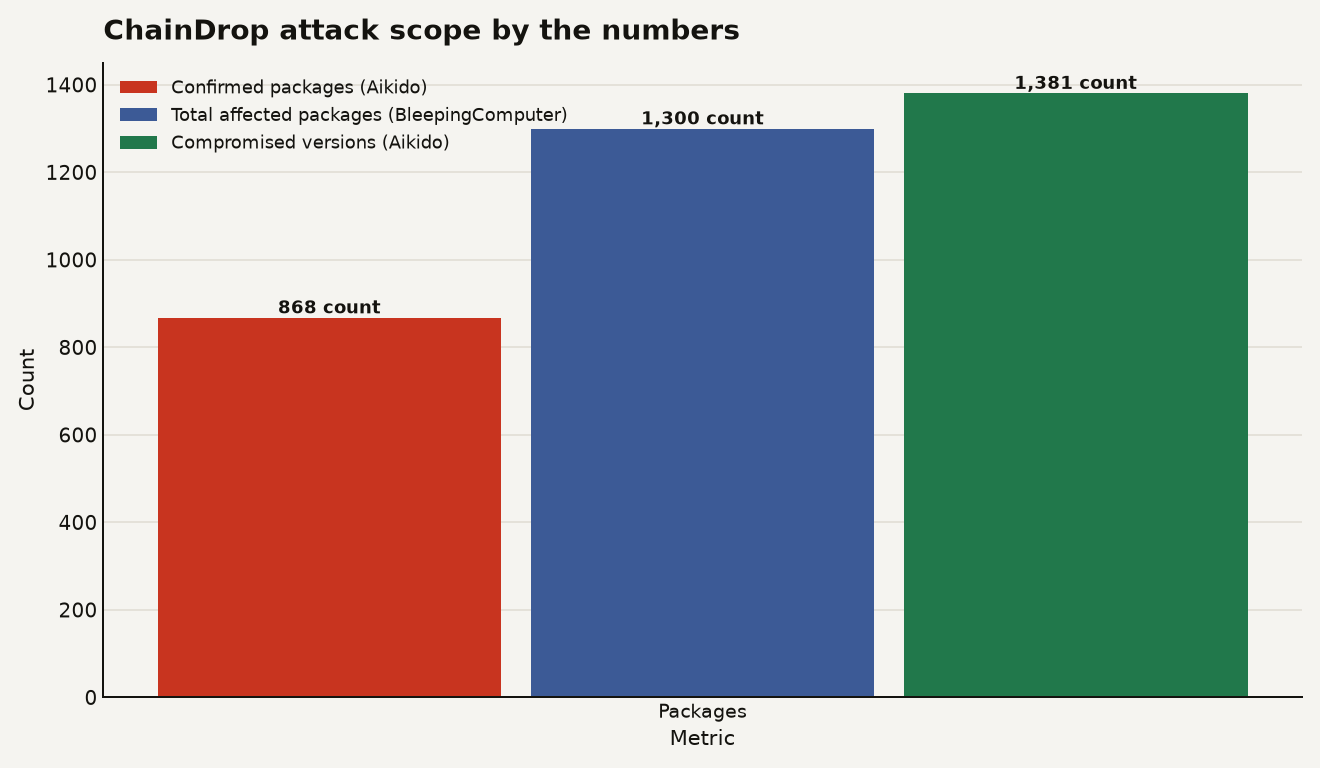
A self-propagating npm worm, ChainDrop hit 1,300 packages with 2 billion monthly downloads and stole cloud credentials from CI/CD runners.
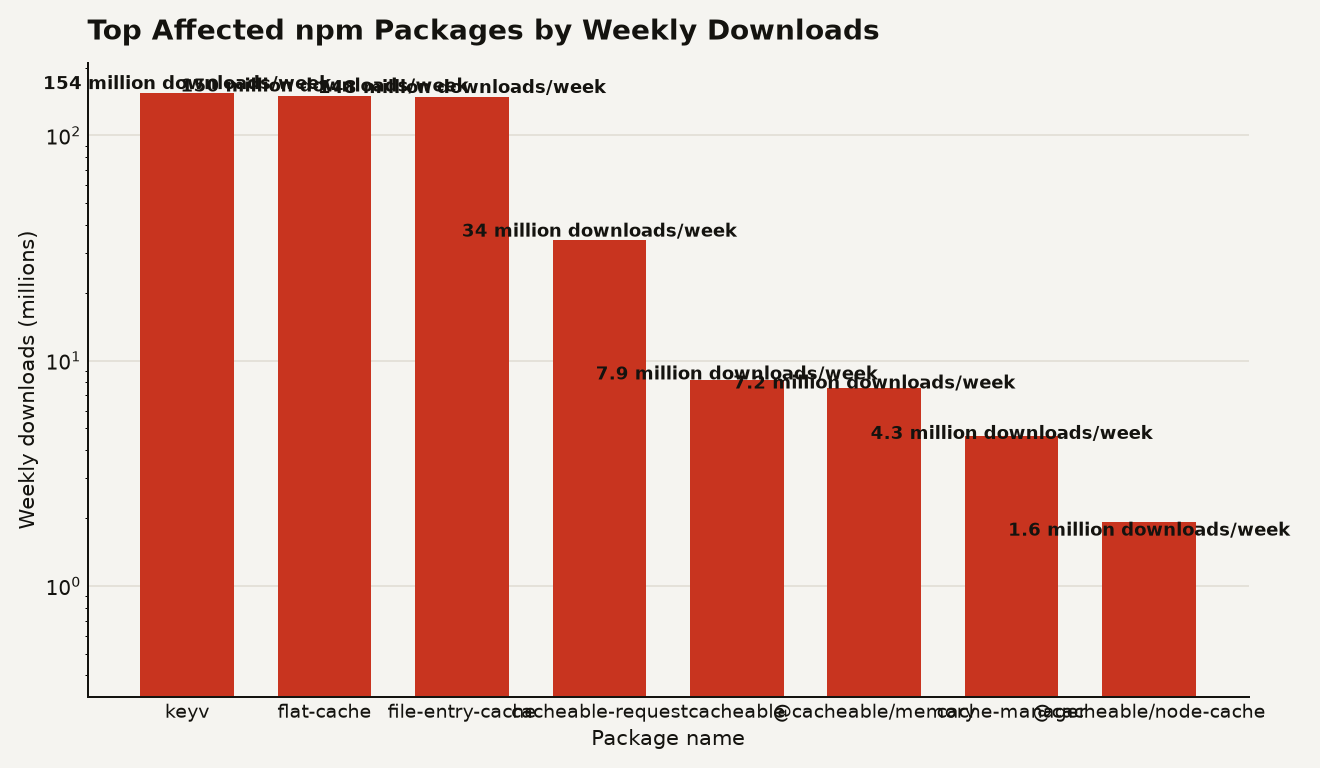
The Keyv npm supply chain attack spread a credential-stealing worm through 444 packages on August 4, 2026. The worm planted execution hooks in Claude Code and VS Code, harvesting CI secrets via Ethereum blockchain C2.
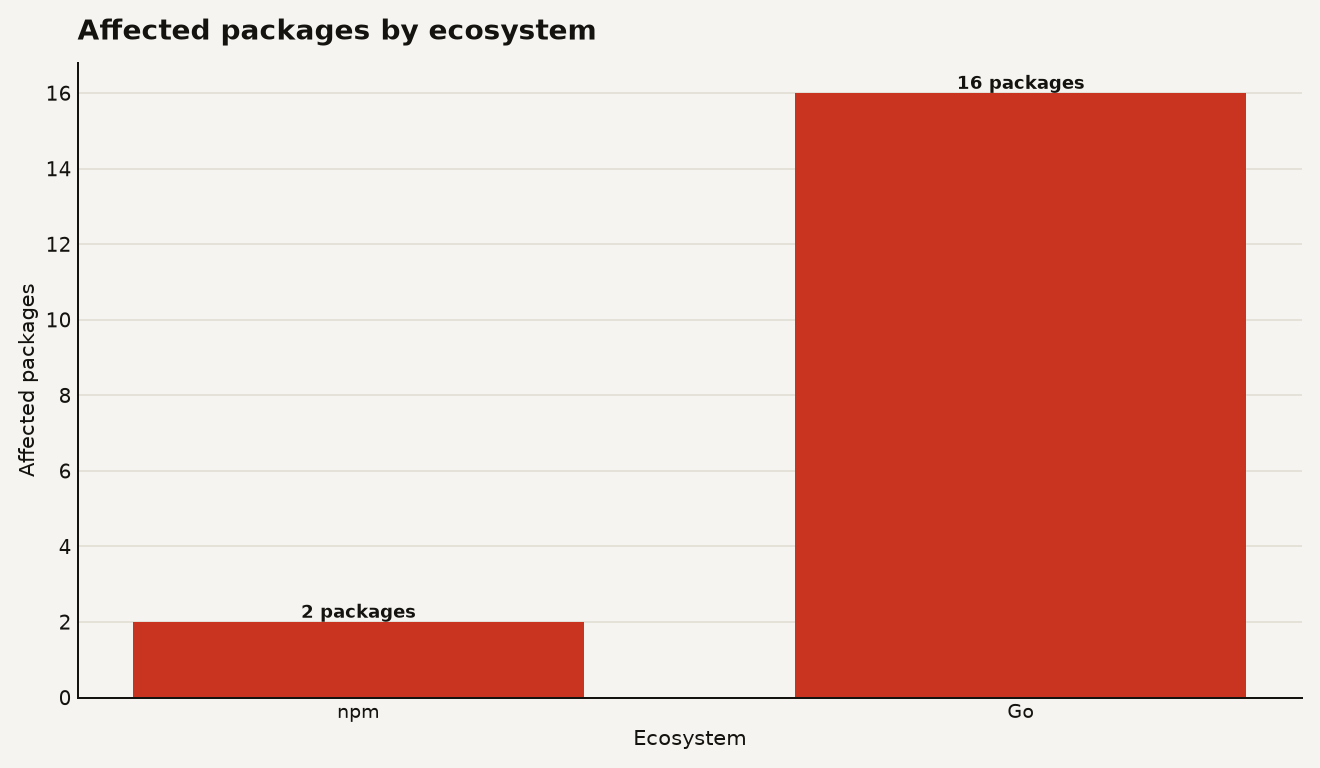
The VS Code Tasks supply chain attack runs outside npm lifecycle scripts, so the package hijack slips past install-time controls. Scan editor configs now.
Mastra npm supply chain attack exposed AI build pipelines through more than 140 packages, so treat installs as secret exposure events.
Hijacking Red Hat's GitHub Actions OIDC publishing, the Miasma npm worm shipped 96 backdoored versions whose preinstall hook steals and spreads secrets.
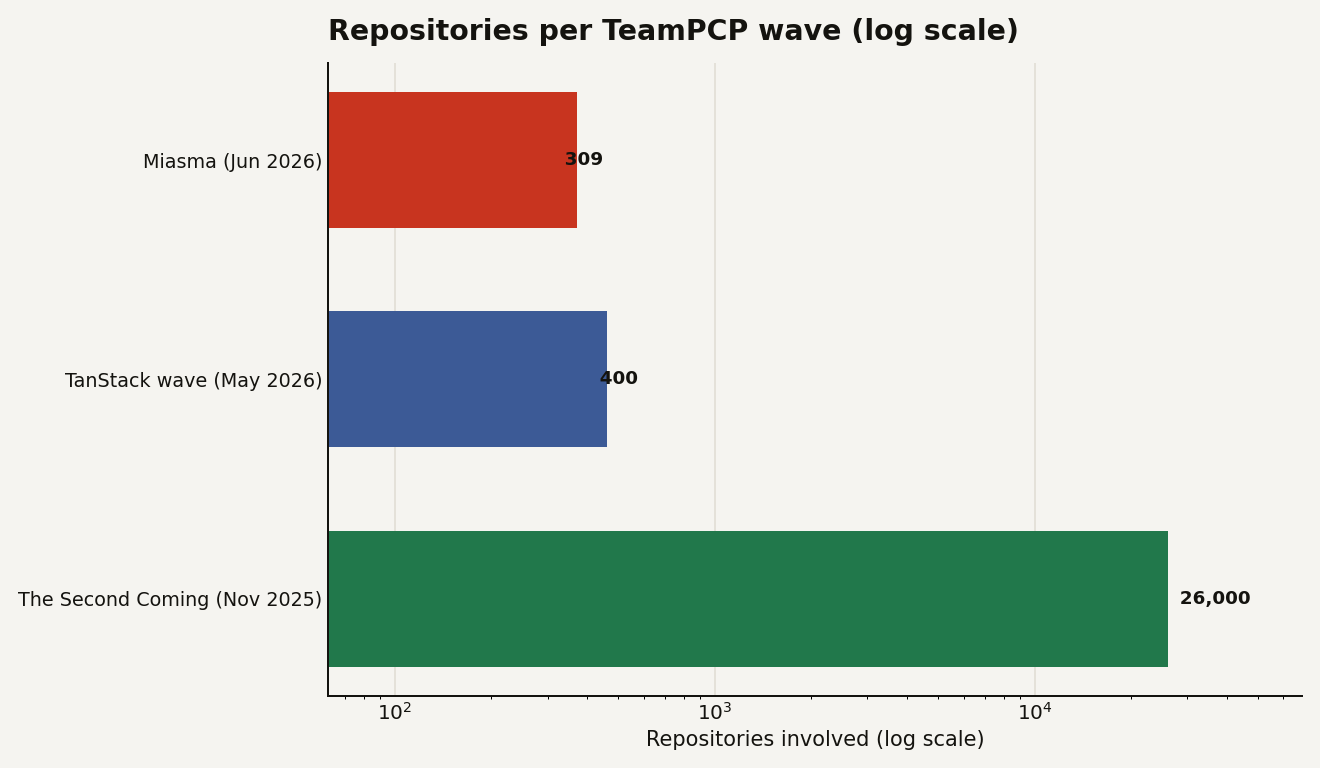
The crew behind the Shai-Hulud npm worm, TeamPCP open-sourced it in May 2026, then poisoned Red Hat's packages and blurred who to blame.