PHP 8.5.12 fixes two critical pre-auth RCEs: update now
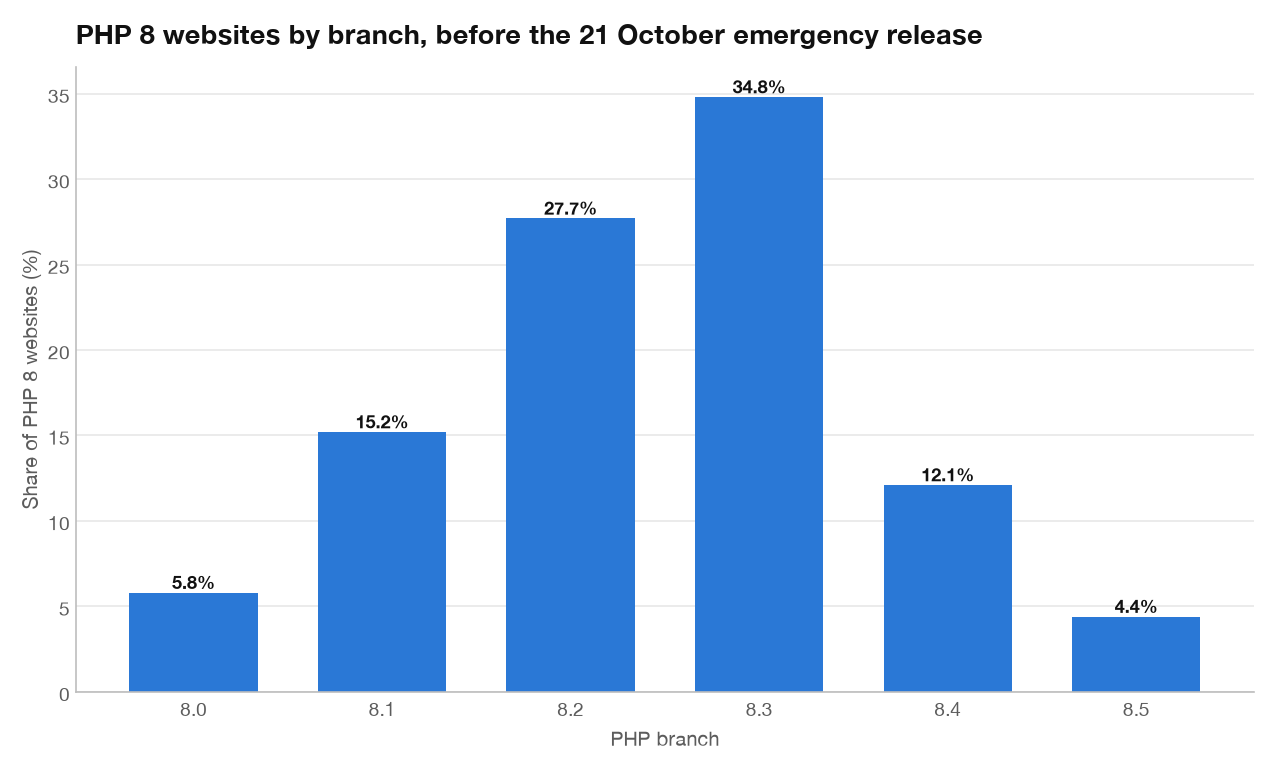
Two PHP flaws rated 9.2, CVE-2026-109618 and CVE-2026-109619, allow unauthenticated RCE before your code runs. Fixed in PHP 8.5.12 and 8.4.27.
15 stories tagged threat-intel.
Two PHP flaws rated 9.2, CVE-2026-109618 and CVE-2026-109619, allow unauthenticated RCE before your code runs. Fixed in PHP 8.5.12 and 8.4.27.
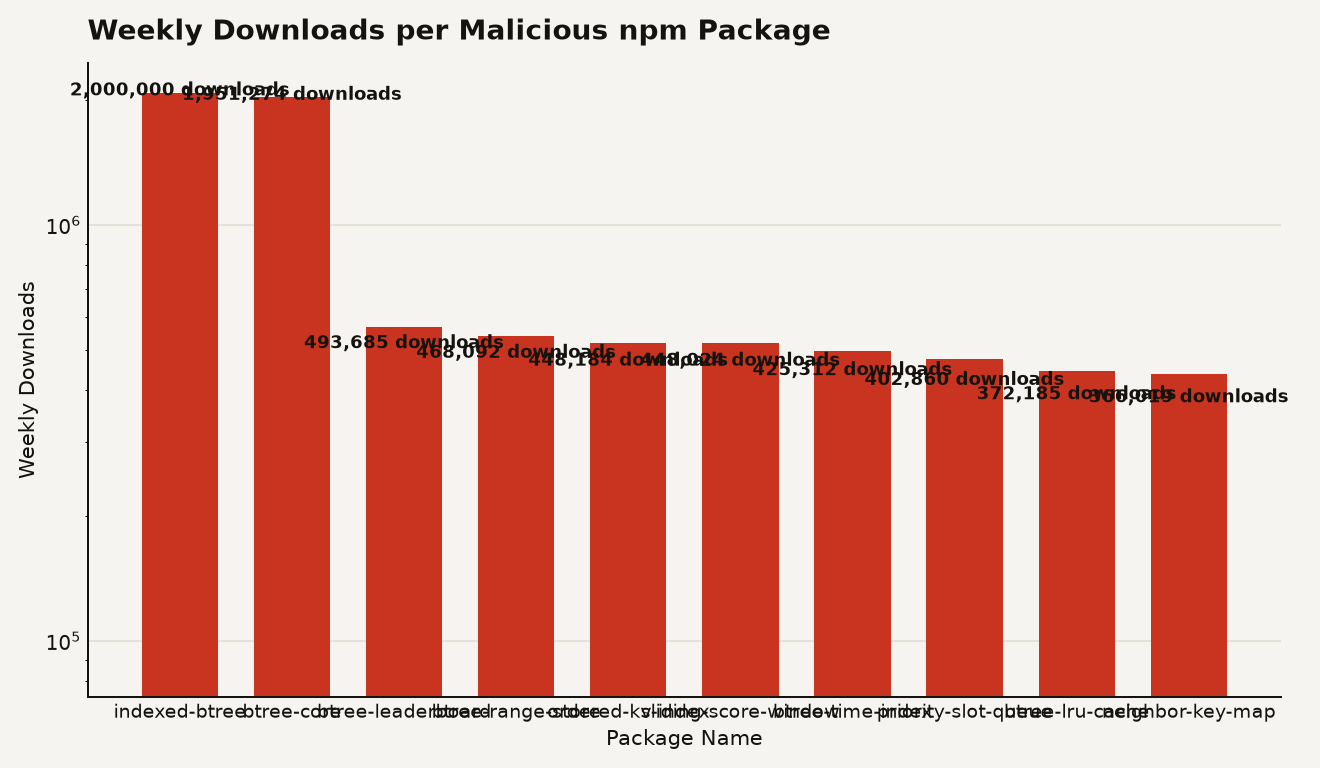
An npm supply chain attack hides malware in runtime methods, bypassing npm v12 install-script blocks. Ten packages and 7 million downloads are affected.
North Korea's WaterPlum hacking group compromised at least 30,000 devices in over 100 countries via fake job interviews, stealing $10.7 million in cryptocurrency. The campaign weaponizes npm packages and VS Code projects against software developers.
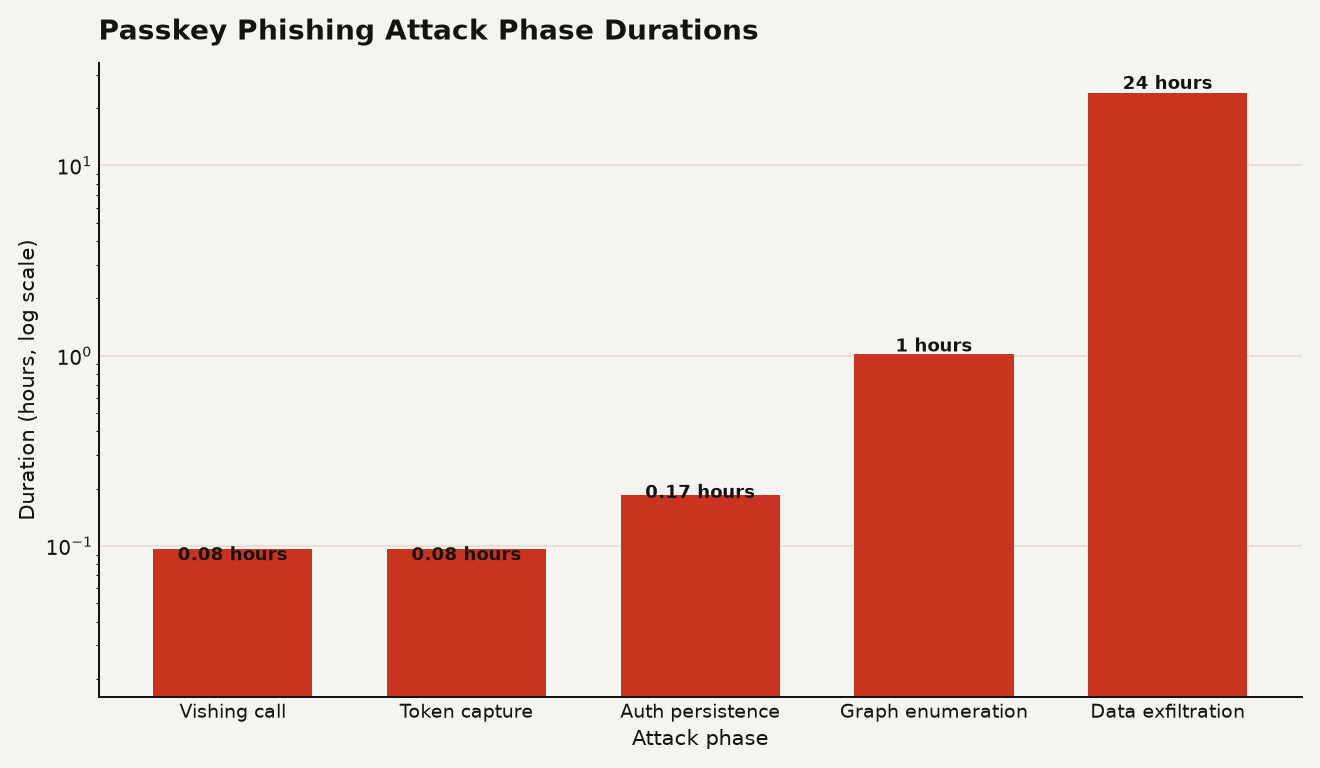
Vishing calls themed around passkeys are hijacking Microsoft 365 accounts; attackers steal session tokens and exfiltrate data over days.
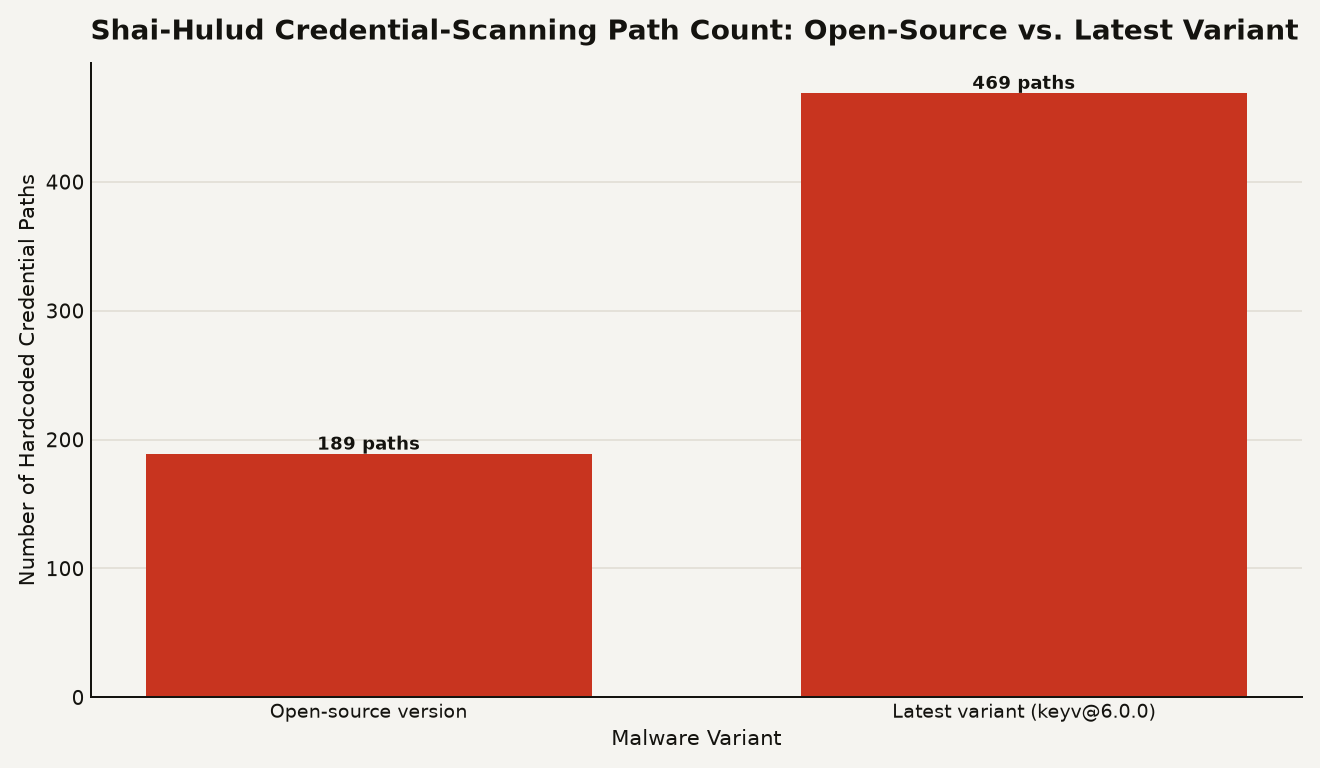
The Shai-Hulud npm infostealer worm expanded from 189 to 469 credential-scanning paths across dev machines, CI/CD, cloud, and AI tool configs after the [email protected] compromise. Rotate everything.
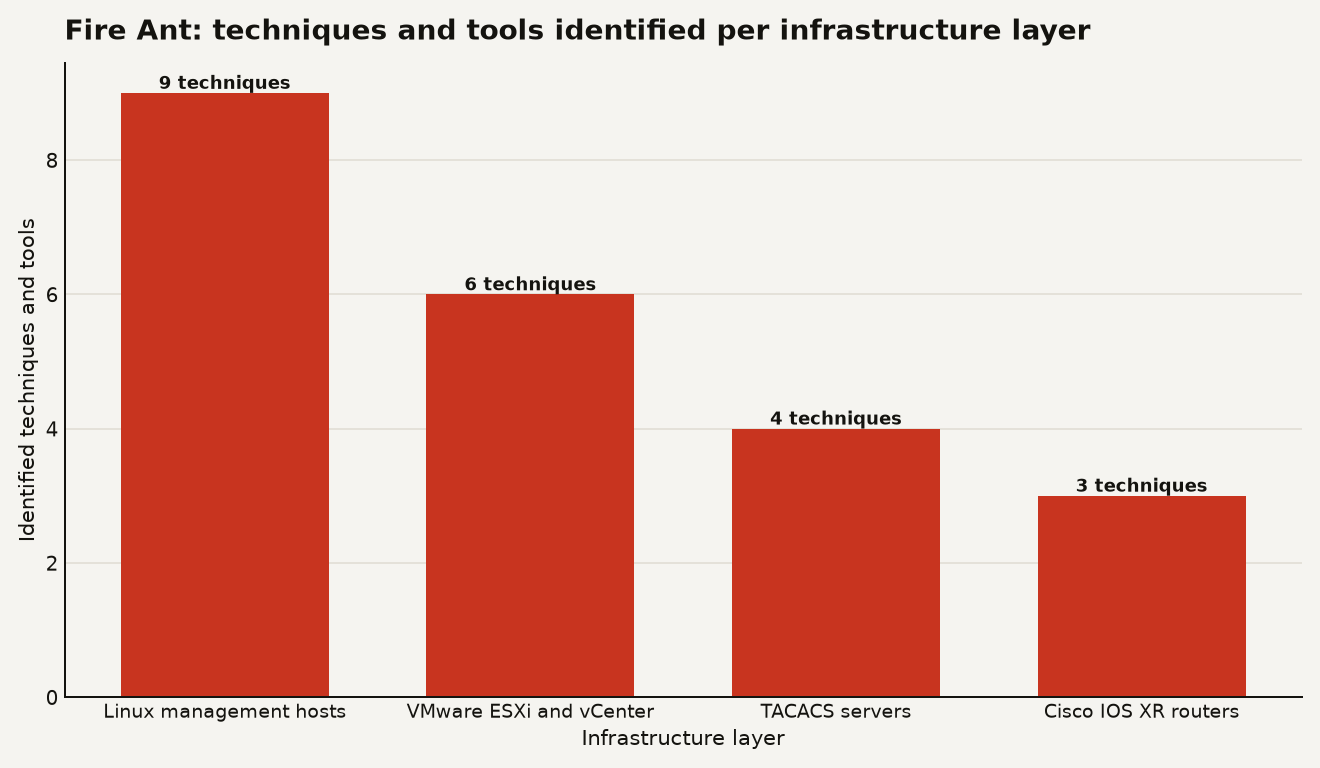
Fire Ant, a China-nexus espionage group, expanded from VMware hypervisors to Cisco IOS XR routers and TACACS servers, hijacking the network trust layer to steal credentials and blind security logging across connected environments.
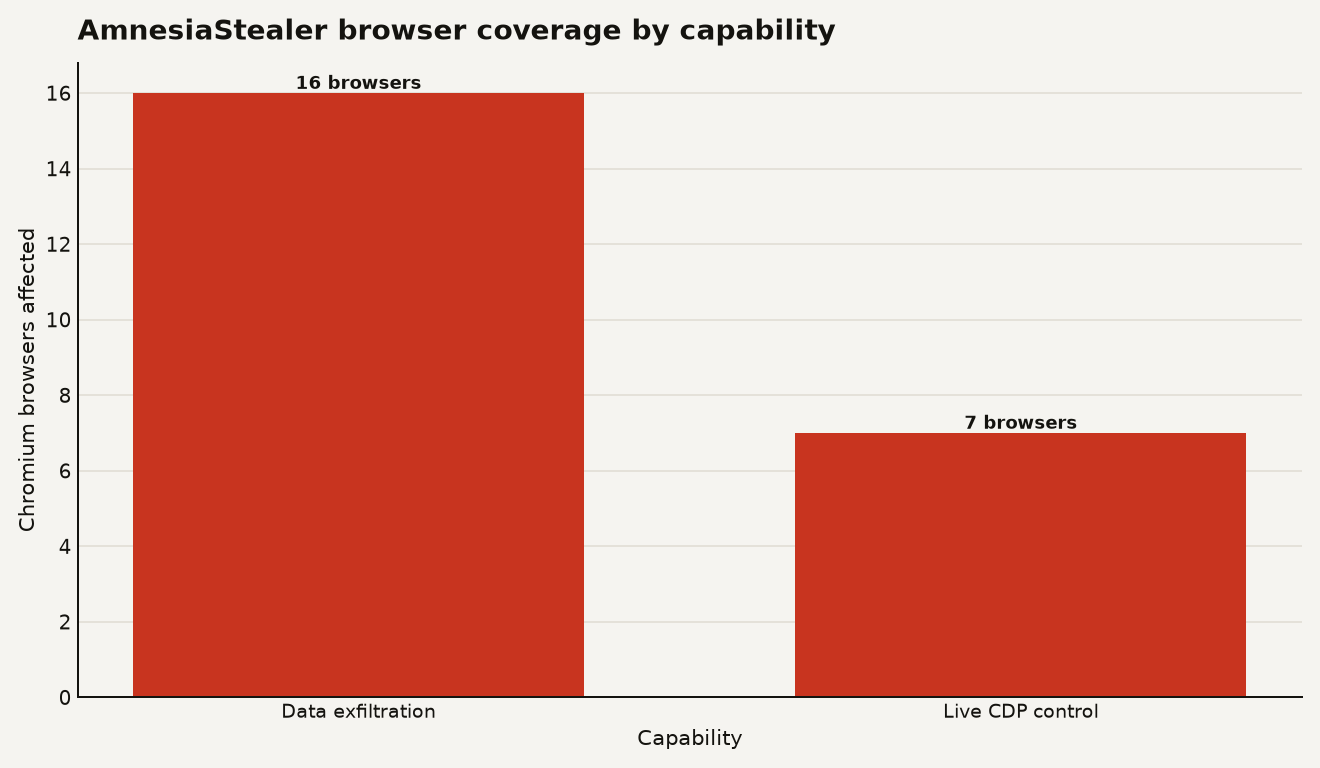
A new macOS infostealer, AmnesiaStealer clones Chromium profiles and gives attackers live control of logged-in browser sessions over CDP.
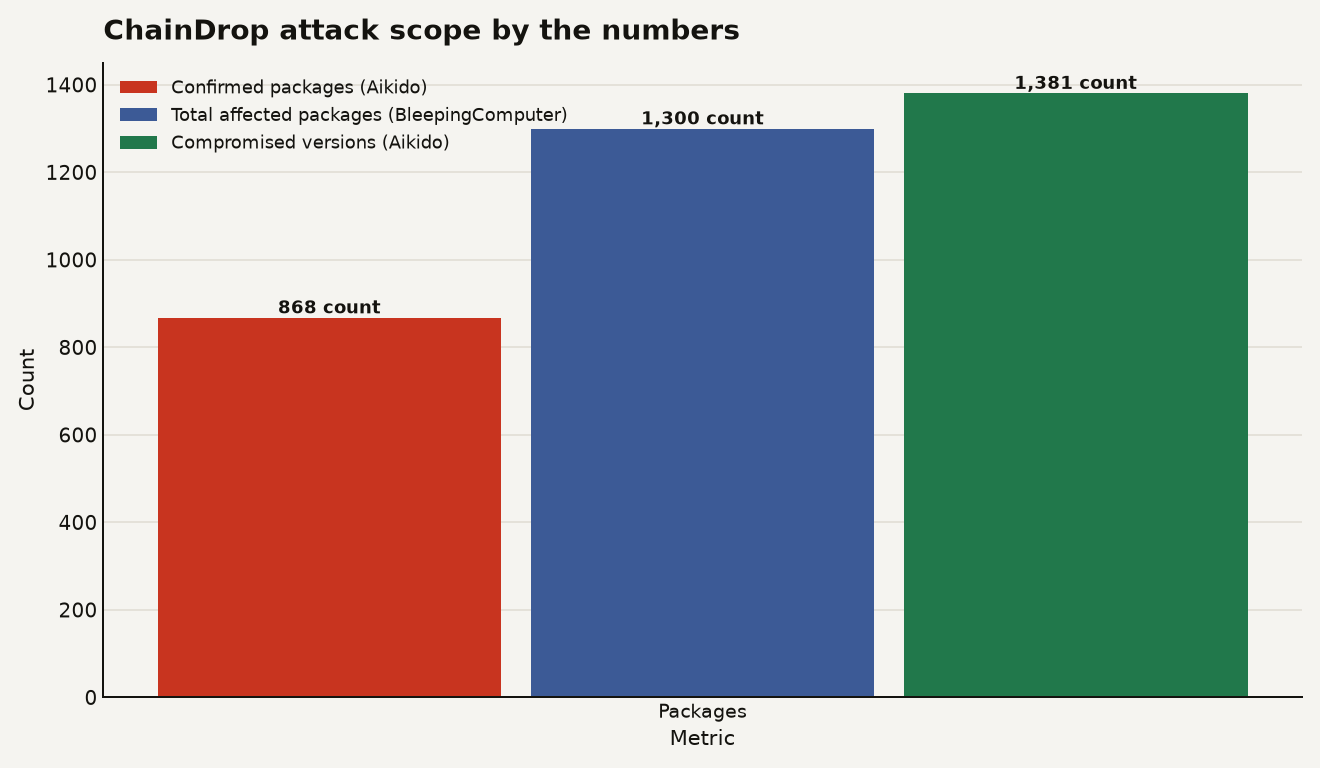
A self-propagating npm worm, ChainDrop hit 1,300 packages with 2 billion monthly downloads and stole cloud credentials from CI/CD runners.
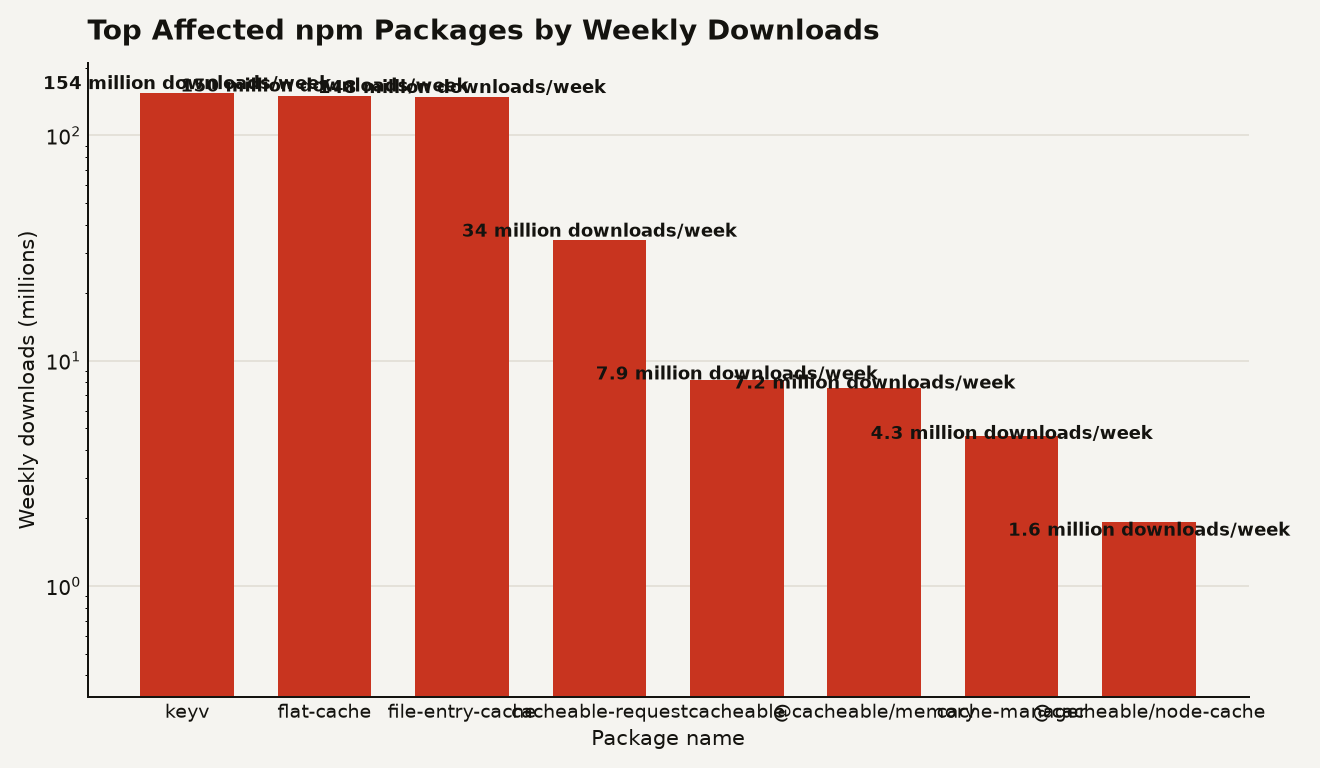
The Keyv npm supply chain attack spread a credential-stealing worm through 444 packages on August 4, 2026. The worm planted execution hooks in Claude Code and VS Code, harvesting CI secrets via Ethereum blockchain C2.
PLC attacks on water utilities by Iranian APTs triggered a CISA alert after attackers locked operators out and caused boil water notices across the US.
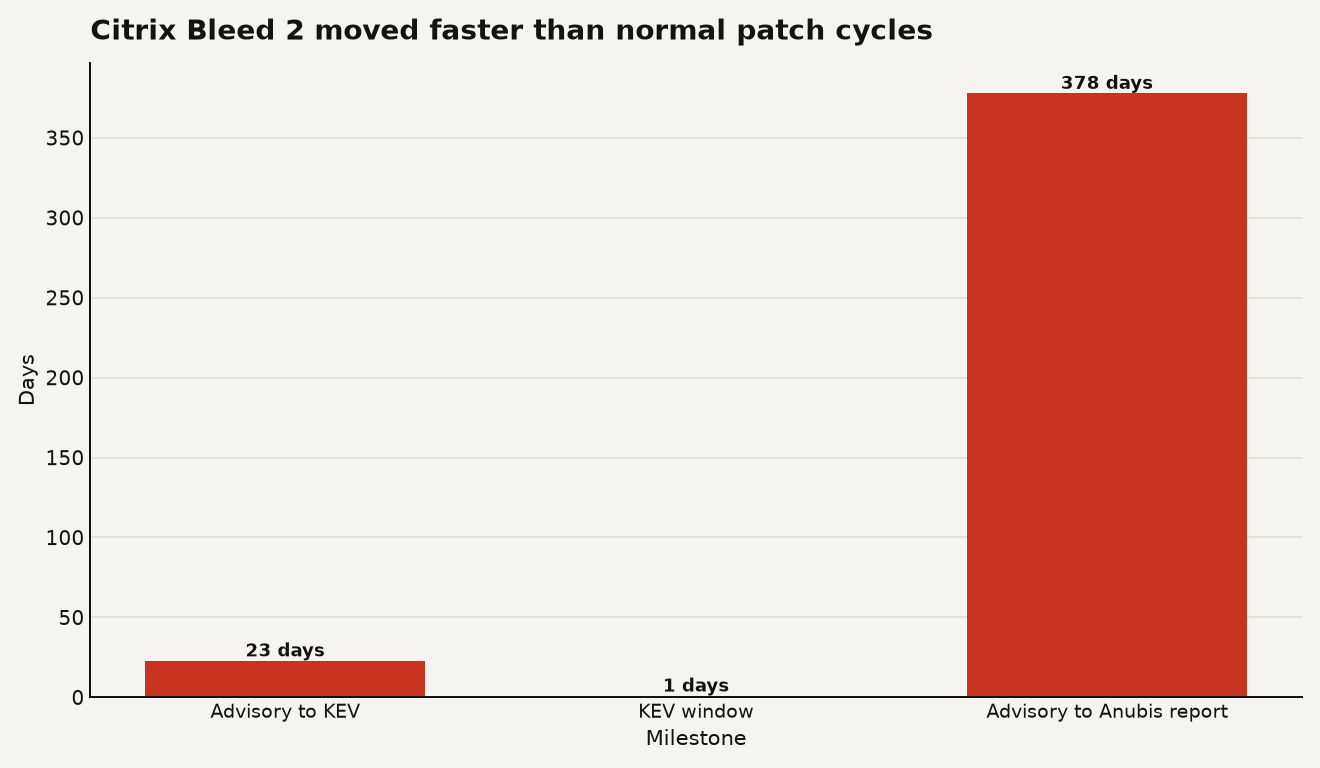
Anubis ransomware now uses Citrix Bleed 2 as an access path. Patch NetScaler, kill sessions, and hunt RMM and credential abuse.
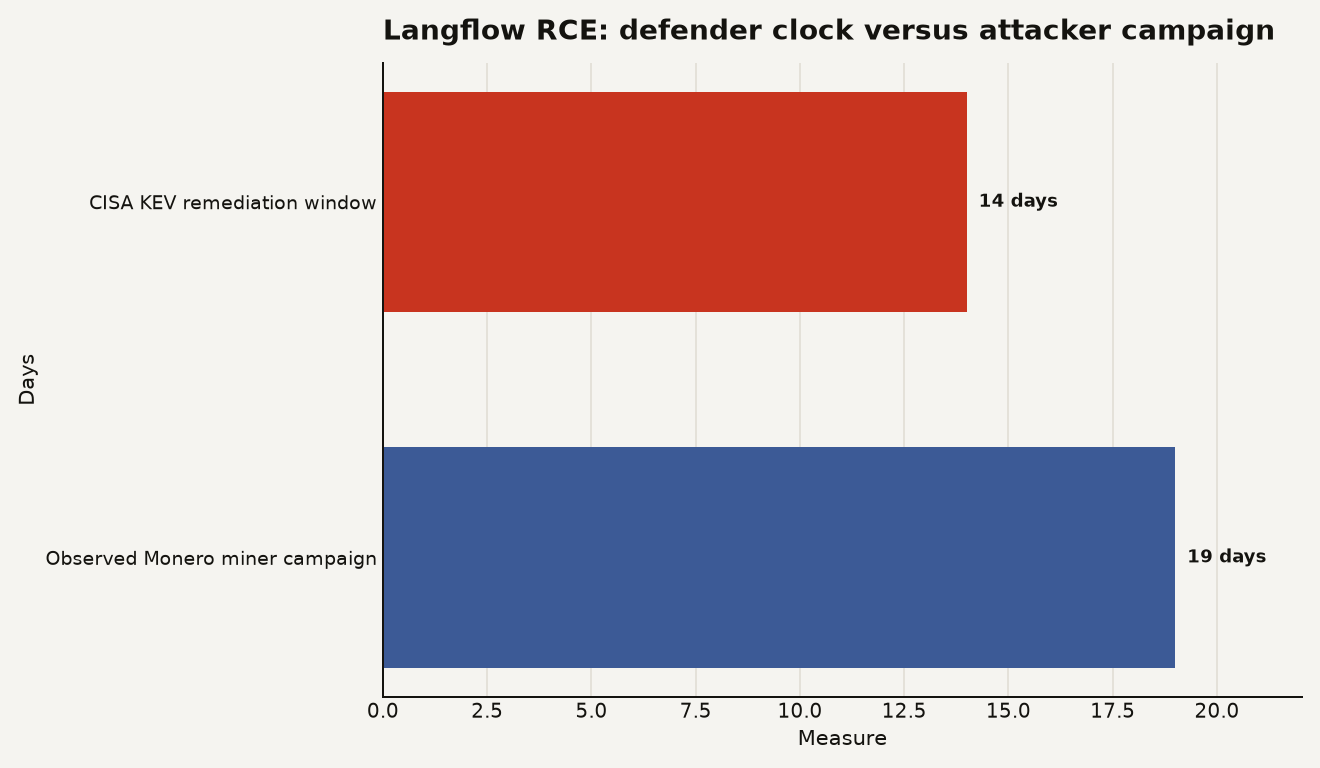
Attackers use a Langflow RCE to mine Monero on exposed AI app endpoints. Patch, isolate, and treat public workflows as attack surface.
The VS Code Tasks supply chain attack runs outside npm lifecycle scripts, so the package hijack slips past install-time controls. Scan editor configs now.
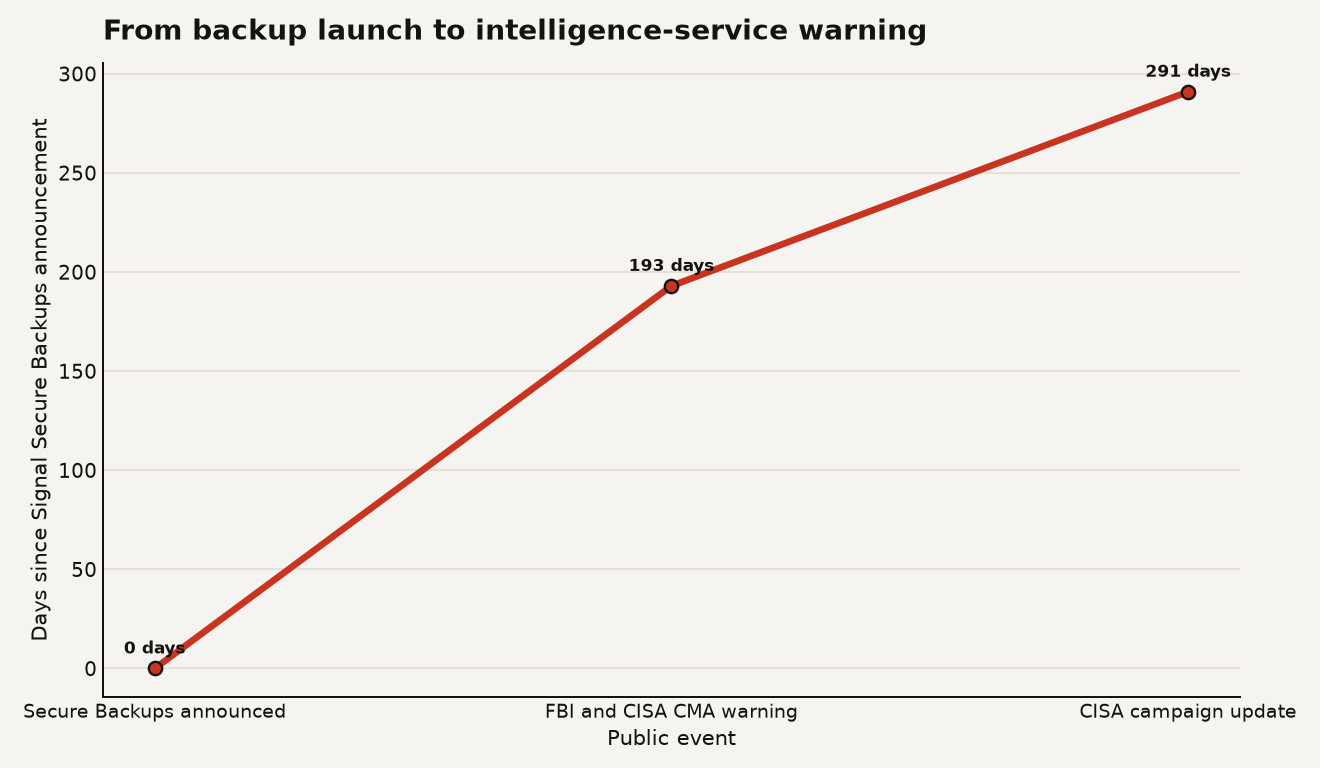
Signal backup recovery keys can expose historical chats after one phishing win. Treat messenger backups like identity infrastructure now.
Mastra npm supply chain attack exposed AI build pipelines through more than 140 packages, so treat installs as secret exposure events.