Cyber security
Check Point SmartConsole auth bypass gives attackers full admin
Rated CVSS 9.3 and listed in CISA KEV, the Check Point SmartConsole auth bypass CVE-2026-16232 is actively exploited. Patch management servers now.
3 stories tagged patching.
Rated CVSS 9.3 and listed in CISA KEV, the Check Point SmartConsole auth bypass CVE-2026-16232 is actively exploited. Patch management servers now.
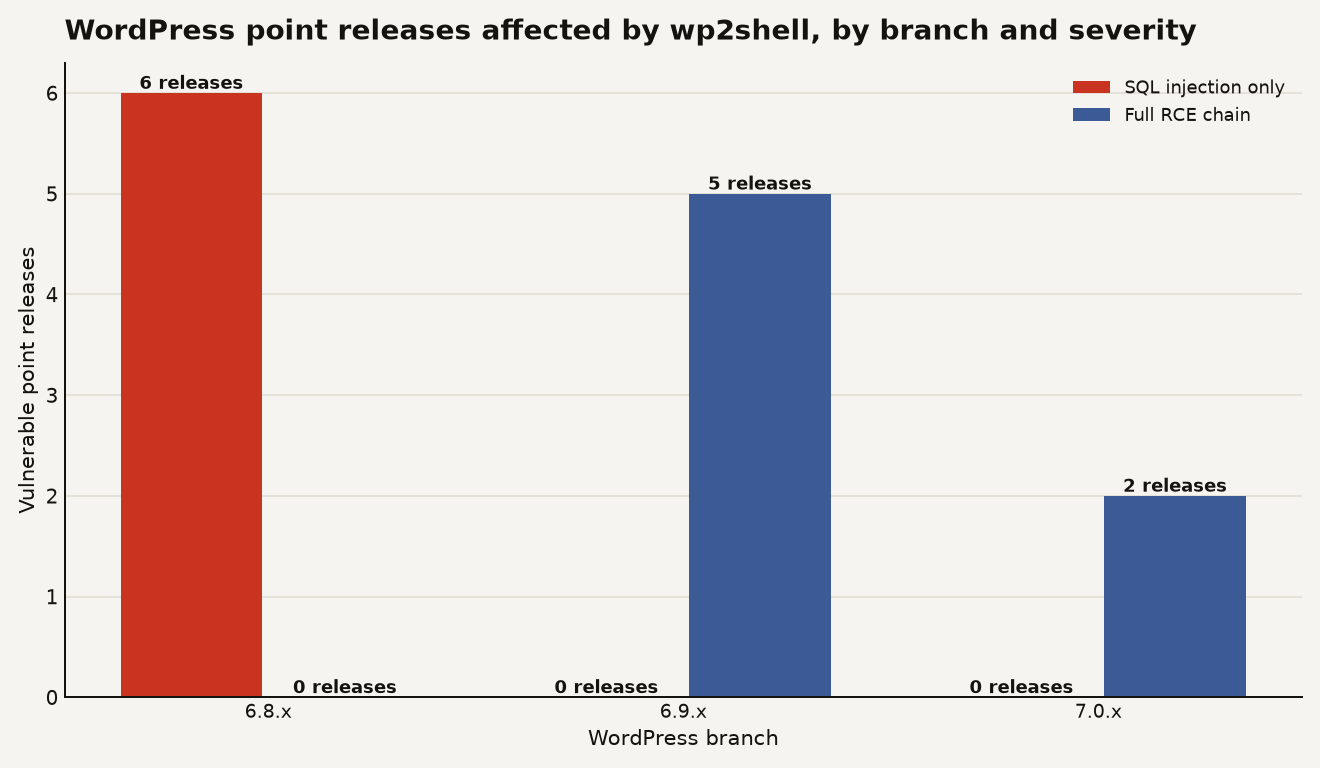
Two WordPress Core CVEs form wp2shell, a pre-auth RCE chain that lets anonymous attackers run code on 6.9 and 7.0 sites with no plugins.
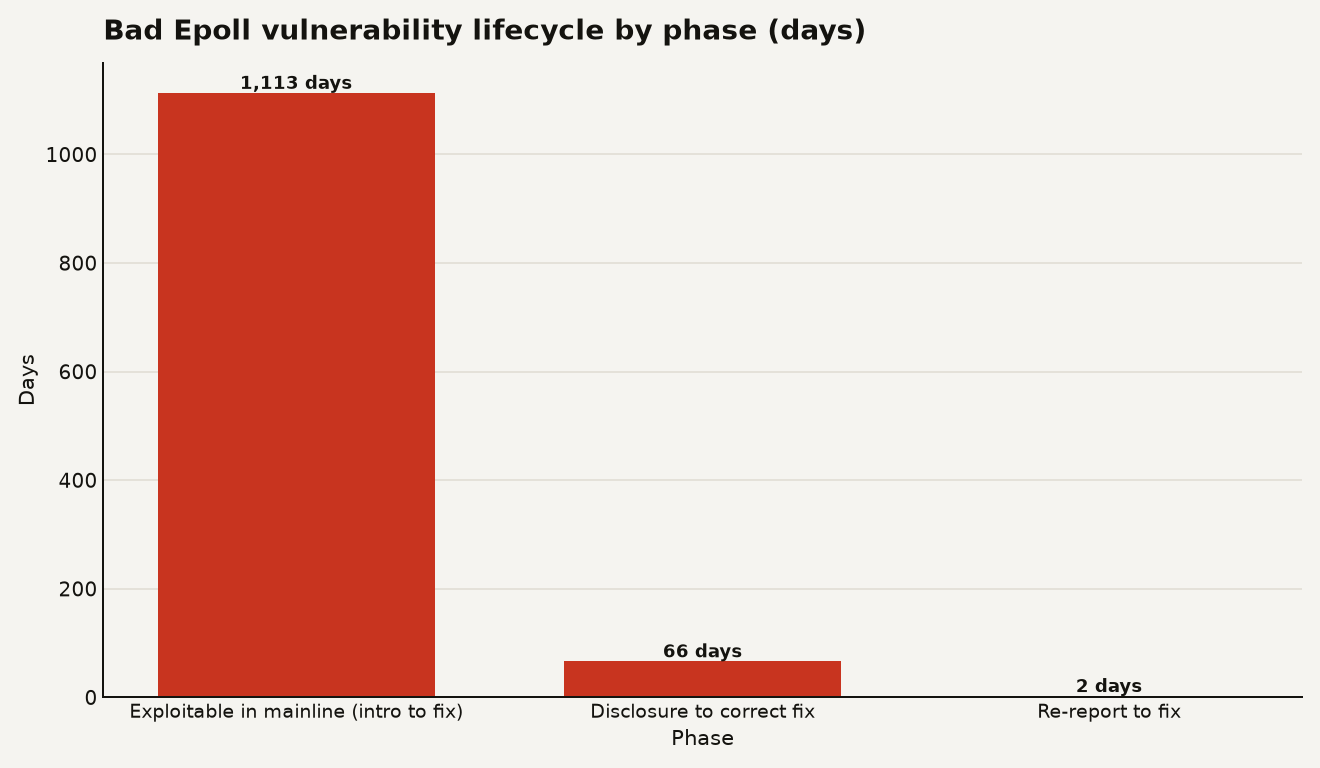
Unprivileged users get root on Linux v6.4+ and Android through Bad Epoll (CVE-2026-46242). No workaround exists; apply patch a6dc643c6931 now.