Cyber security
SharePoint CVE-2026-55040 auth bypass exploited after PoC
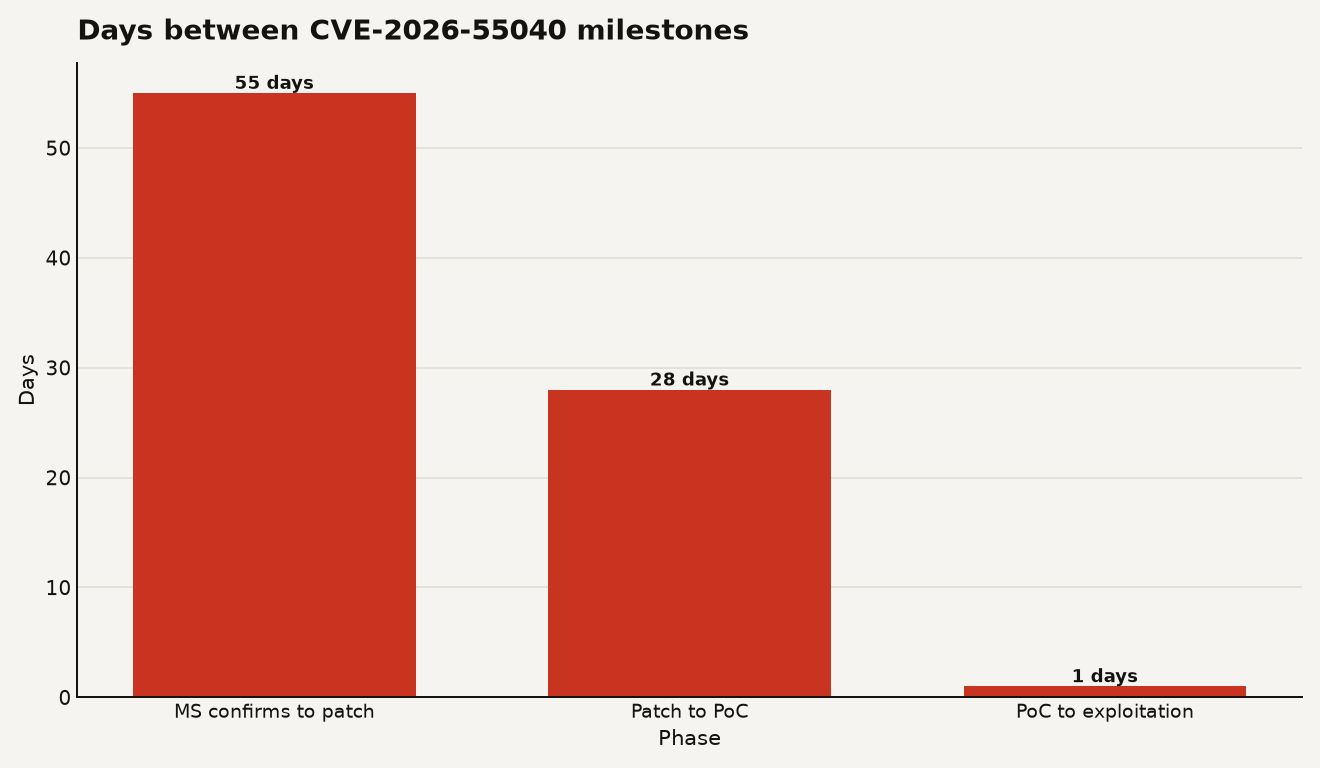
Attackers began exploiting the SharePoint auth bypass CVE-2026-55040, rated CVSS 9.1 and patched in July, after Rapid7 released a PoC on August 11.
2 stories tagged sharepoint.
Attackers began exploiting the SharePoint auth bypass CVE-2026-55040, rated CVSS 9.1 and patched in July, after Rapid7 released a PoC on August 11.
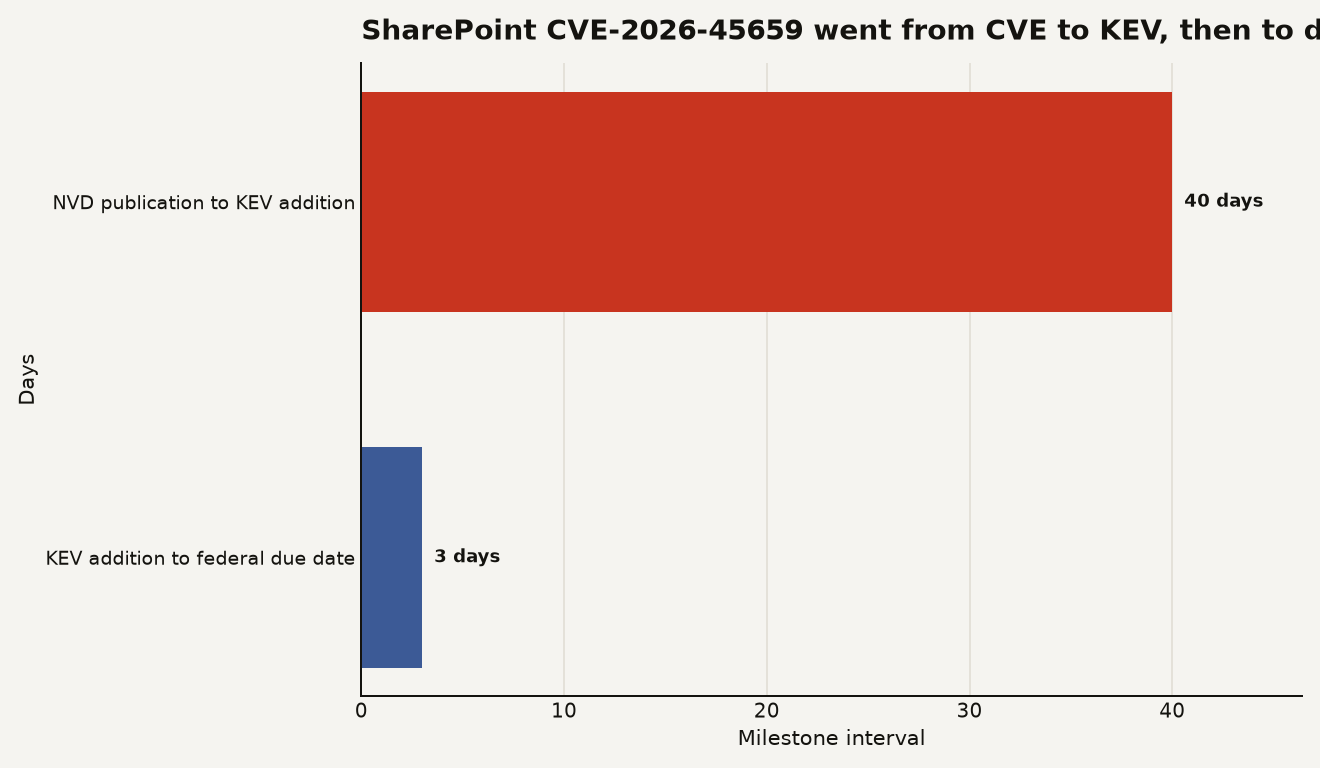
Listed in CISA KEV, SharePoint CVE-2026-45659 is an actively exploited RCE risk. Patch exposed servers and check for compromise now.