PHP 8.5.12 fixes two critical pre-auth RCEs: update now
Two PHP flaws rated 9.2, CVE-2026-109618 and CVE-2026-109619, allow unauthenticated RCE before your code runs. Fixed in PHP 8.5.12 and 8.4.27.
The Security Desk tracks the critical vulnerabilities and incidents that hit data and AI teams. Each report says who is affected, whether it is exploited in the wild, and exactly what to patch or switch off, in that order.
The Data Today Security Desk is a research workflow that monitors primary sources and drafts analysis. Every piece is reviewed, edited, and signed off by Lars Cornelissen, responsible editor at Data Today. Corrections go to [email protected].
Sources this desk works from:
Responsible editor: Lars Cornelissen, responsible editor.
Contact: [email protected].
Two PHP flaws rated 9.2, CVE-2026-109618 and CVE-2026-109619, allow unauthenticated RCE before your code runs. Fixed in PHP 8.5.12 and 8.4.27.
Data Today Security Desk ·
CVE-2026-76504 is a CVSS 9.8 authentication bypass in Cisco Catalyst SD-WAN Manager, exploited in the wild since September 2026. CISA gave federal agencies until October 3 to patch. Here is what to check and how to fix it.
Data Today Security Desk ·
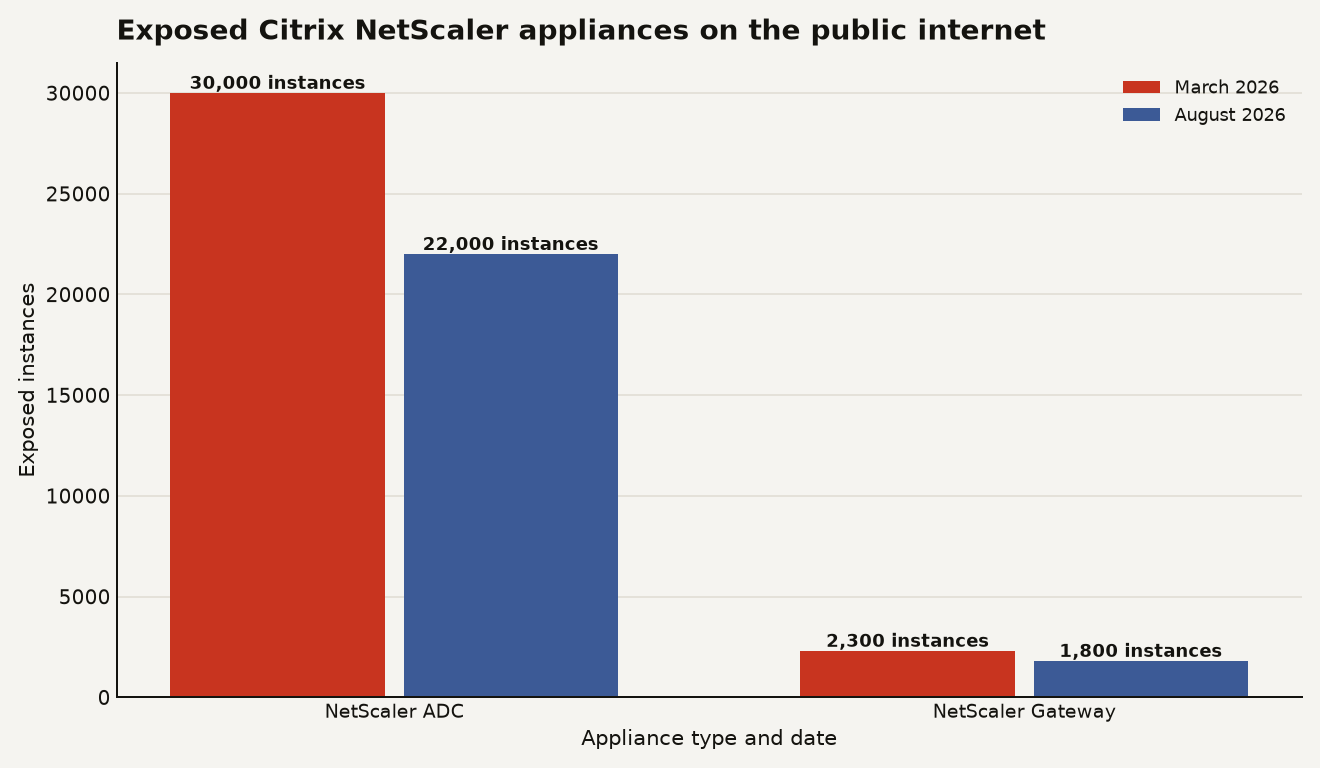
With no fix available for two exploited Citrix NetScaler RCE zero-days, operators must isolate or shut down appliances before Monday.
Data Today Security Desk ·
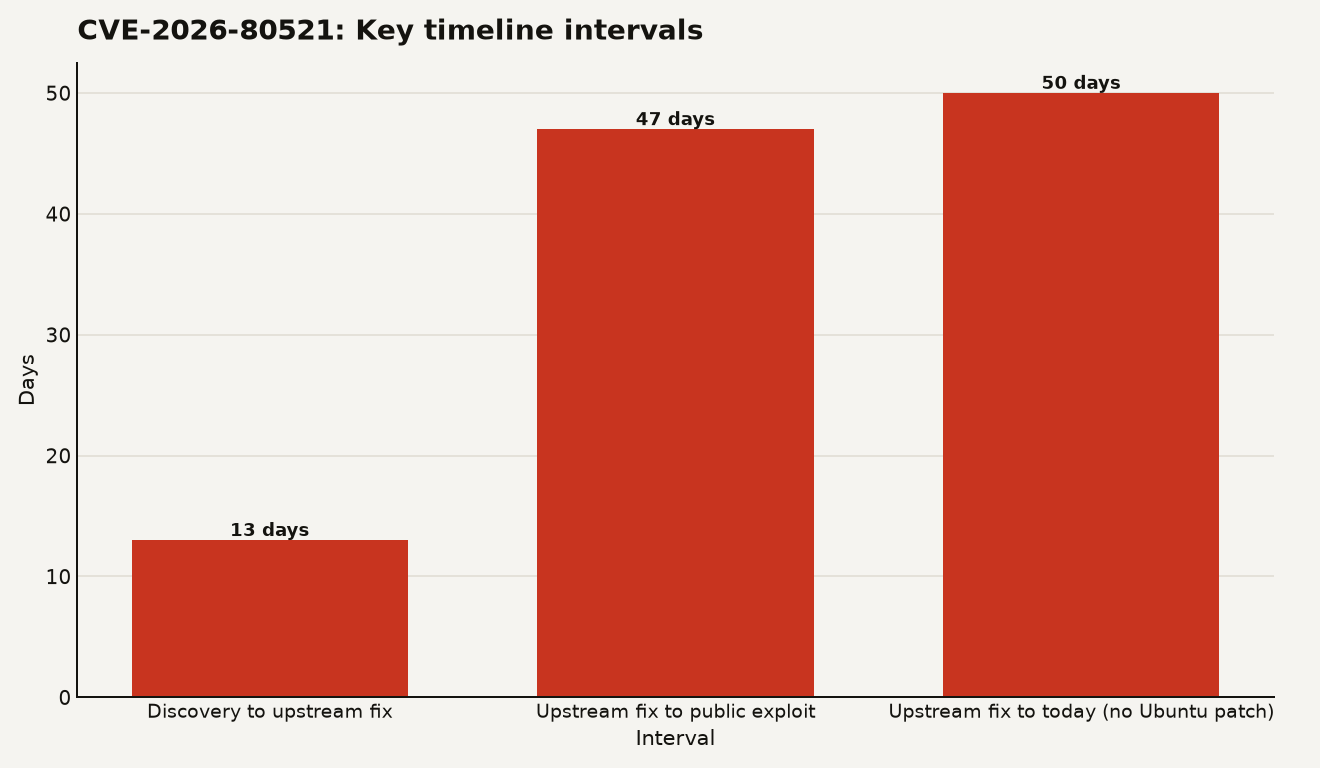
CVE-2026-80521 enables a container escape to host root via a Linux kernel use-after-free. Ubuntu has no LTS patch 50 days after the upstream fix.
Data Today Security Desk ·
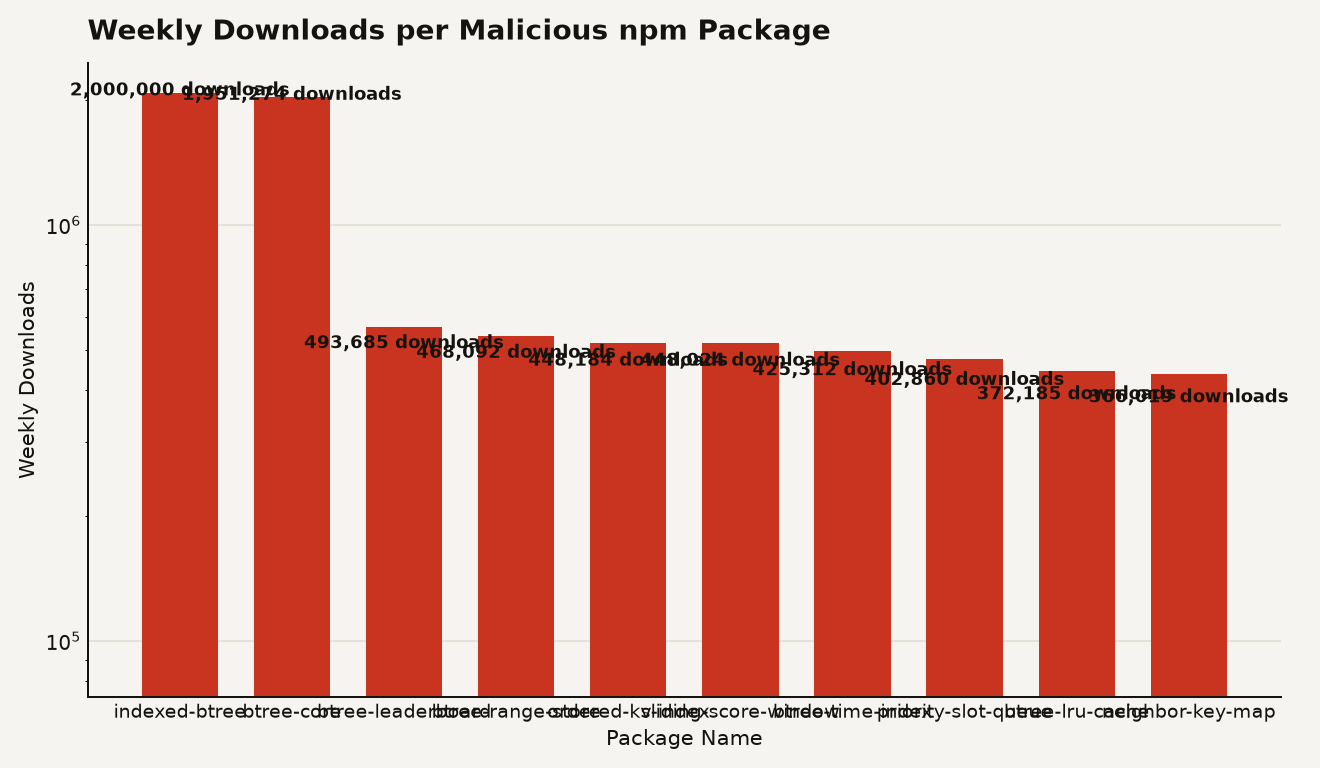
An npm supply chain attack hides malware in runtime methods, bypassing npm v12 install-script blocks. Ten packages and 7 million downloads are affected.
Data Today Security Desk ·
North Korea's WaterPlum hacking group compromised at least 30,000 devices in over 100 countries via fake job interviews, stealing $10.7 million in cryptocurrency. The campaign weaponizes npm packages and VS Code projects against software developers.
Data Today Security Desk ·
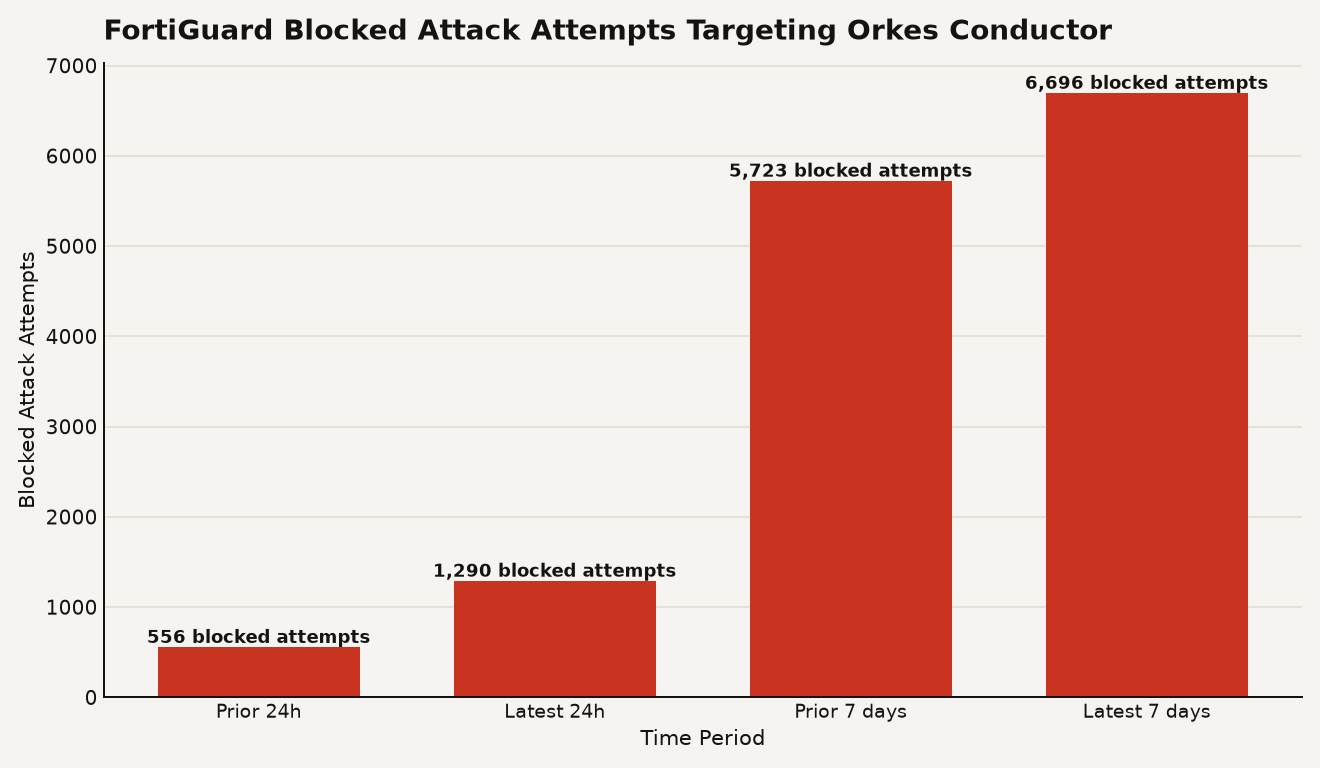
Exploited since August 2026, Orkes Conductor CVE-2026-58138 is a CVSS 9.8 unauthenticated RCE in GraalVM script evaluators. Upgrade to 3.30.2.
Data Today Security Desk ·
An AI coding assistant hijack at a SaaS provider let attackers spread the Shai-Hulud worm across 100 repositories, stealing secrets and proprietary source code.
Data Today Security Desk ·
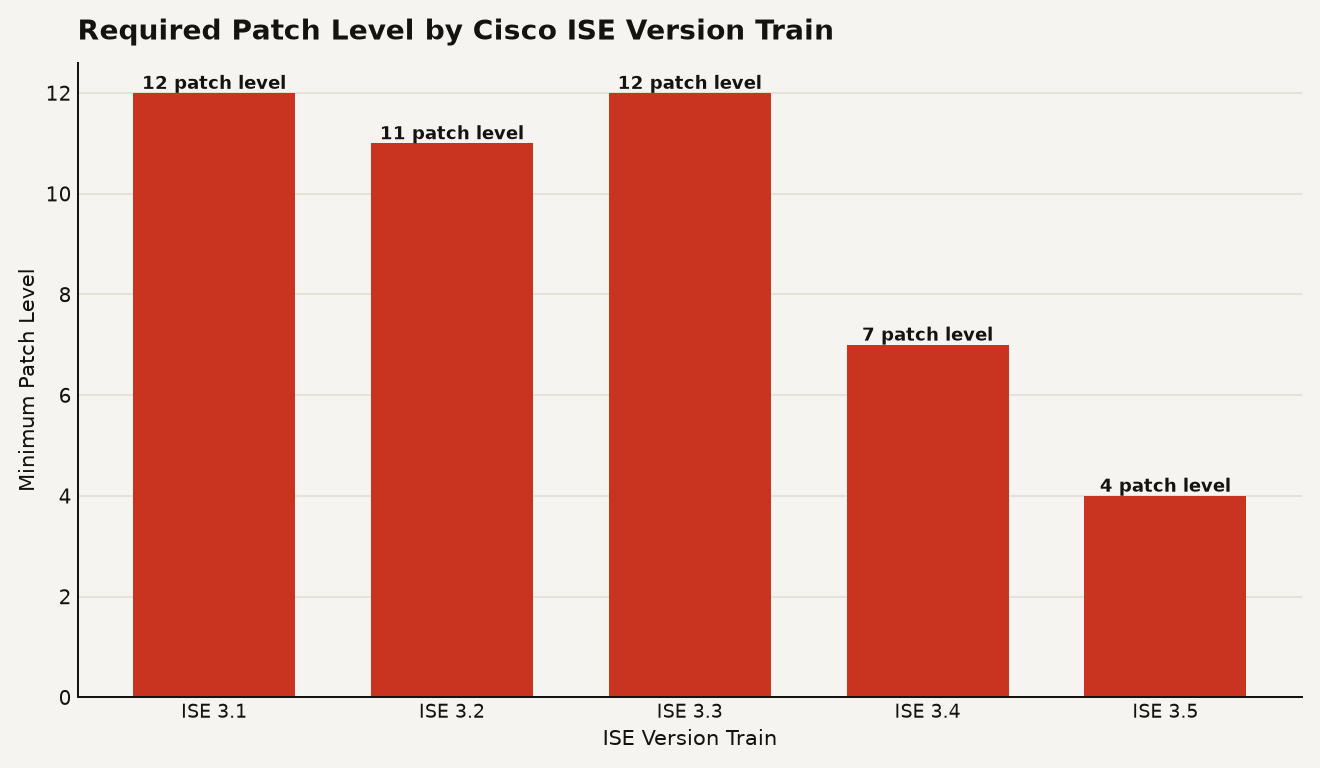
Attackers are exploiting CVE-2026-76460, a CVSS 10.0 auth bypass in Cisco ISE and ISE-PIC. CISA gave federal agencies three days to patch.
Data Today Security Desk ·
CISA confirmed active exploitation of CVE-2026-76461, a root-level SQL injection in Cisco Secure Email Gateway, and set a 3-day patch deadline.
Data Today Security Desk ·
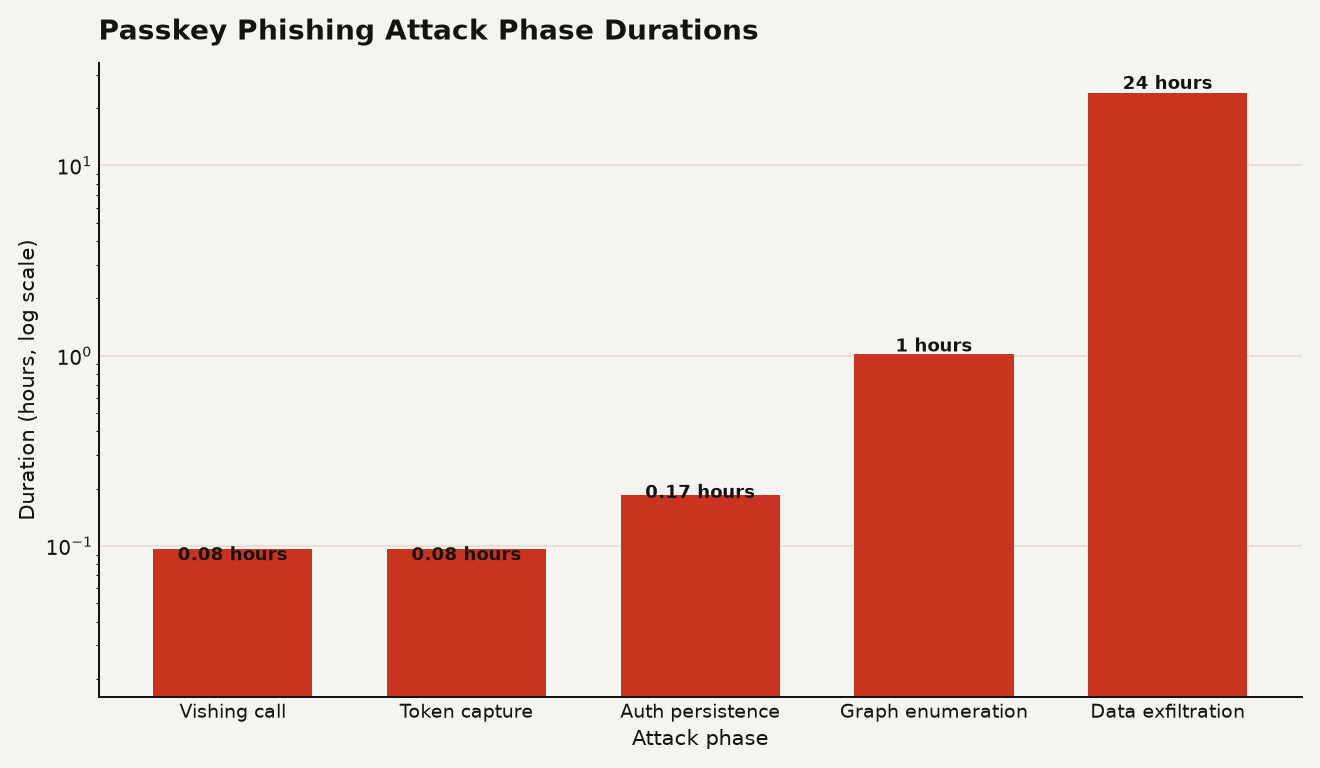
Vishing calls themed around passkeys are hijacking Microsoft 365 accounts; attackers steal session tokens and exfiltrate data over days.
Data Today Security Desk ·
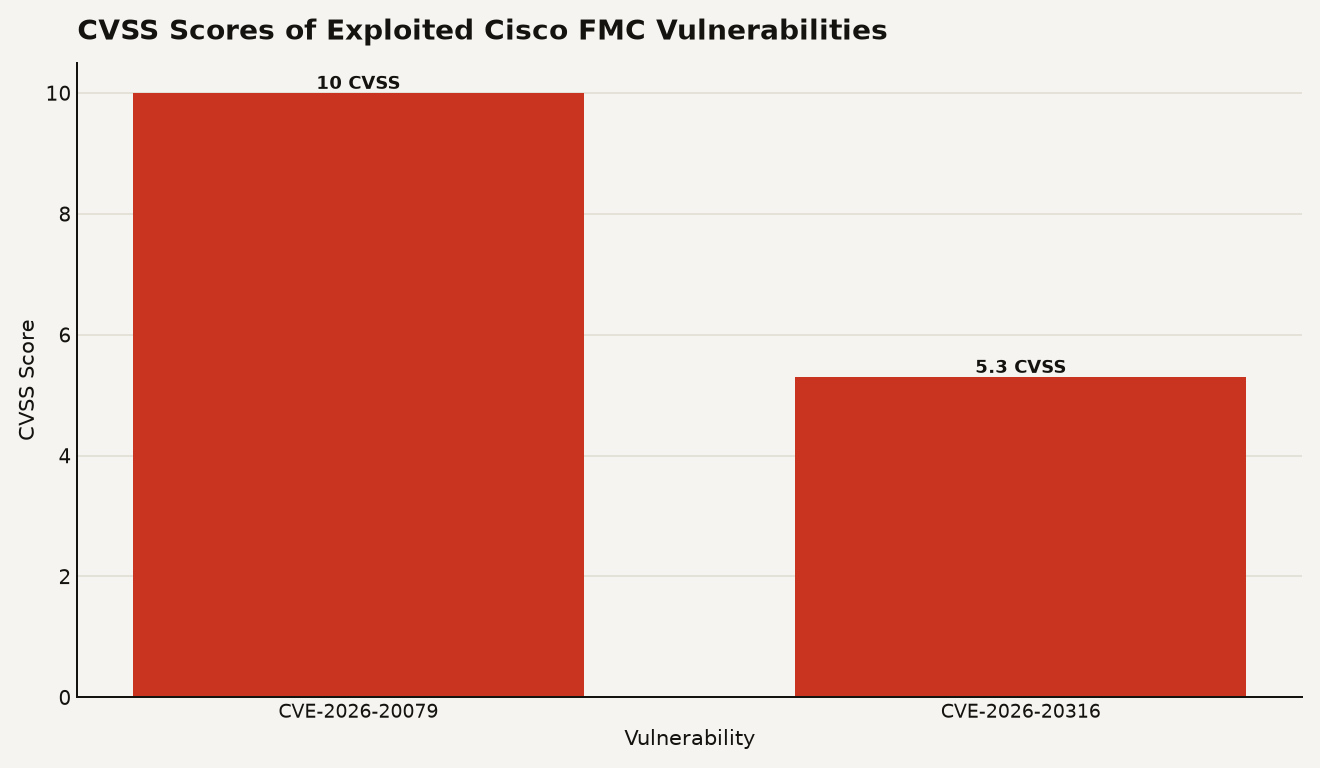
Cisco FMC CVE-2026-20079 lets unauthenticated attackers gain root on firewall managers. Three threat clusters are exploiting it, including Qilin ransomware and suspected Sandworm activity.
Data Today Security Desk ·
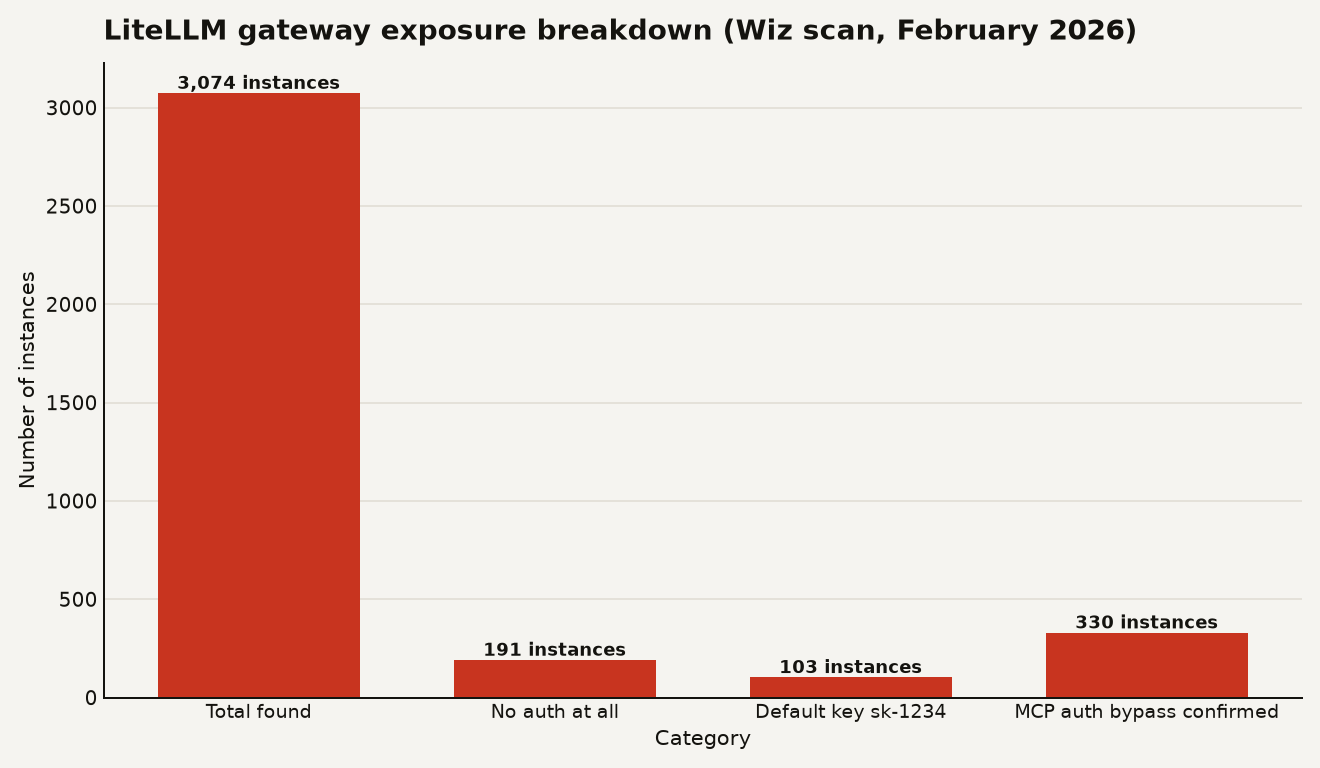
Nearly 1 in 10 internet-facing LiteLLM AI gateways accepted the default admin key sk-1234, exposing model provider keys, database credentials, and cloud IAM roles to attackers. CVE-2026-59822 is on CISA KEV and the fix is a config change, not an upgrade.
Data Today Security Desk ·
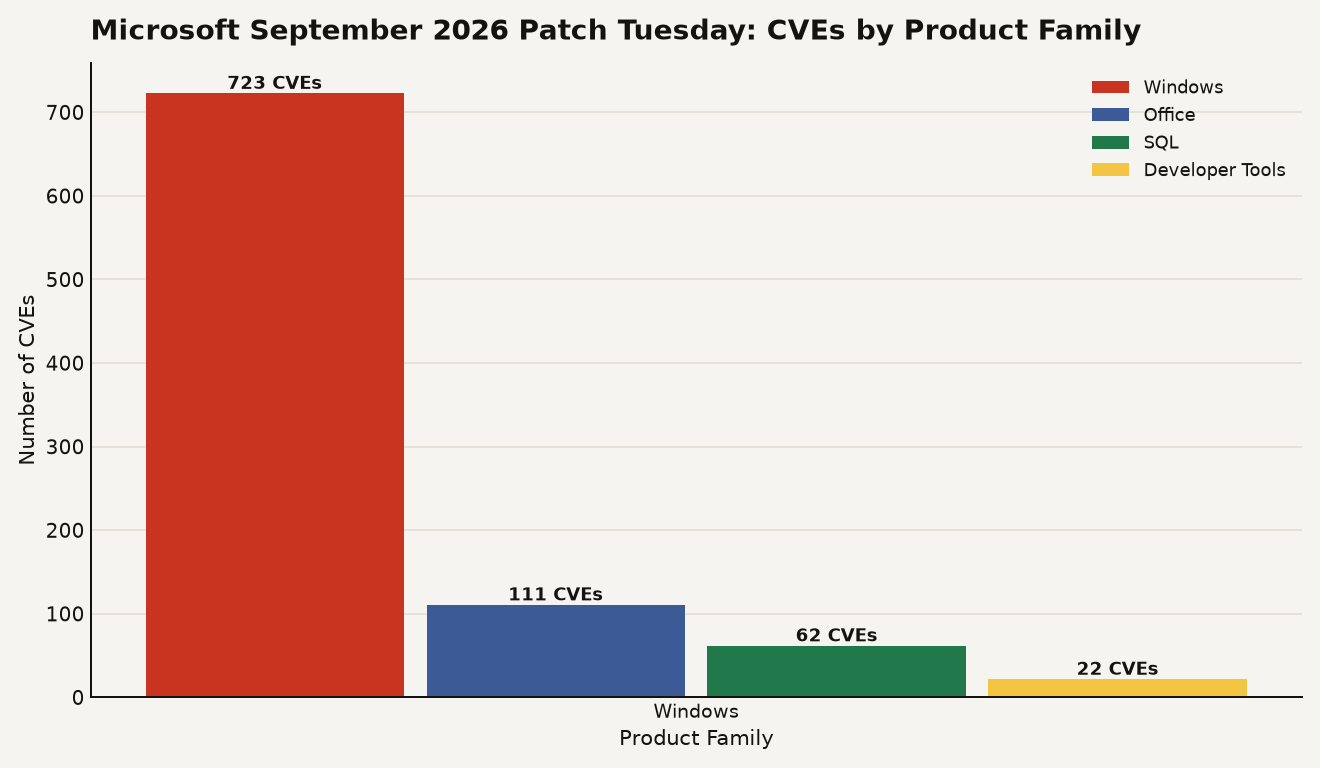
Microsoft shipped a record 974 CVEs in September 2026 Patch Tuesday, including two actively exploited Windows zero-days. Operators now face a deployment crisis as patch volume overwhelms testing capacity.
Data Today Security Desk ·
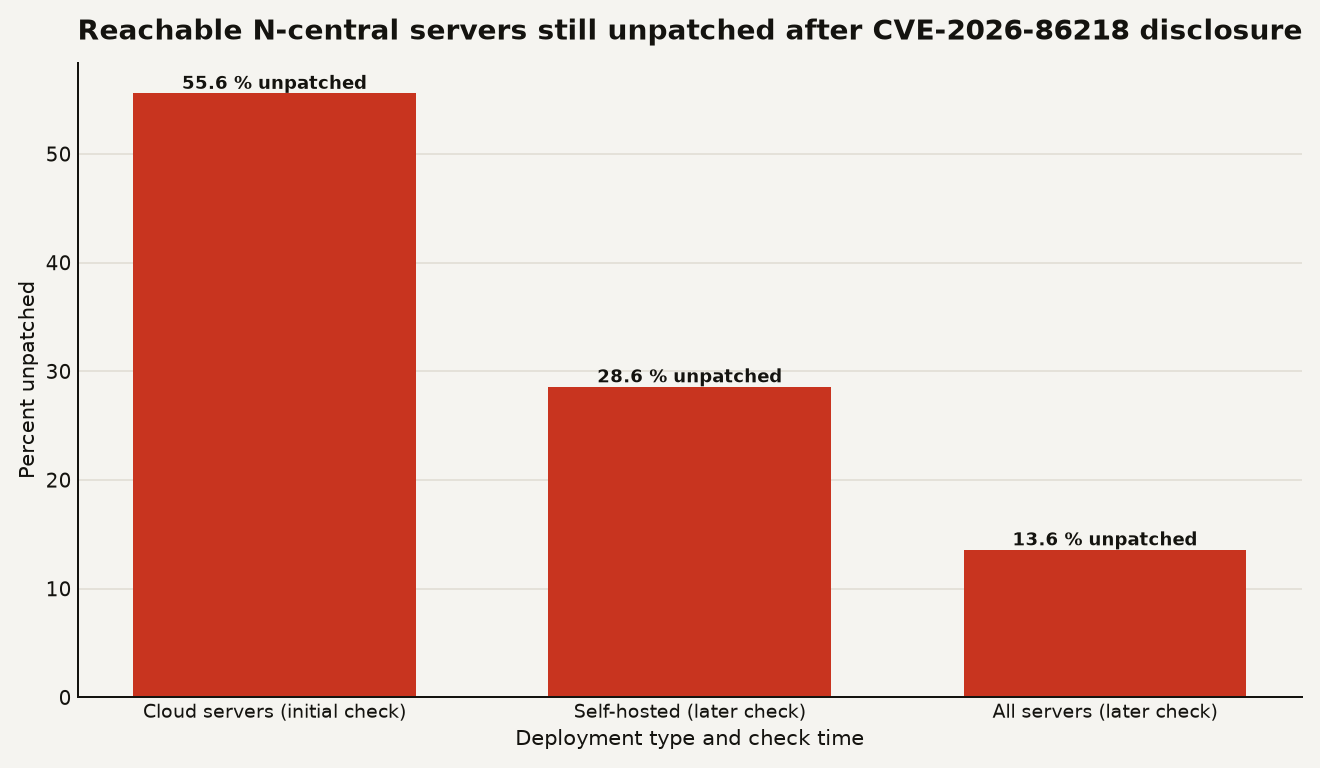
About 1,500 N-central servers are exposed to CVE-2026-86218, a CVSS 10.0 pre-auth RCE, with attacks reported. On-prem needs build 2026.3.1.14 now.
Data Today Security Desk ·
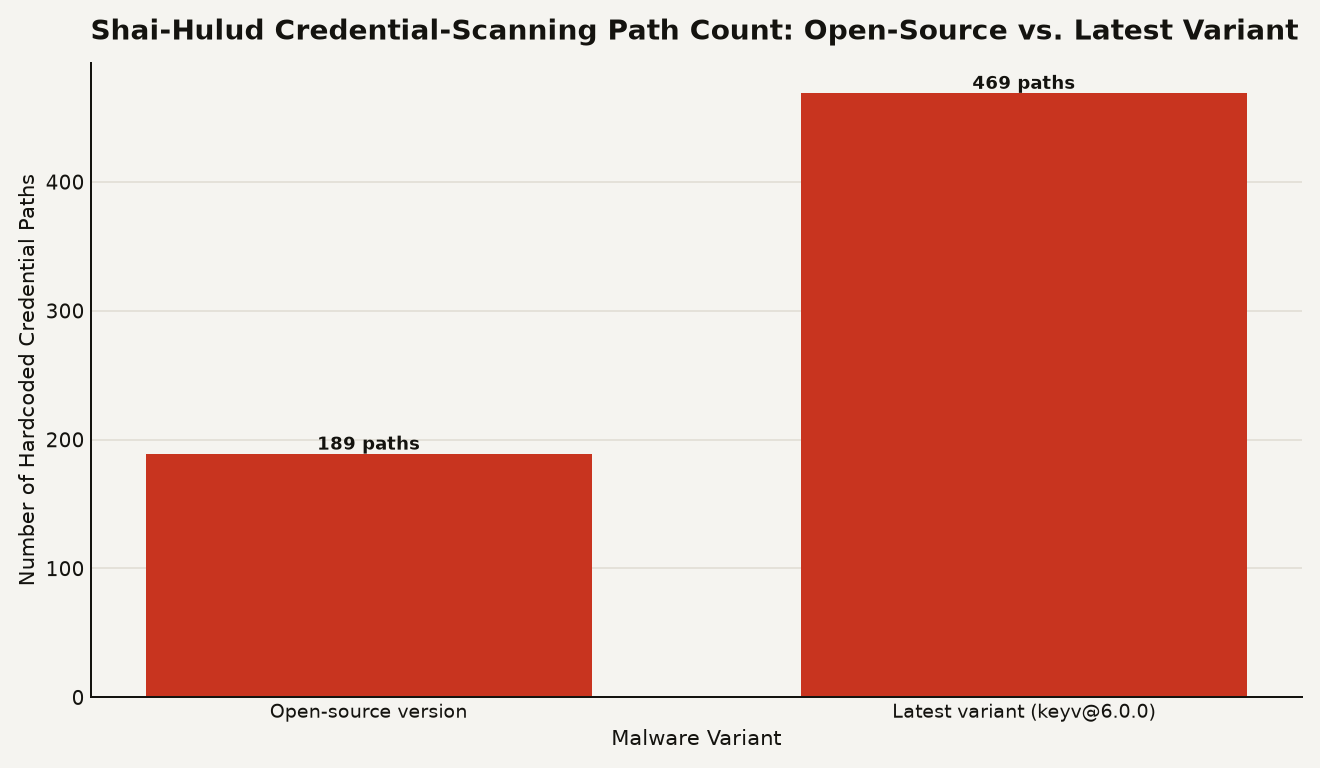
The Shai-Hulud npm infostealer worm expanded from 189 to 469 credential-scanning paths across dev machines, CI/CD, cloud, and AI tool configs after the [email protected] compromise. Rotate everything.
Data Today Security Desk ·
Langflow RCE flaws face active exploitation with over 15,000 successful attacks. Attackers harvest AI provider keys and cloud credentials from exposed instances.
Data Today Security Desk ·
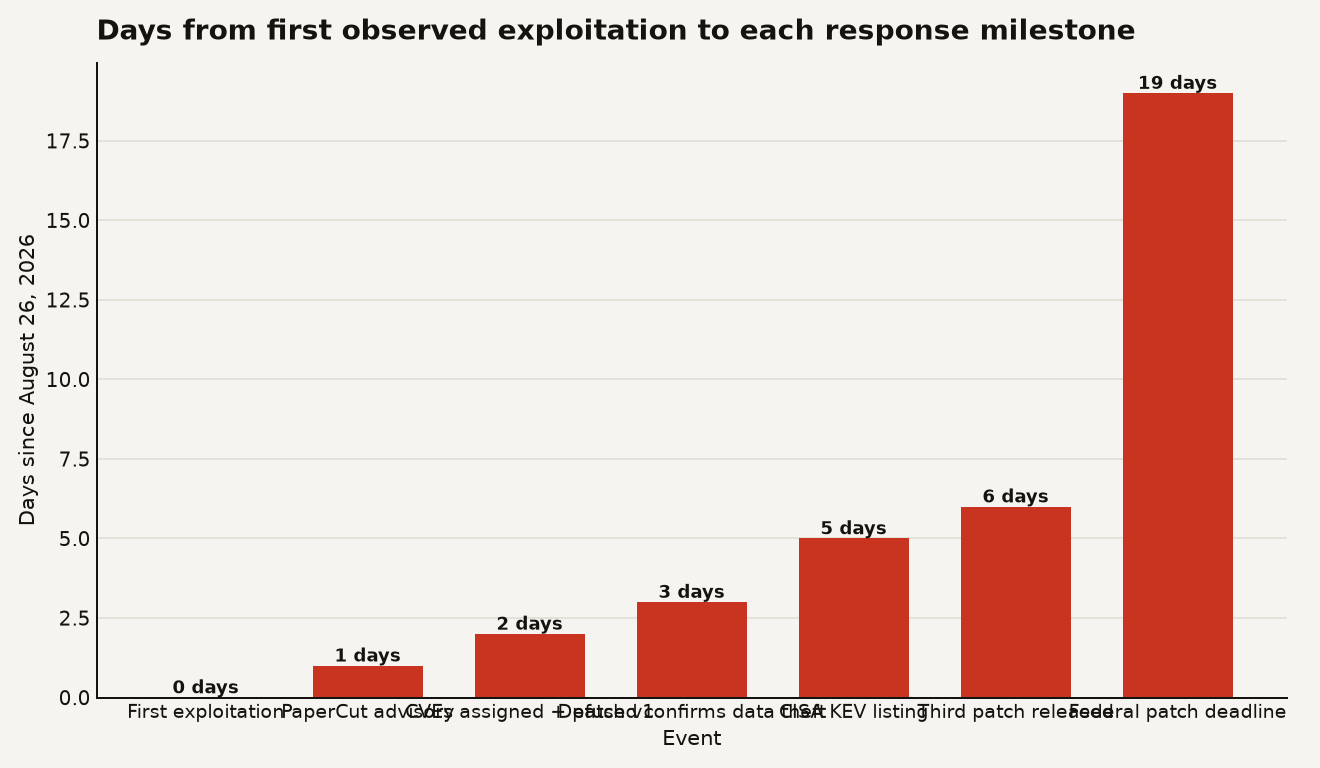
PaperCut NG/MF zero-day chain CVE-2026-81578 and CVE-2026-82078 enables pre-auth RCE on print servers. CISA added both to KEV with a September 14 patch deadline.
Data Today Security Desk ·
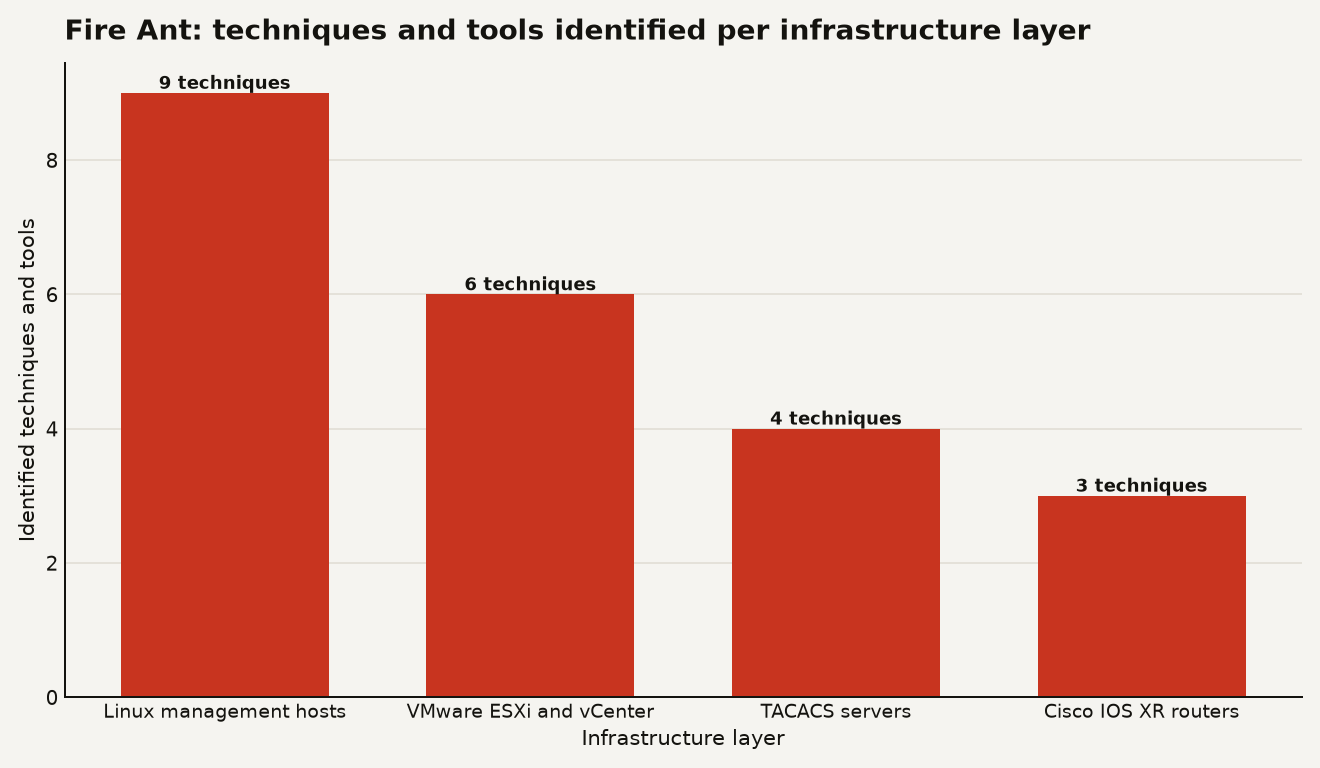
Fire Ant, a China-nexus espionage group, expanded from VMware hypervisors to Cisco IOS XR routers and TACACS servers, hijacking the network trust layer to steal credentials and blind security logging across connected environments.
Data Today Security Desk ·
Web shells are turning up on devices hit through Citrix NetScaler RCE flaw CVE-2026-8452. CISA orders patching by Saturday, August 29.
Data Today Security Desk ·
Next.js patches two critical unauthenticated RCE vulnerabilities in the August 2026 security release. AVIF image optimization and Windows filesystem path traversal both expose self-hosted servers. Upgrade to 15.5.24 or 16.3.3 immediately.
Data Today Security Desk ·
Rated CVSS 9.1, CVE-2026-18963 in Keycloak's password reset flow lets unauthenticated attackers skip email checks and take over any account.
Data Today Security Desk ·
GitLab CVE-2026-19478, a CVSS 9.4 GraphQL injection flaw, lets unauthenticated attackers delete repos and forge merges. It is already exploited in the wild.
Data Today Security Desk ·
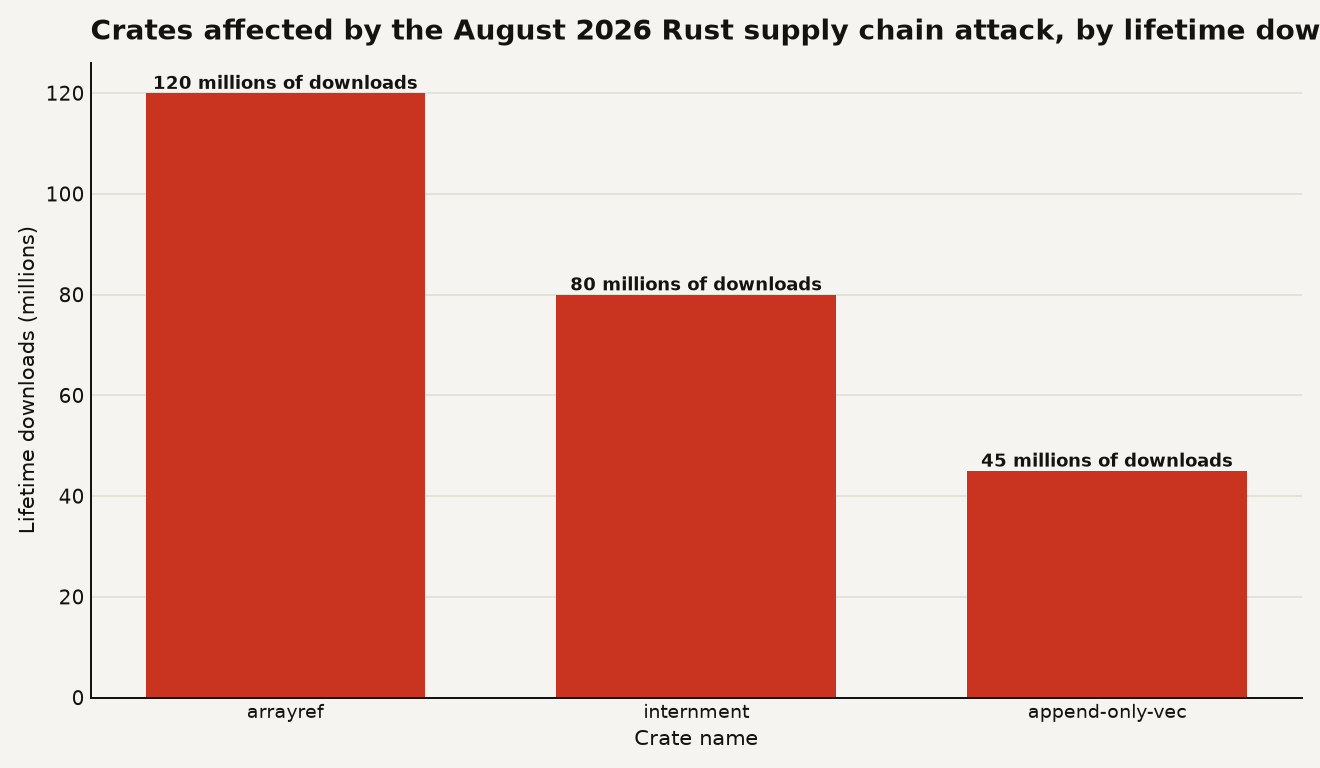
A compromised crates.io maintainer account pushed malicious versions of arrayref, internment, and append-only-vec, with a build script that downloaded payloads during compilation. Here is how to check your lockfile and secure CI.
Data Today Security Desk ·