Engineering
Orkes Conductor pre-auth RCE exploited: patch your workflows
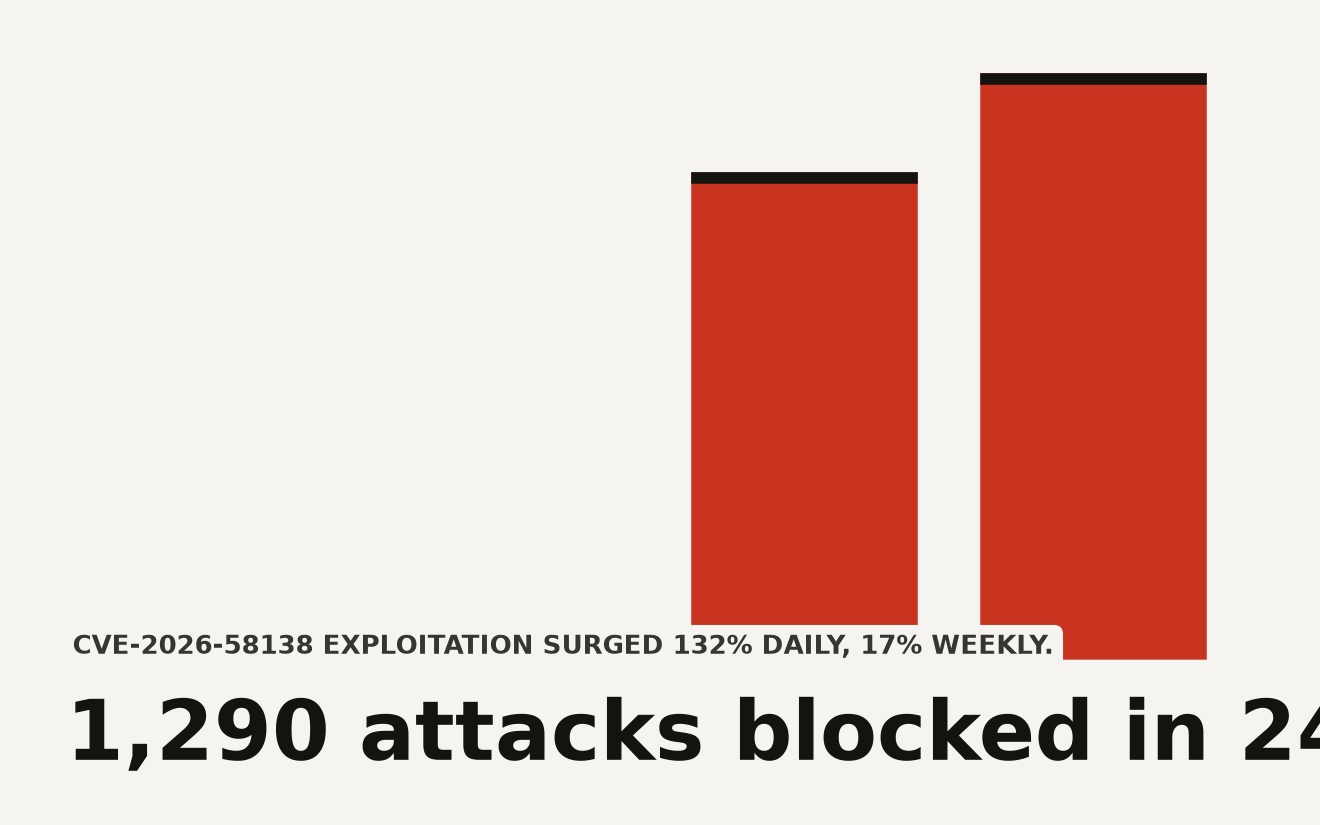
Orkes Conductor CVE-2026-58138 is a CVSS 9.8 unauthenticated RCE in GraalVM script evaluators, actively exploited since August 2026. Upgrade to 3.30.2 now.
High-severity vulnerabilities worth immediate patch decisions, with CVSS context, affected software, and practical mitigation steps.
Orkes Conductor CVE-2026-58138 is a CVSS 9.8 unauthenticated RCE in GraalVM script evaluators, actively exploited since August 2026. Upgrade to 3.30.2 now.
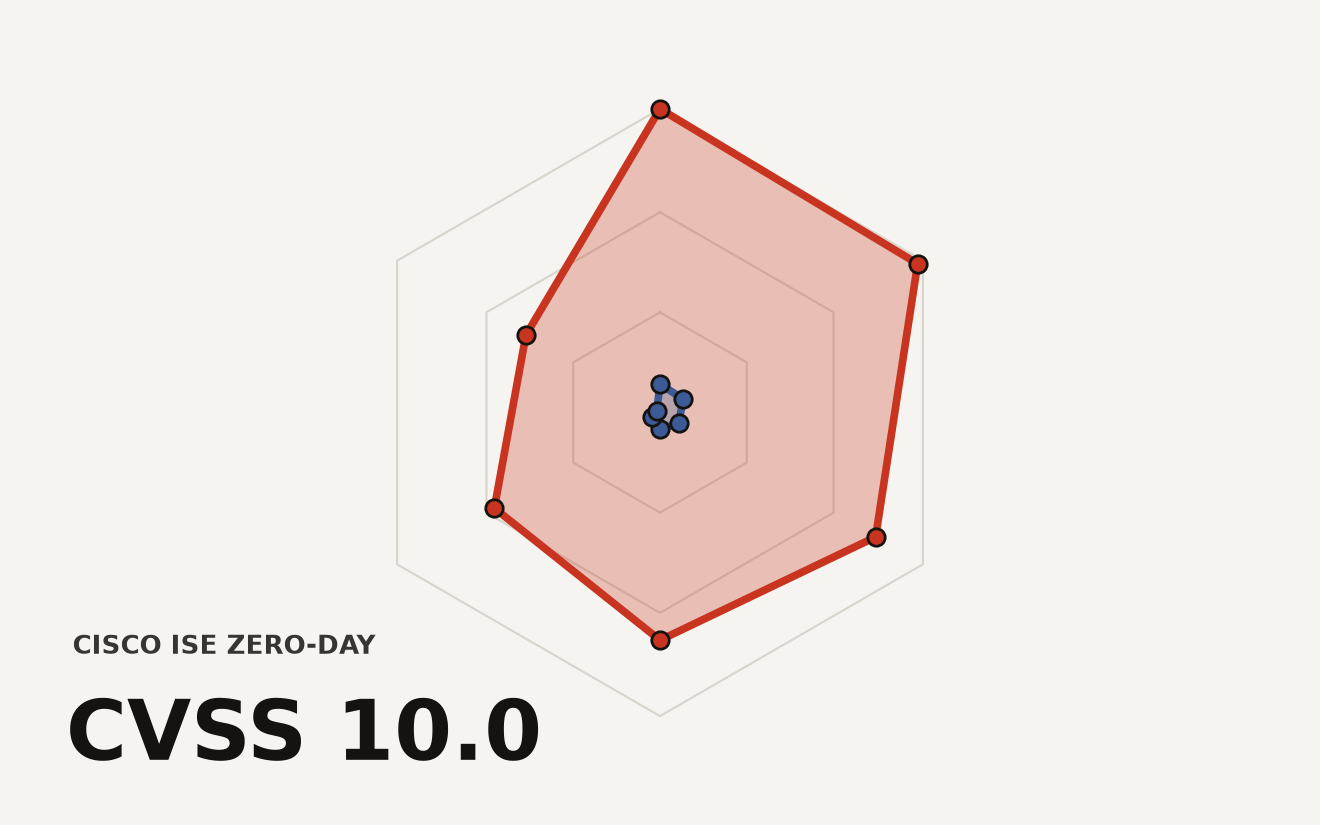
CVE-2026-76460 is a CVSS 10.0 authentication bypass in Cisco ISE and ISE-PIC, actively exploited in the wild. CISA gave federal agencies three days to patch.
CVE-2026-76461 is a root-level SQL injection zero-day in Cisco Secure Email Gateway. CISA confirmed active exploitation and set a 3-day patch deadline.
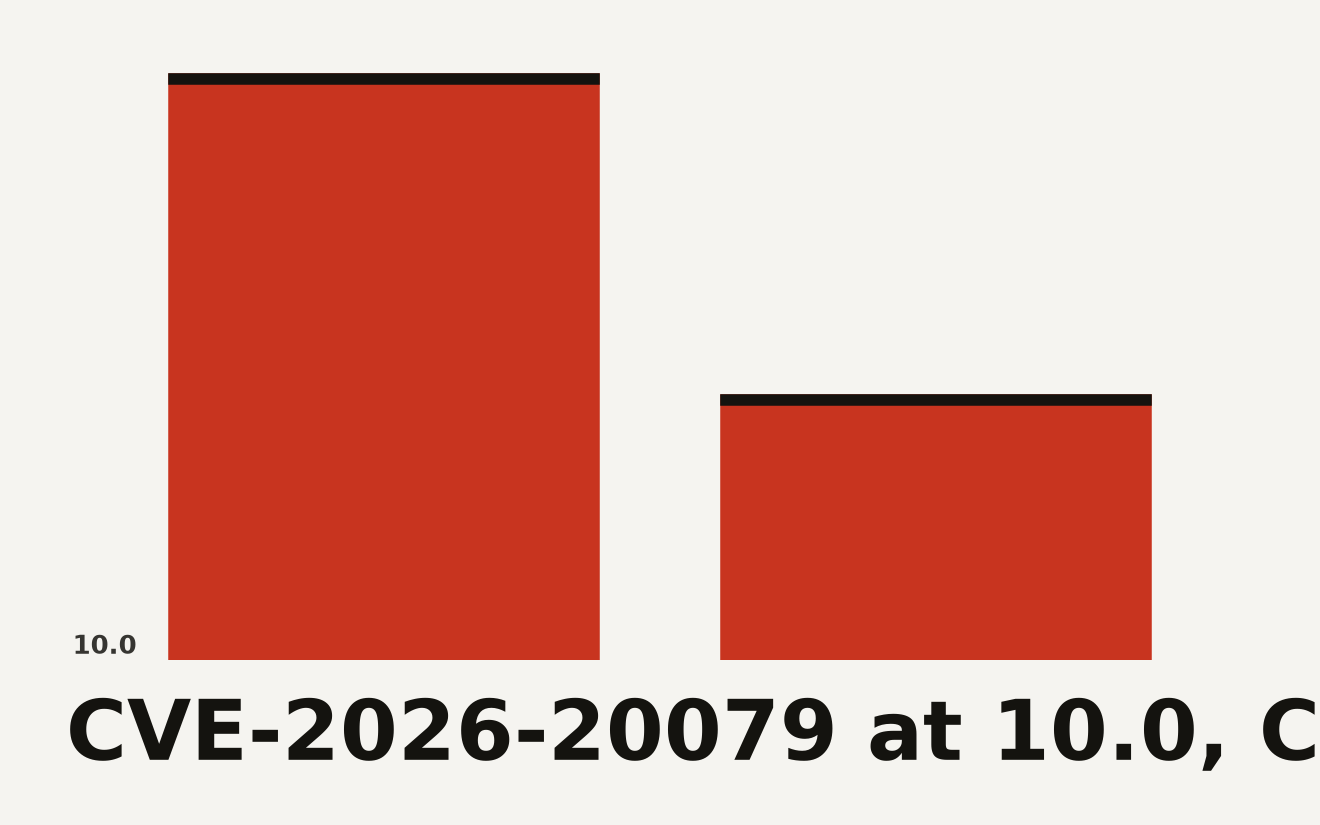
Cisco FMC CVE-2026-20079 lets unauthenticated attackers gain root on firewall managers. Three threat clusters are exploiting it, including Qilin ransomware and suspected Sandworm activity.
Nearly 1 in 10 internet-facing LiteLLM AI gateways accepted the default admin key sk-1234, exposing model provider keys, database credentials, and cloud IAM roles to attackers. CVE-2026-59822 is on CISA KEV and the fix is a config change, not an upgrade.
Microsoft shipped a record 974 CVEs in September 2026 Patch Tuesday, including two actively exploited Windows zero-days. Operators now face a deployment crisis as patch volume overwhelms testing capacity.
CVE-2026-86218 is a CVSS 10.0 pre-auth N-central RCE flaw in N-able's RMM platform. On-prem servers need build 2026.3.1.14 now, with 1,500 exposed online and active attacks reported.
Langflow RCE flaws face active exploitation with over 15,000 successful attacks. Attackers harvest AI provider keys and cloud credentials from exposed instances.
PaperCut NG/MF zero-day chain CVE-2026-81578 and CVE-2026-82078 enables pre-auth RCE on print servers. CISA added both to KEV with a September 14 patch deadline.
Citrix NetScaler RCE flaw CVE-2026-8452 is under active attack with web shells on compromised devices. CISA orders patching by Saturday August 29.
Next.js patches two critical unauthenticated RCE vulnerabilities in the August 2026 security release. AVIF image optimization and Windows filesystem path traversal both expose self-hosted servers. Upgrade to 15.5.24 or 16.3.3 immediately.
CVE-2026-18963 is a critical unauthenticated account takeover in Keycloak's password reset flow, rated CVSS 9.1, letting attackers bypass email verification and set new credentials on any account.
GitLab CVE-2026-19478, a CVSS 9.4 GraphQL injection flaw, lets unauthenticated attackers delete repos and forge merges. It is already exploited in the wild.
MLflow SSRF vulnerability CVE-2026-64849 exposes cloud credentials on 238 servers. Attackers stole secrets from 103 within hours of disclosure.
CVE-2025-62593 in Ray is a critical code injection flaw exploitable via Firefox and Safari, now under active attack. CISA gave federal agencies 72 hours to patch or stop using it.
CVE-2026-55040 is a CVSS 9.1 SharePoint authentication bypass patched in July. Attackers are exploiting it now after Rapid7 released a PoC on August 11.
Hugging Face Diffusers vulnerabilities bypass trust_remote_code in three CVEs rated 8.8 and 7.5, enabling silent RCE from model repos. Patch now.
Fastjson 1.x RCE (CVE-2026-16723) is a critical CVSS 9.0 flaw actively exploited in Spring Boot apps with no official patch available. Block Fastjson 1.x endpoints, migrate to Jackson, and demand autotype safelists.
Check Point SmartConsole CVE-2026-16232 is a critical authentication bypass with a CVSS of 9.3, actively exploited and listed in CISA KEV. Patch your Security Management servers now.
CVE-2026-50522 is a critical SharePoint RCE flaw with CVSS 9.8 that attackers exploit to steal machine keys for persistence after patching.
ServiceNow CVE-2026-6875 is a CVSS 9.5 pre-auth sandbox escape RCE in the AI Platform, now actively exploited. Patch self-hosted instances immediately.
LegacyHive is a public Windows zero-day that escalates standard users to admin on patched systems. No CVE or patch yet, but MDE detection queries exist.
wp2shell is a pre-authentication remote code execution chain in WordPress Core. Two CVEs let anonymous attackers run code on 6.9 and 7.0 sites with no plugins.
Two SonicWall SMA 1000 zero-day vulnerabilities including a CVSS 10.0 SSRF are under active exploitation. CISA KEV-listed with a July 17 patch deadline.
A critical Gitea Docker auth bypass, CVE-2026-20896, lets attackers impersonate any user with one HTTP header. Over 6,200 instances are exposed online.
Bad Epoll (CVE-2026-46242) is a Linux epoll use-after-free giving unprivileged users root on v6.4+ kernels and Android. No workaround exists. Apply patch a6dc643c6931 now.
SharePoint CVE-2026-45659 is an actively exploited RCE risk in CISA KEV. Patch exposed servers and check compromise now.
SimpleHelp CVE-2026-48558 is an actively exploited auth bypass. Patch 5.5.16 or 6.0 RC2, then hunt for TaskWeaver and Djinn.
Cisco Unified CM CVE is now a patch-or-isolate job: CISA set a June 28 deadline after active exploitation of CVE-2026-20230.
CISA KEV vulnerabilities are a live patch queue: four exploited Lantronix and UniFi OS bugs now demand edge inventory and compromise checks.
Splunk CVE-2026-20253 is an actively exploited critical flaw. Patch exposed Enterprise 10.0 and 10.2 nodes by June 21.
Splunk Enterprise flaw CVE-2026-20253 is under active exploitation. Patch by June 21 or disable the PostgreSQL sidecar safely.